For suppliers to companies under NIS 2
Answer one security questionnaire, share it with every customer
Companies under NIS 2 have to manage the security of their supply chain, so they ask their suppliers. You answer one questionnaire, once, and every customer reads the same answers. Free for suppliers.
Programmi e adesioni
How the questionnaire works
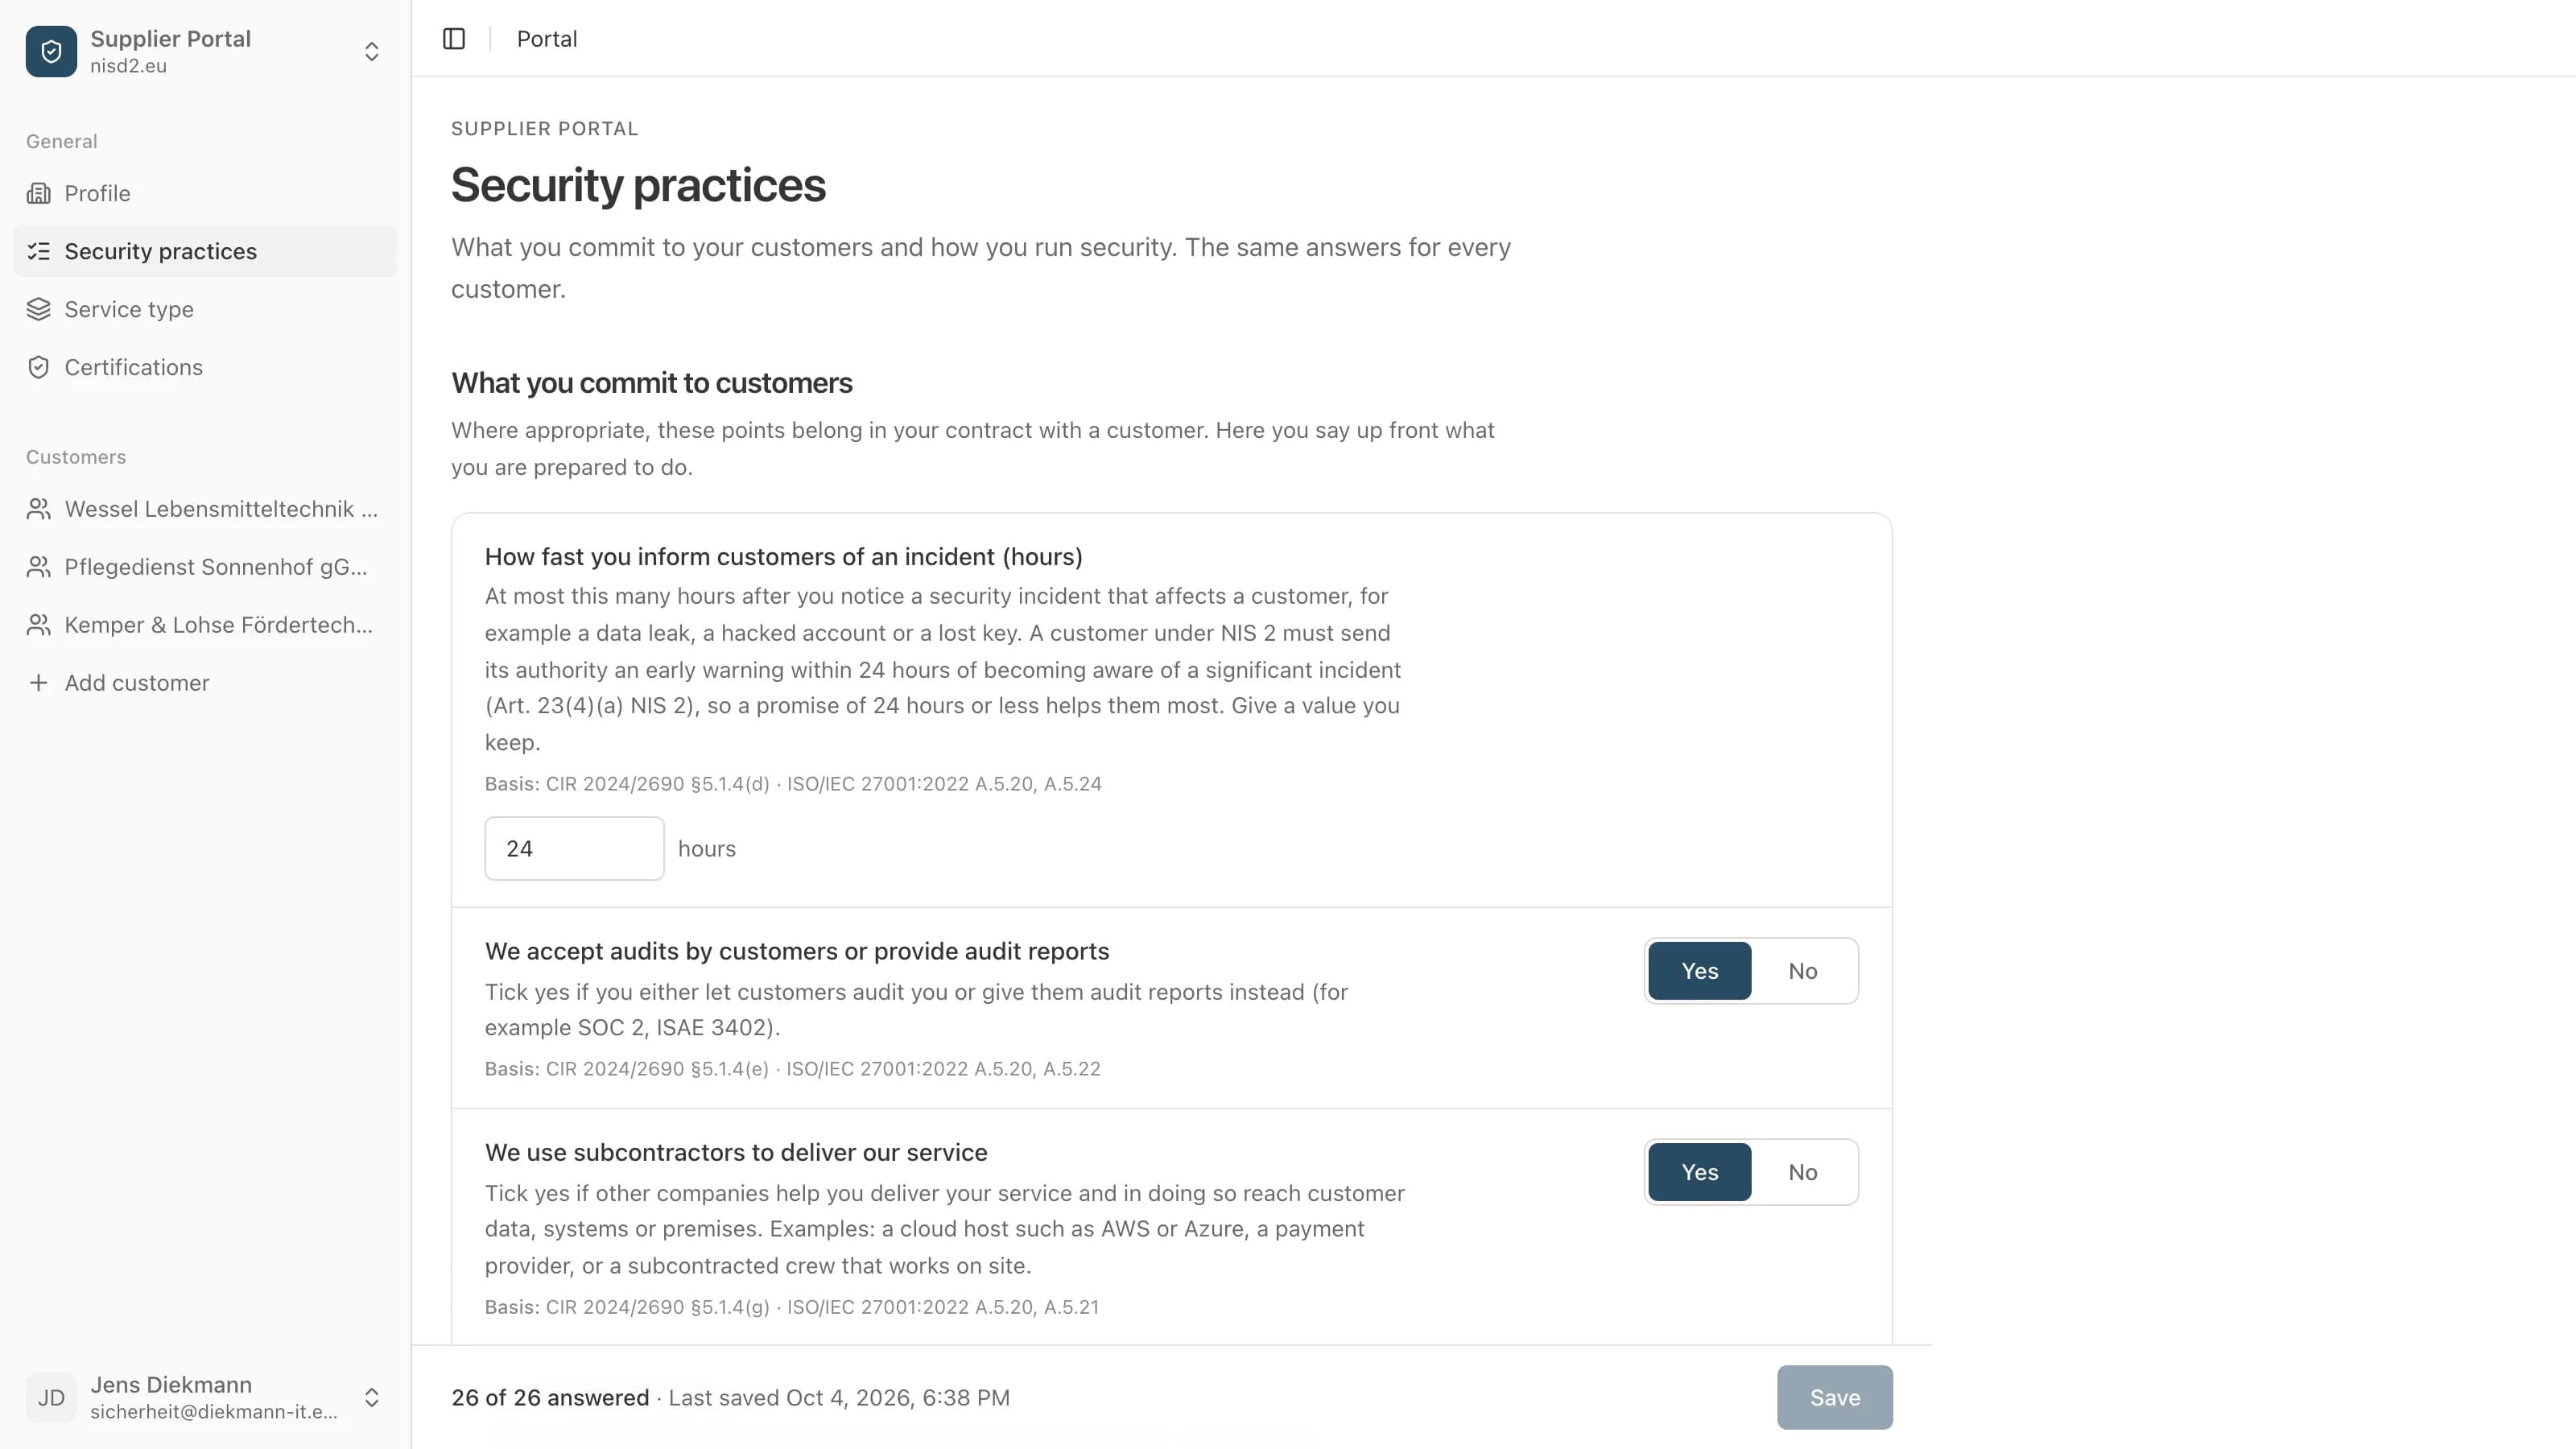
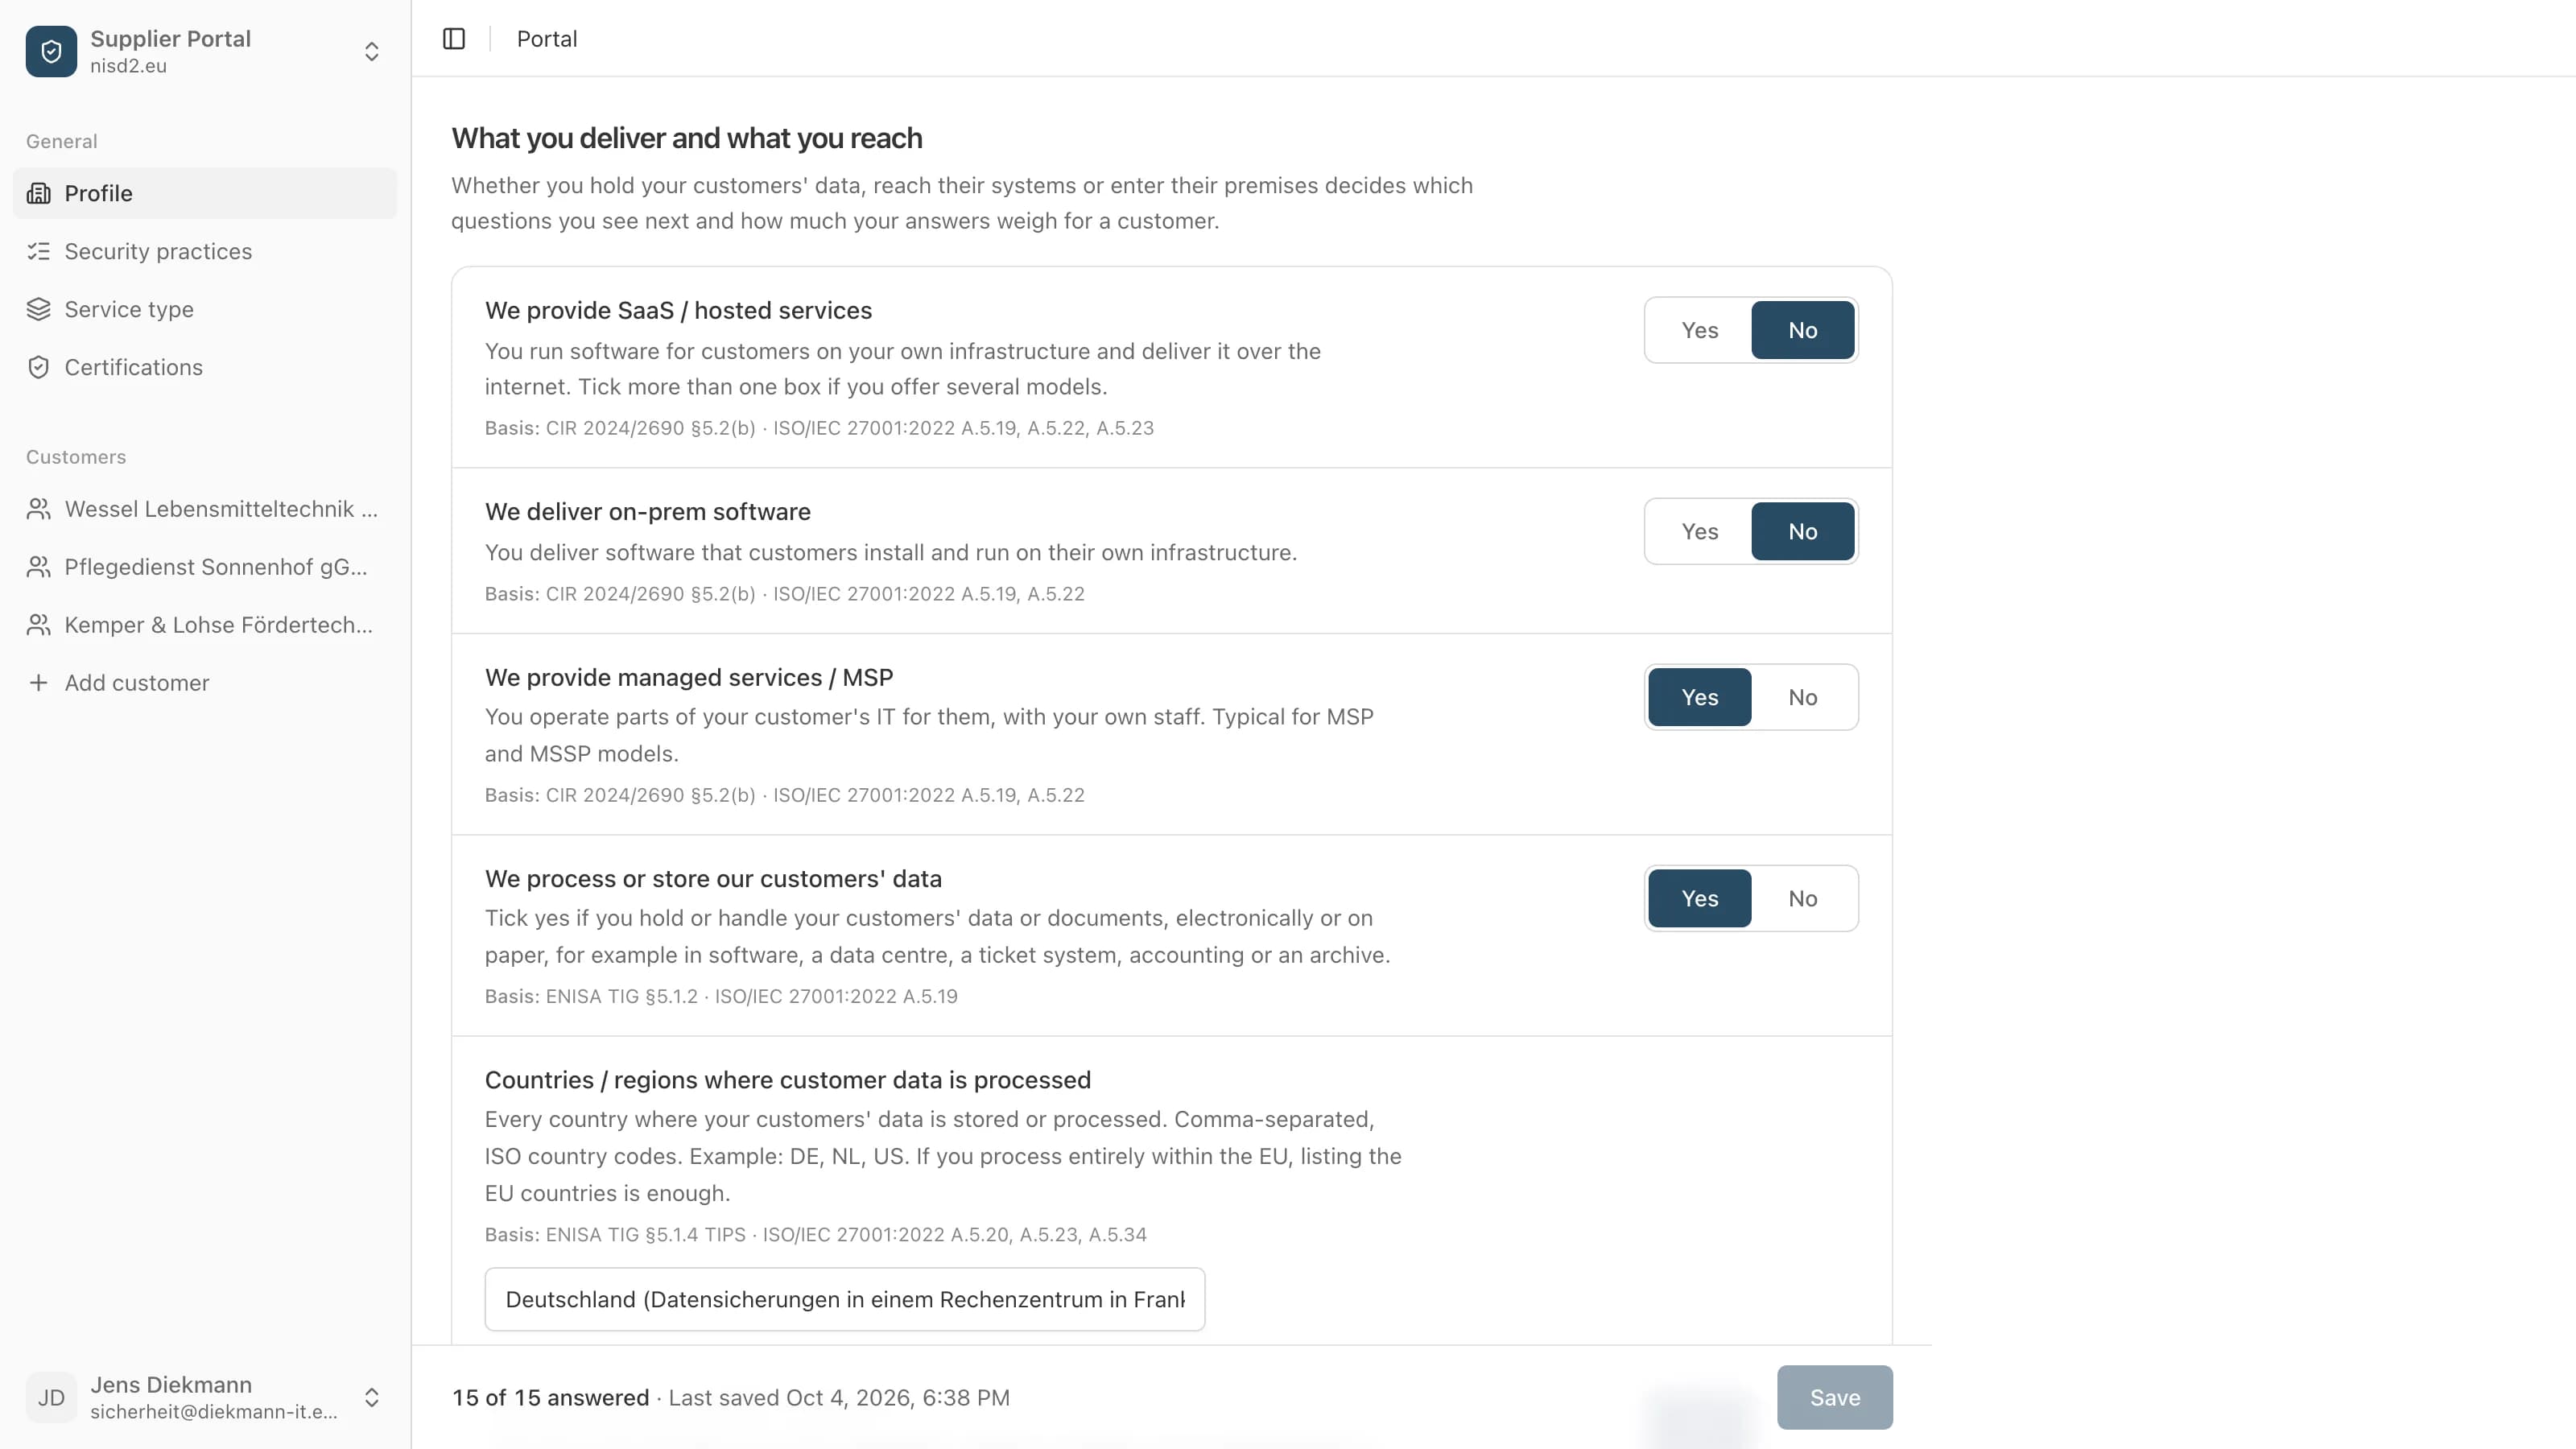
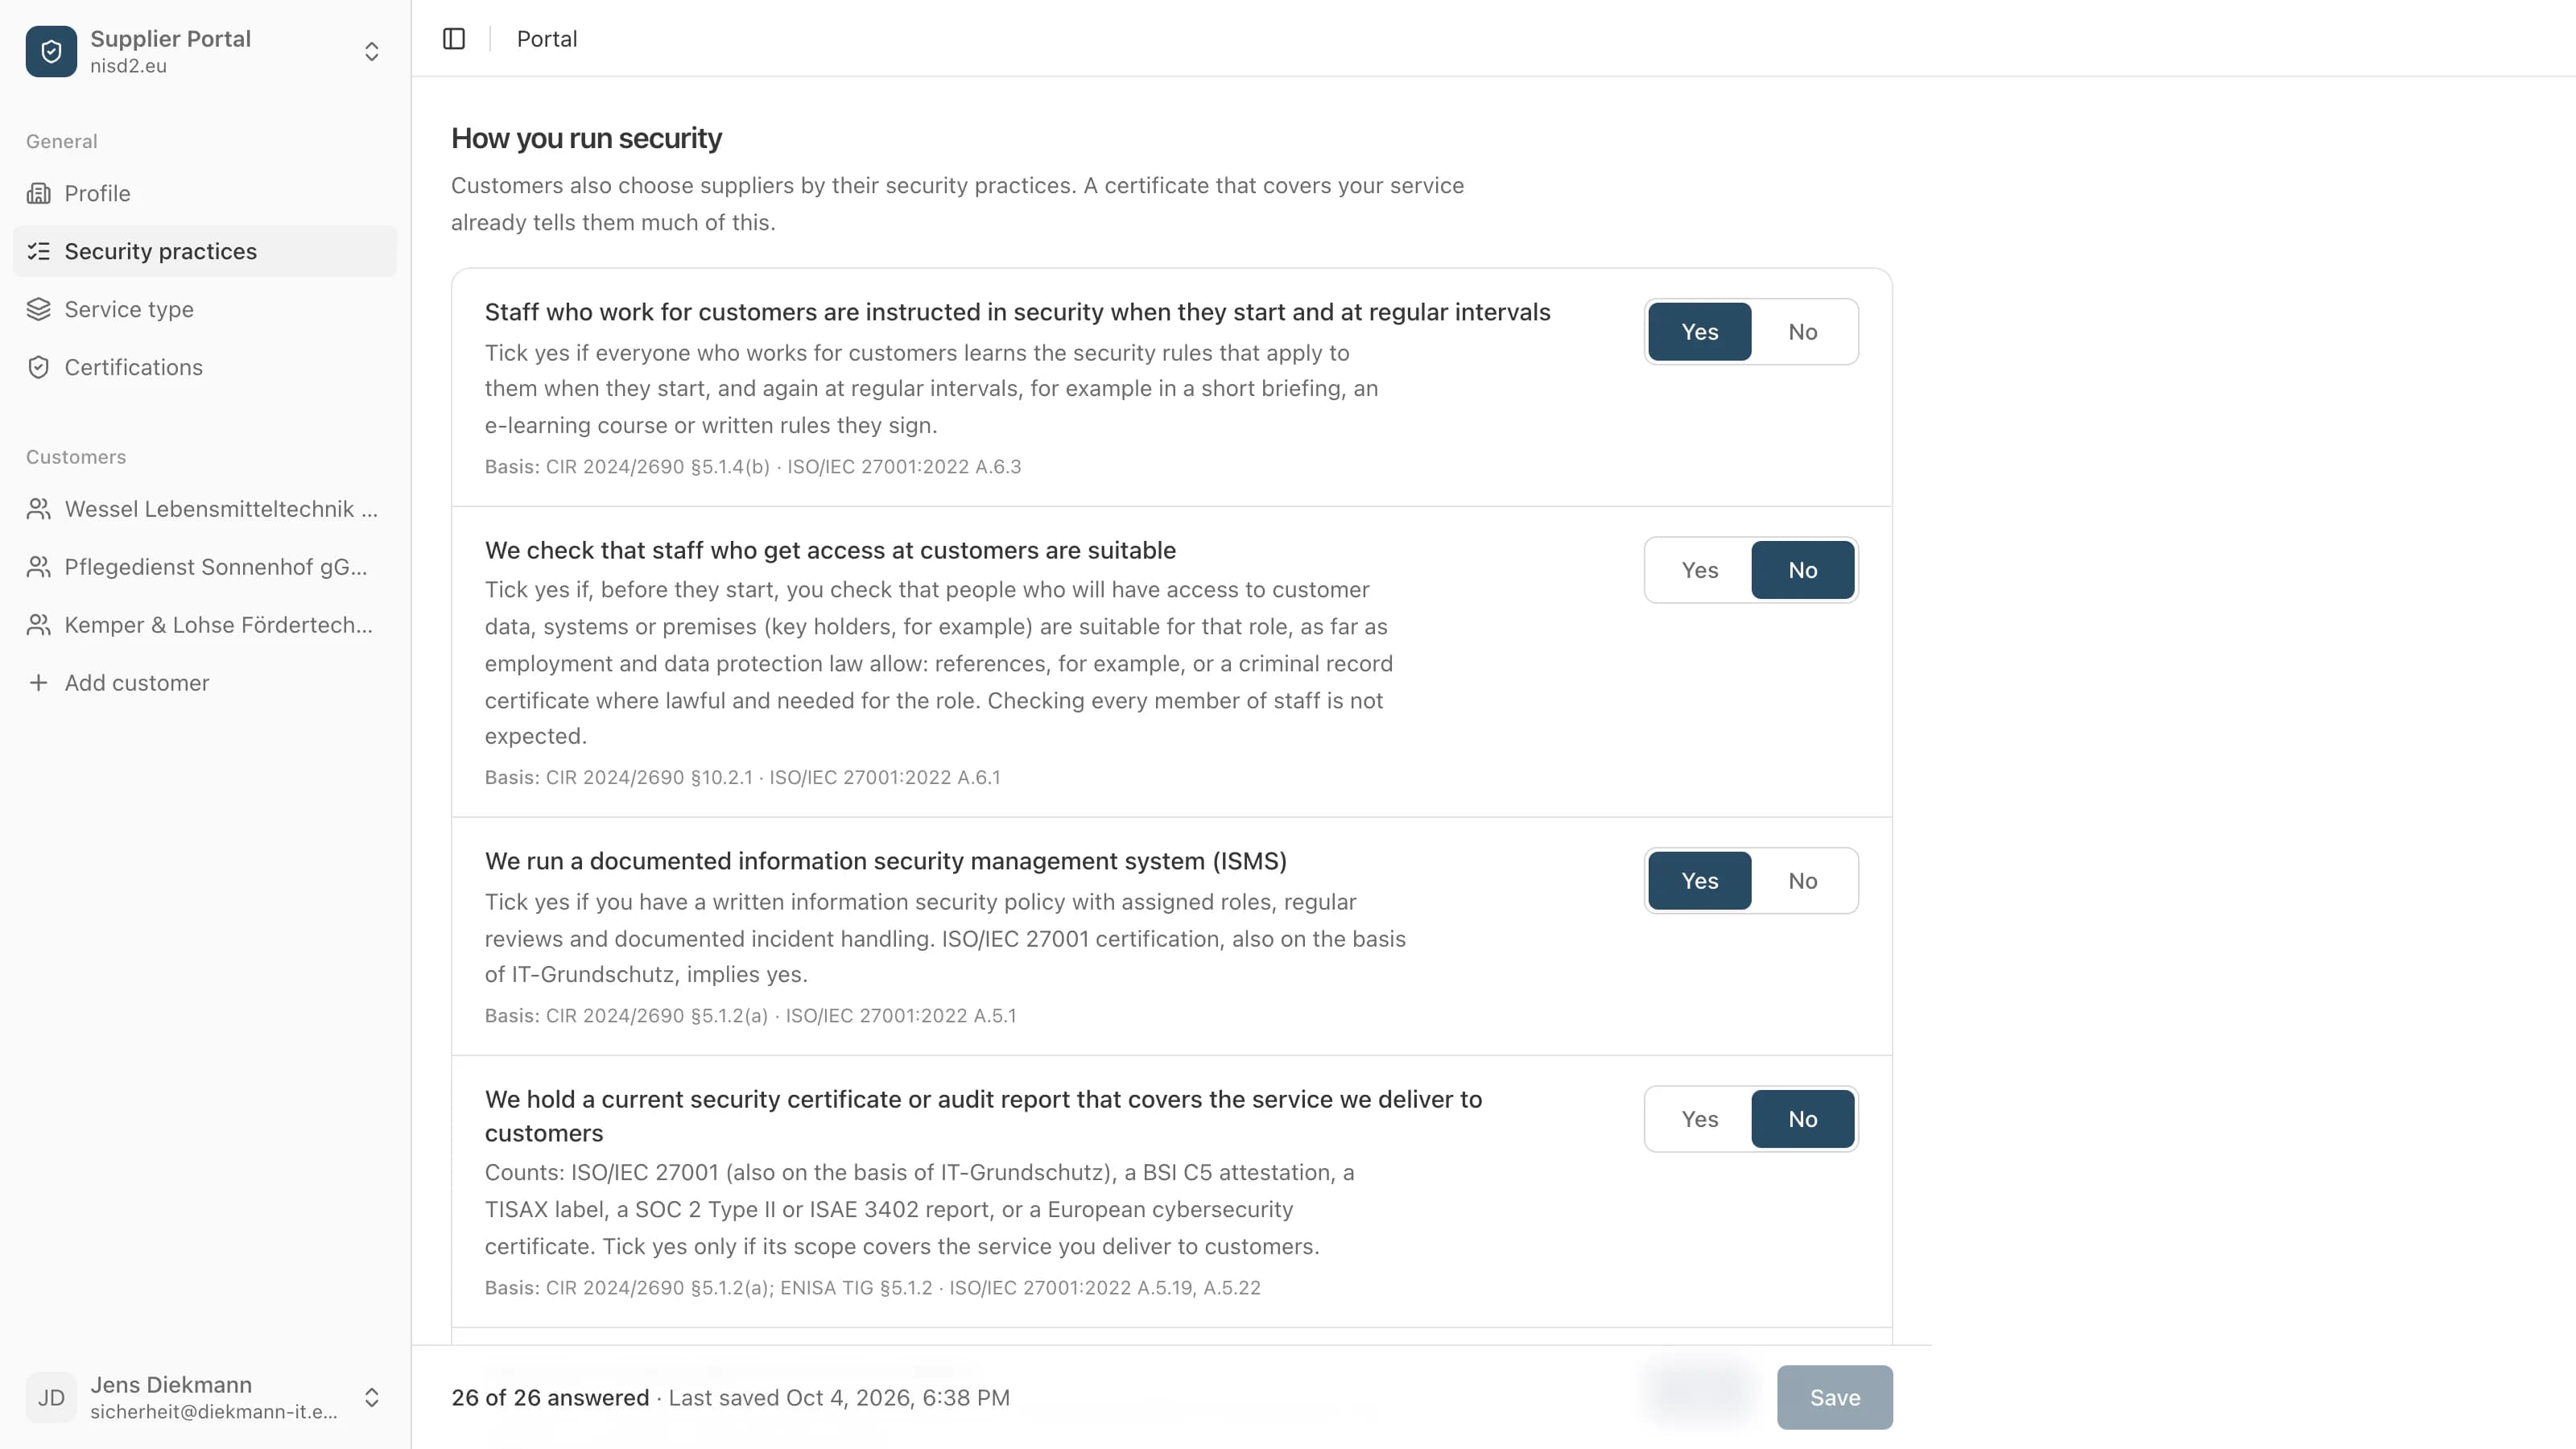
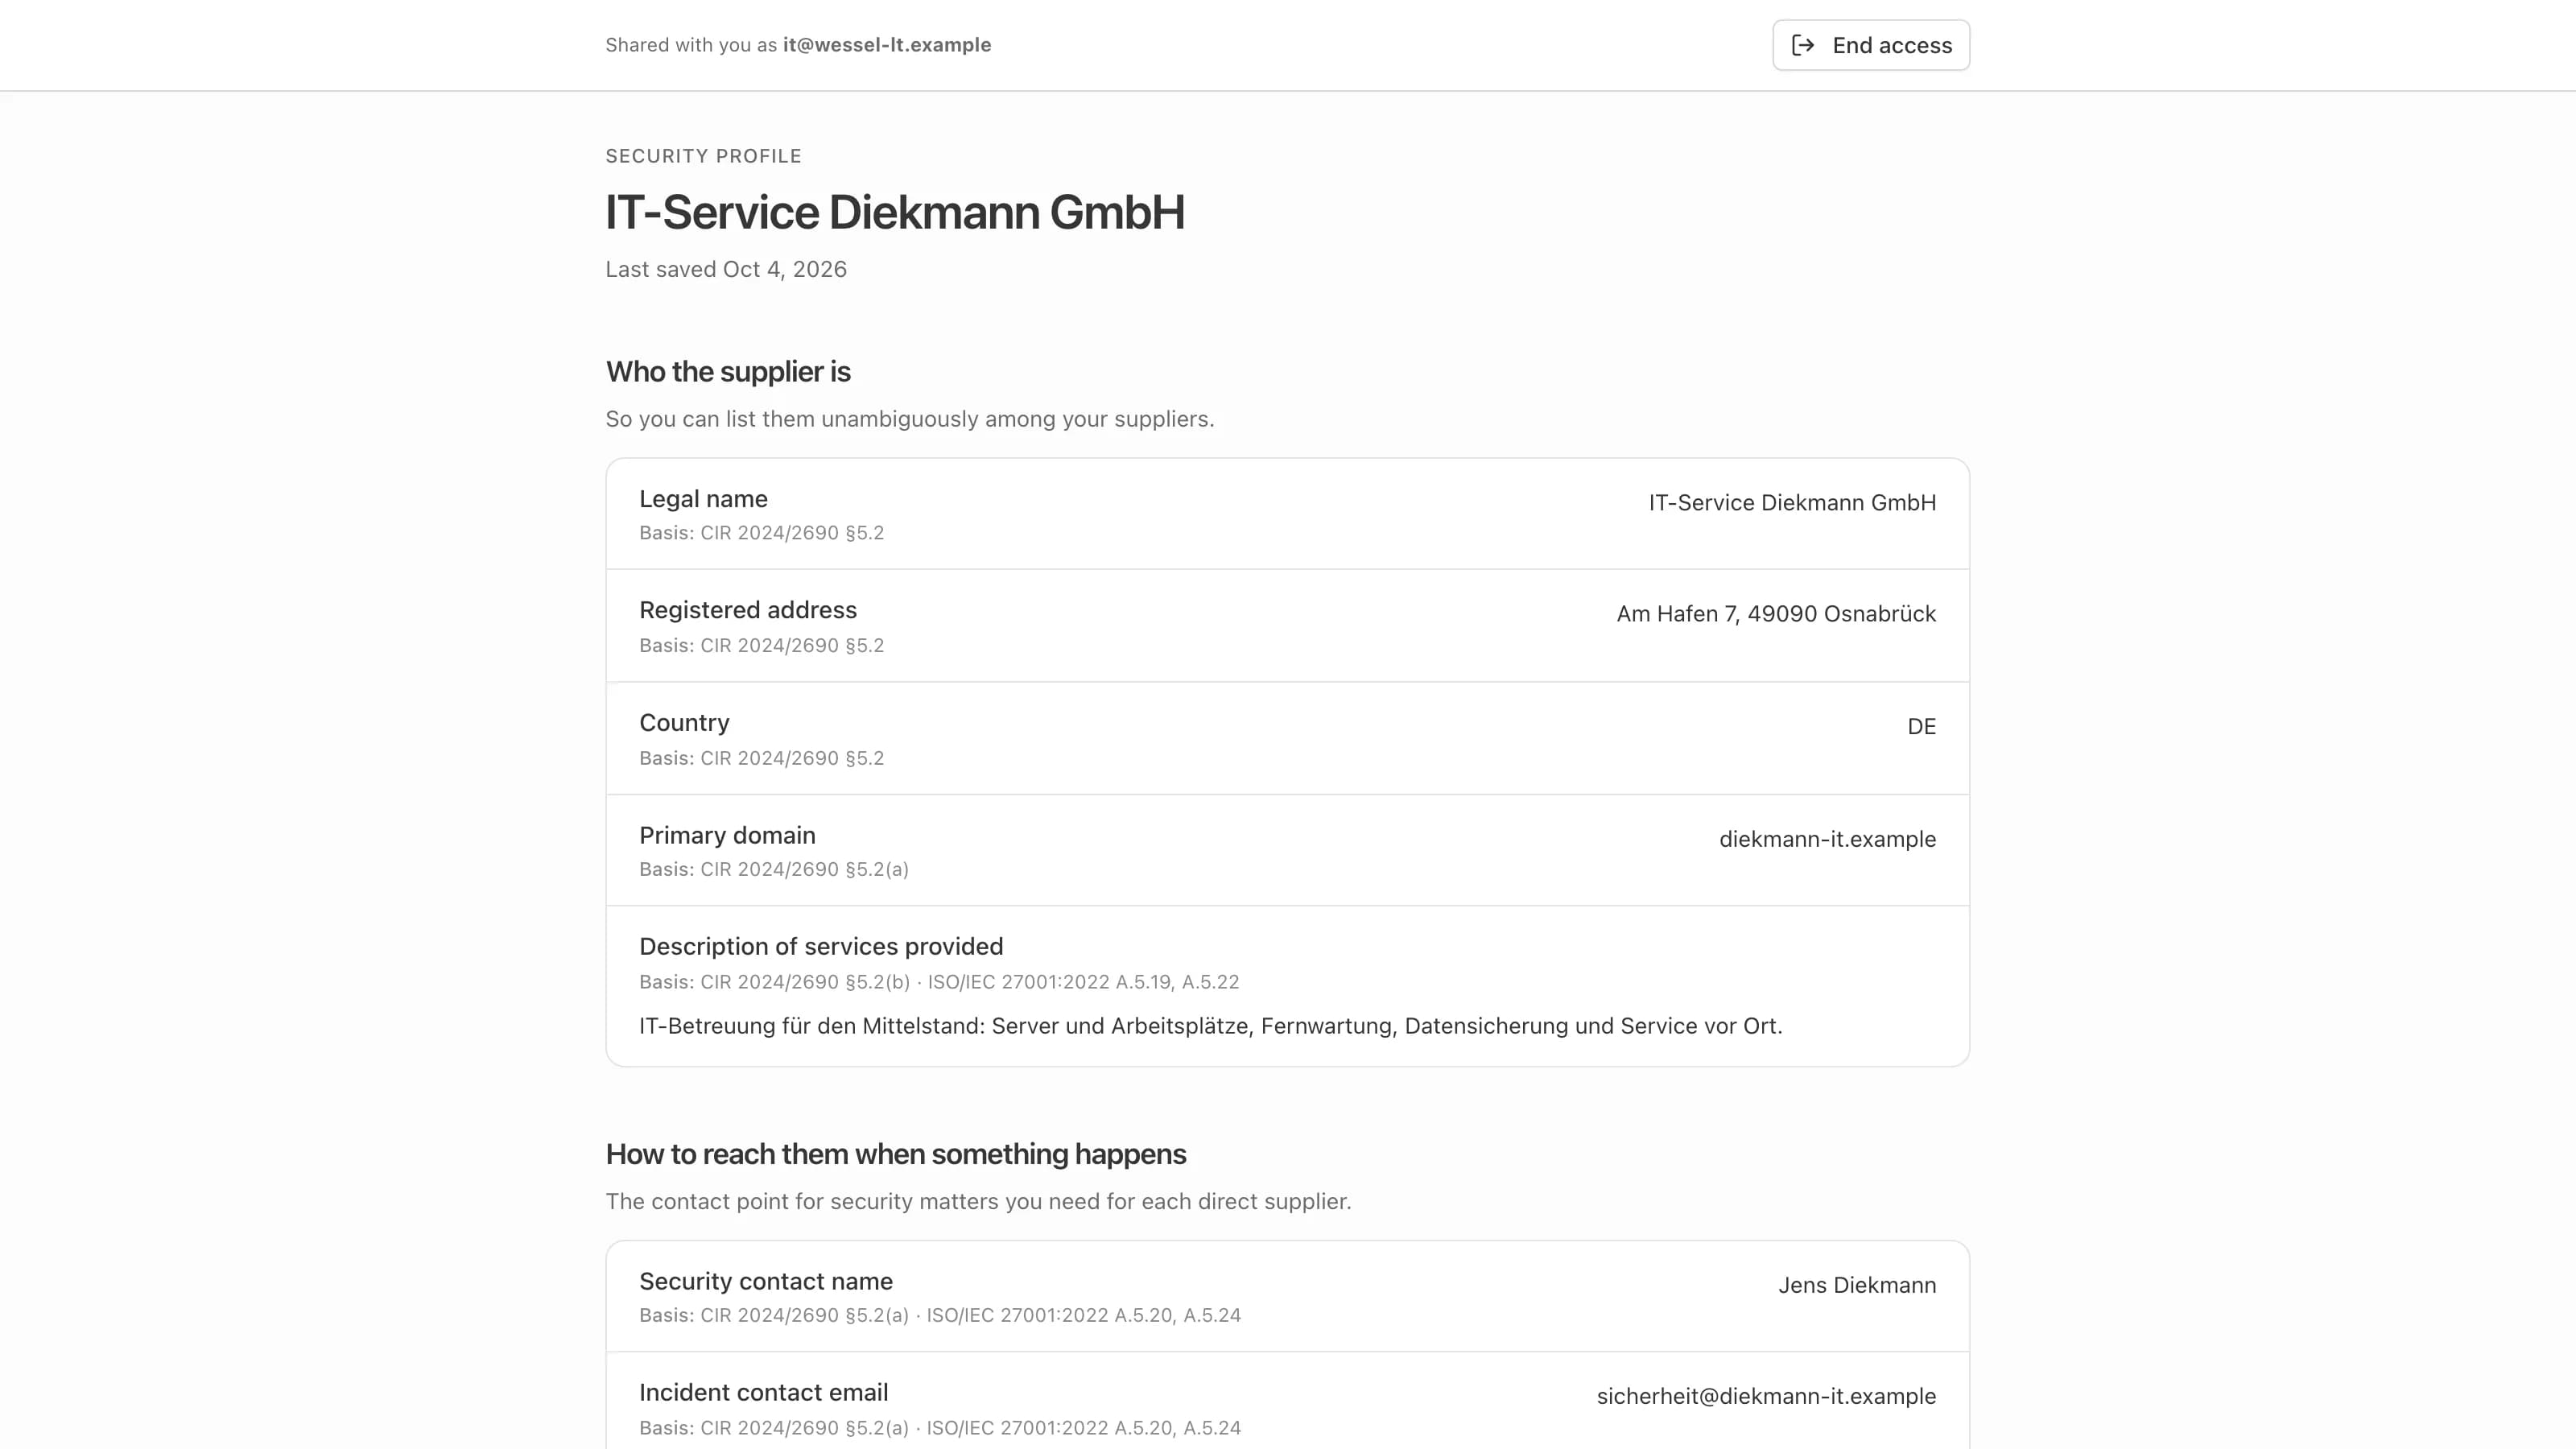
Every picture shows the real app, filled in for made-up sample companies.
- 1
Only the questions that fit you
First you say whether you hold your customers' data, access their systems or enter their premises, and what service you provide. After that you see only the questions that belong to it, and none that do not apply to your service.
- 2
Every question says when to tick yes
Under each question it says in plain words what is meant, with examples. Below that, what the question rests on, mostly a paragraph of Implementing Regulation (EU) 2024/2690, and the matching ISO/IEC 27001:2022 control where there is one.
- 3
Answer once, show every customer
You invite your customers by email. Each opens your answers through a link of their own, without creating an account, and reads the same answers as everyone else. Nothing is public: no profile page, nothing for search engines. You can take the access back at any time.
- 4
Customers on nisd2.eu have you in their supplier register
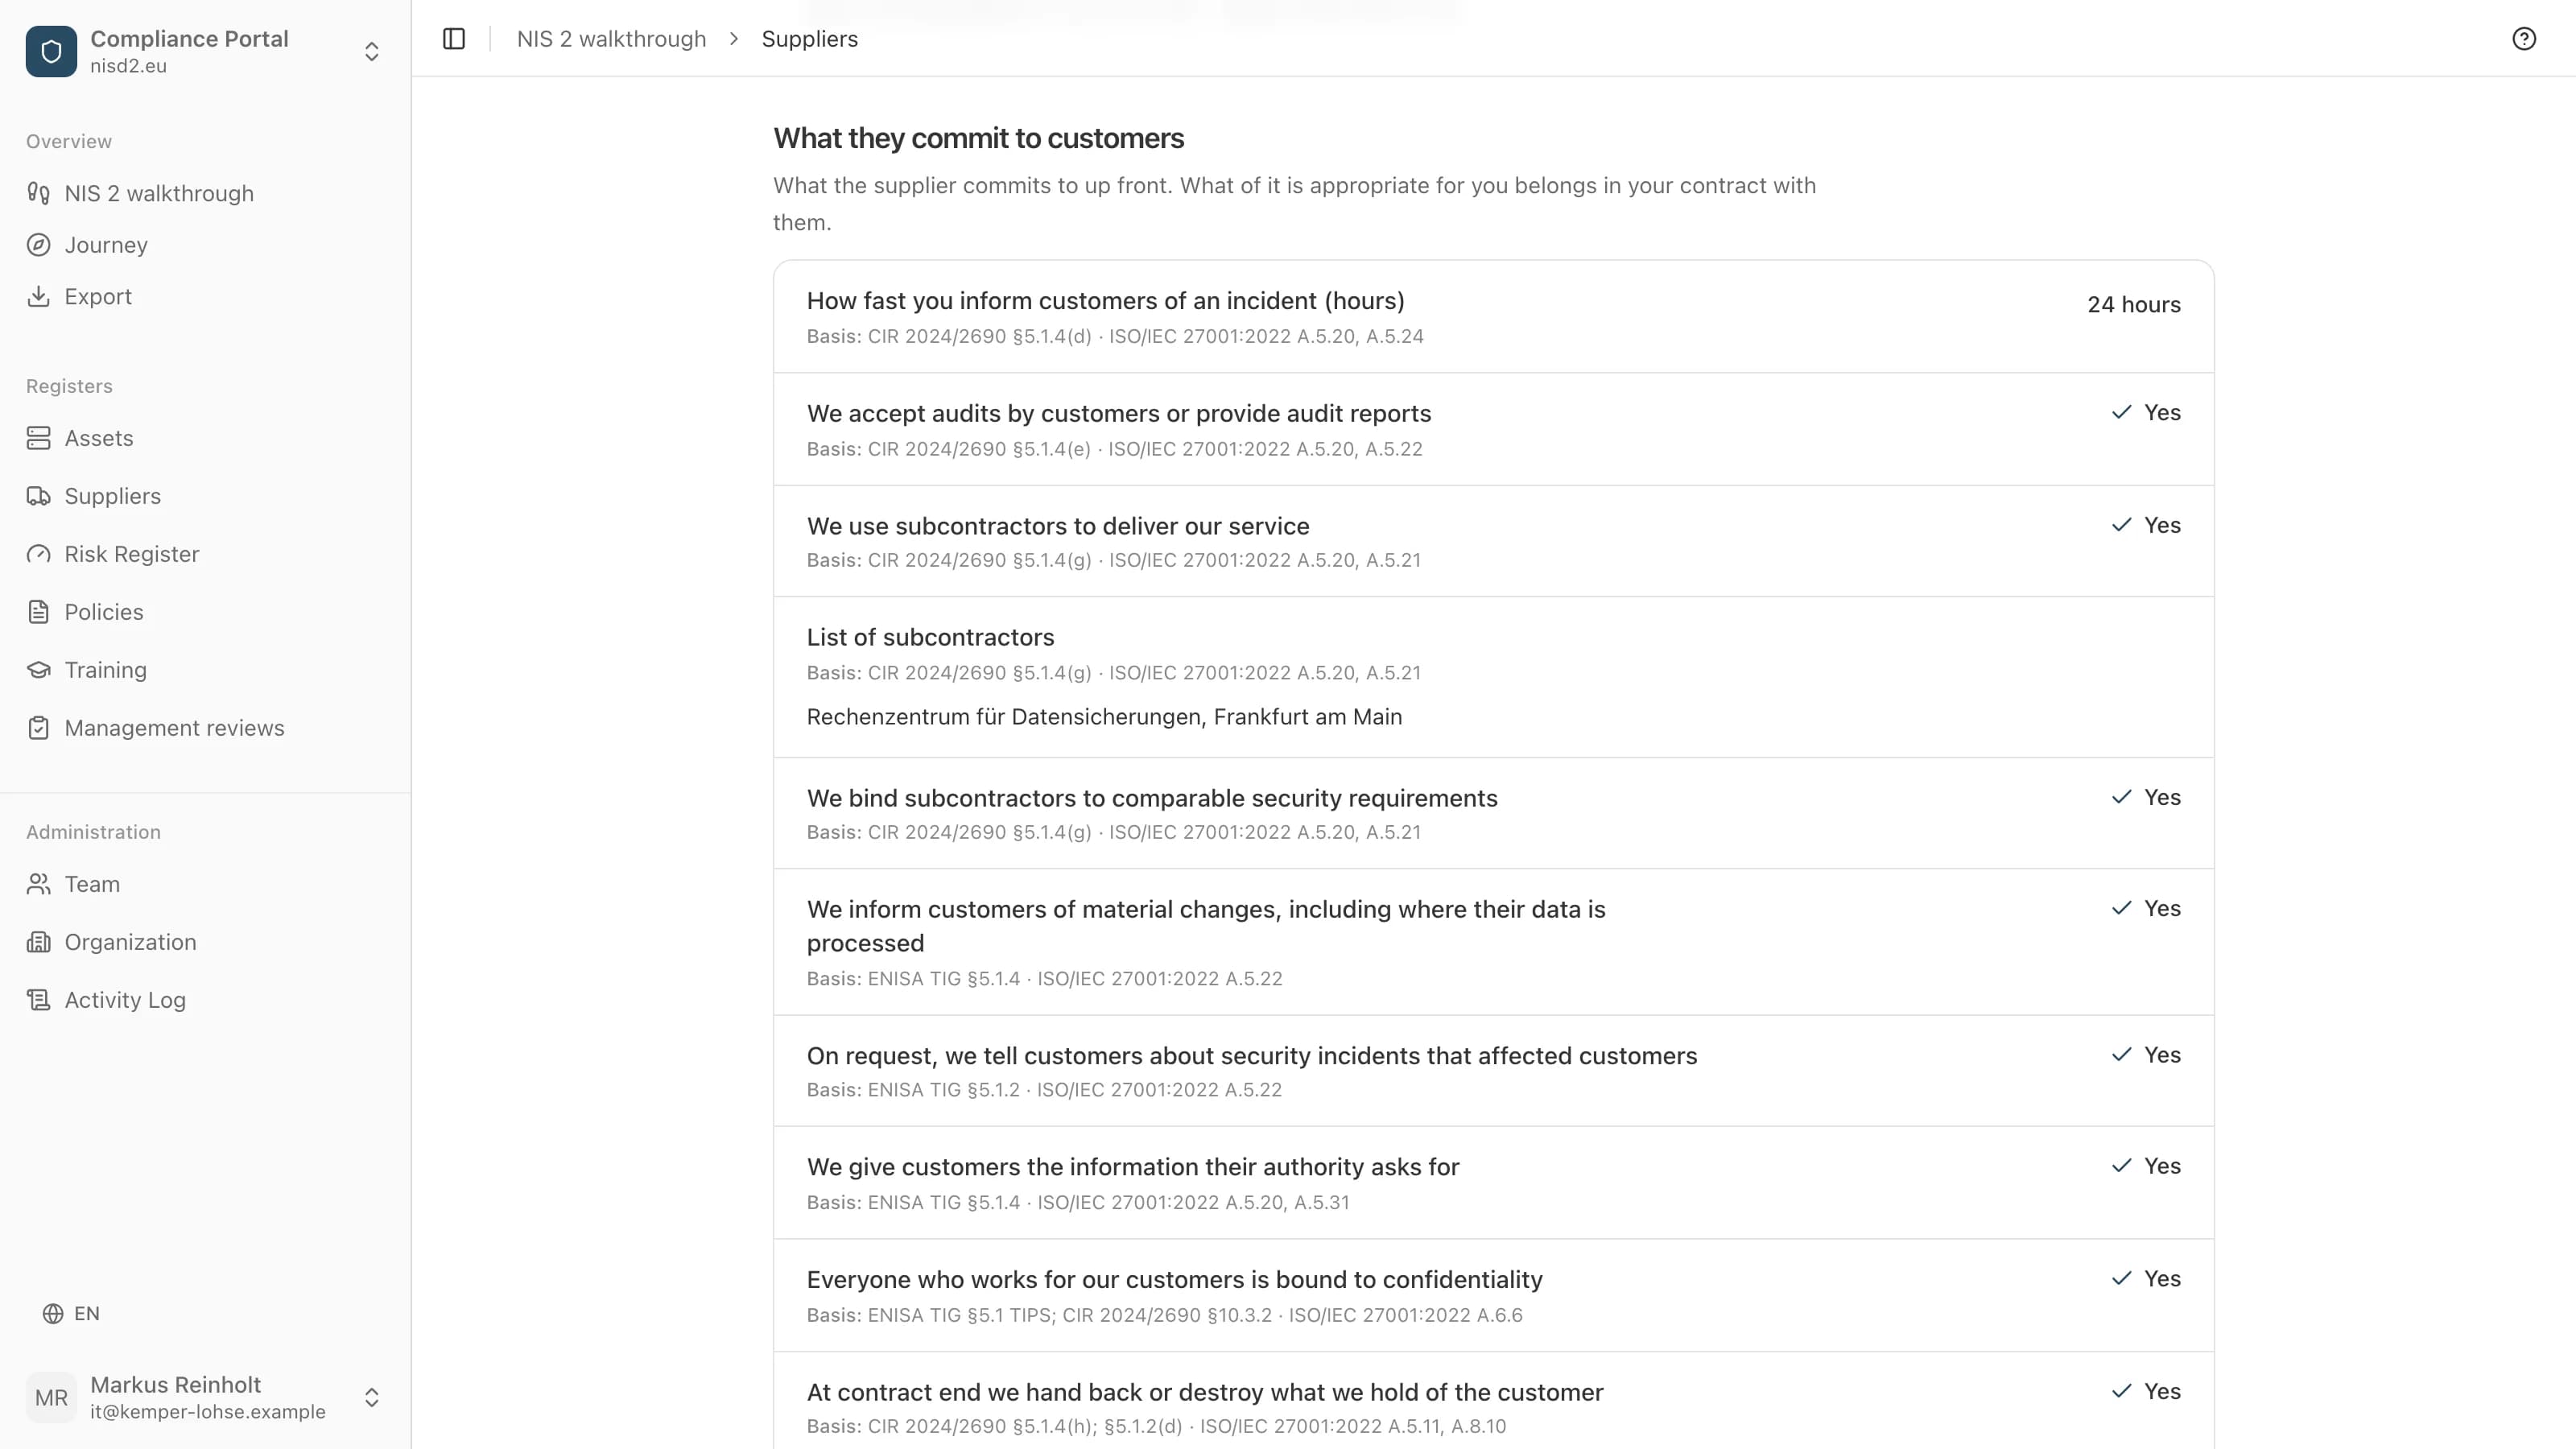
If your customer uses nisd2.eu itself, it requests your answers in the portal. From then on it opens them from its supplier register, where it keeps its suppliers under NIS 2.
- 5
Change it in one place
When a subcontractor is added or an answer changes, you change it once in the portal. Every customer always reads the current version, with the day of your last change.
Cosa ti viene chiesto dipende da ciò a cui accedi presso i tuoi clienti.
Ogni fornitore risponde a 21 domande. Nel profilo indichi se conservi dati dei tuoi clienti, accedi ai loro sistemi o entri nei loro locali, e se offri software come servizio, consegni software o gestisci l'IT per i clienti. Il resto ne deriva. Un fornitore che accede a dati, sistemi o locali risponde anche su riservatezza, idoneità del personale con accesso e restituzione alla fine del contratto.
I dati dei tuoi clienti
Dove vengono trattati i dati, l'accordo sul trattamento dei dati, cifratura a riposo e in transito. Più la tua gestione della sicurezza: SGSI, certificato, gestione delle vulnerabilità, piani per incidenti e interruzioni, un secondo fattore per i tuoi account amministratore.
I sistemi dei tuoi clienti
Account personali con un secondo fattore per ogni accesso, manutenzione remota inclusa, e la registrazione degli accessi con diritti di amministratore. Più la stessa gestione della sicurezza prevista per i dati dei clienti.
I locali dei tuoi clienti
Come tieni traccia di chiavi, badge e codici e quali regole di comportamento scritte segue il tuo personale sul posto. Un fornitore che entra soltanto nei locali non riceve domande su SGSI, test di sicurezza o account amministratore.
Software e servizi gestiti
Se offri software come servizio o consegni software: sviluppo sicuro, un modo pubblicato per segnalare le falle di sicurezza, test di sicurezza indipendenti. Per il SaaS anche un secondo fattore per i tuoi clienti e il tempo di ripristino del servizio; per il software consegnato per quanto tempo fornisci aggiornamenti di sicurezza, una SBOM e rilasci firmati. Se gestisci l'IT per i clienti, rispondi alle domande sui test di sicurezza e sulla gestione della sicurezza.
Un'impresa di pulizie con le chiavi vede così 26 domande, un fornitore SaaS che conserva dati dei clienti 39.
„Wir begrüßen aktuelle Vorstöße der Wirtschaft, einen einheitlichen Fragenkatalog für Lieferanten zu erarbeiten, der die Erfüllung der Anforderungen belegt.“
We welcome current initiatives from industry to develop a uniform catalogue of questions for suppliers that demonstrates the requirements are met.
This questionnaire is one such initiative: uniform, open and free to reuse. Suppliers answer it once, and every customer reads the same answers when it manages the security of its supply chain under Art. 21(2)(d) NIS 2.
Only for customers you invite
Your answers are seen only by the customers you invite or whose request you accept. No public profile page, nothing for search engines. Hosted in the EU, with the code open on GitHub.
Start with your profile
Sign in, enter your company name, then answer the questionnaire at your own pace. You invite your customers only when you are ready.
Create supplier profileMore on nisd2.eu
- Supplier portal
What else the portal does: invite customers, store certificates, report incidents.
- Every question with its basis
The whole questionnaire to read, and as a PDF, for Word and as an open schema.
- Open source
The full source code under AGPL-3.0 on GitHub.
Open source
La piattaforma è open source e gratuita se la ospiti tu stesso. Guadagniamo dall'implementazione guidata, non dai tuoi dati. Il codice e gli schemi sono aperti su GitHub, così puoi verificare di persona. Tutto esportabile, nessun lock-in.