For suppliers to companies under NIS 2
Answer one security questionnaire, share it with every customer
Companies under NIS 2 have to manage the security of their supply chain, so they ask their suppliers. You answer one questionnaire, once, and every customer reads the same answers. Free for suppliers.
Programy i członkostwa
How the questionnaire works
Every picture shows the real app, filled in for made-up sample companies.
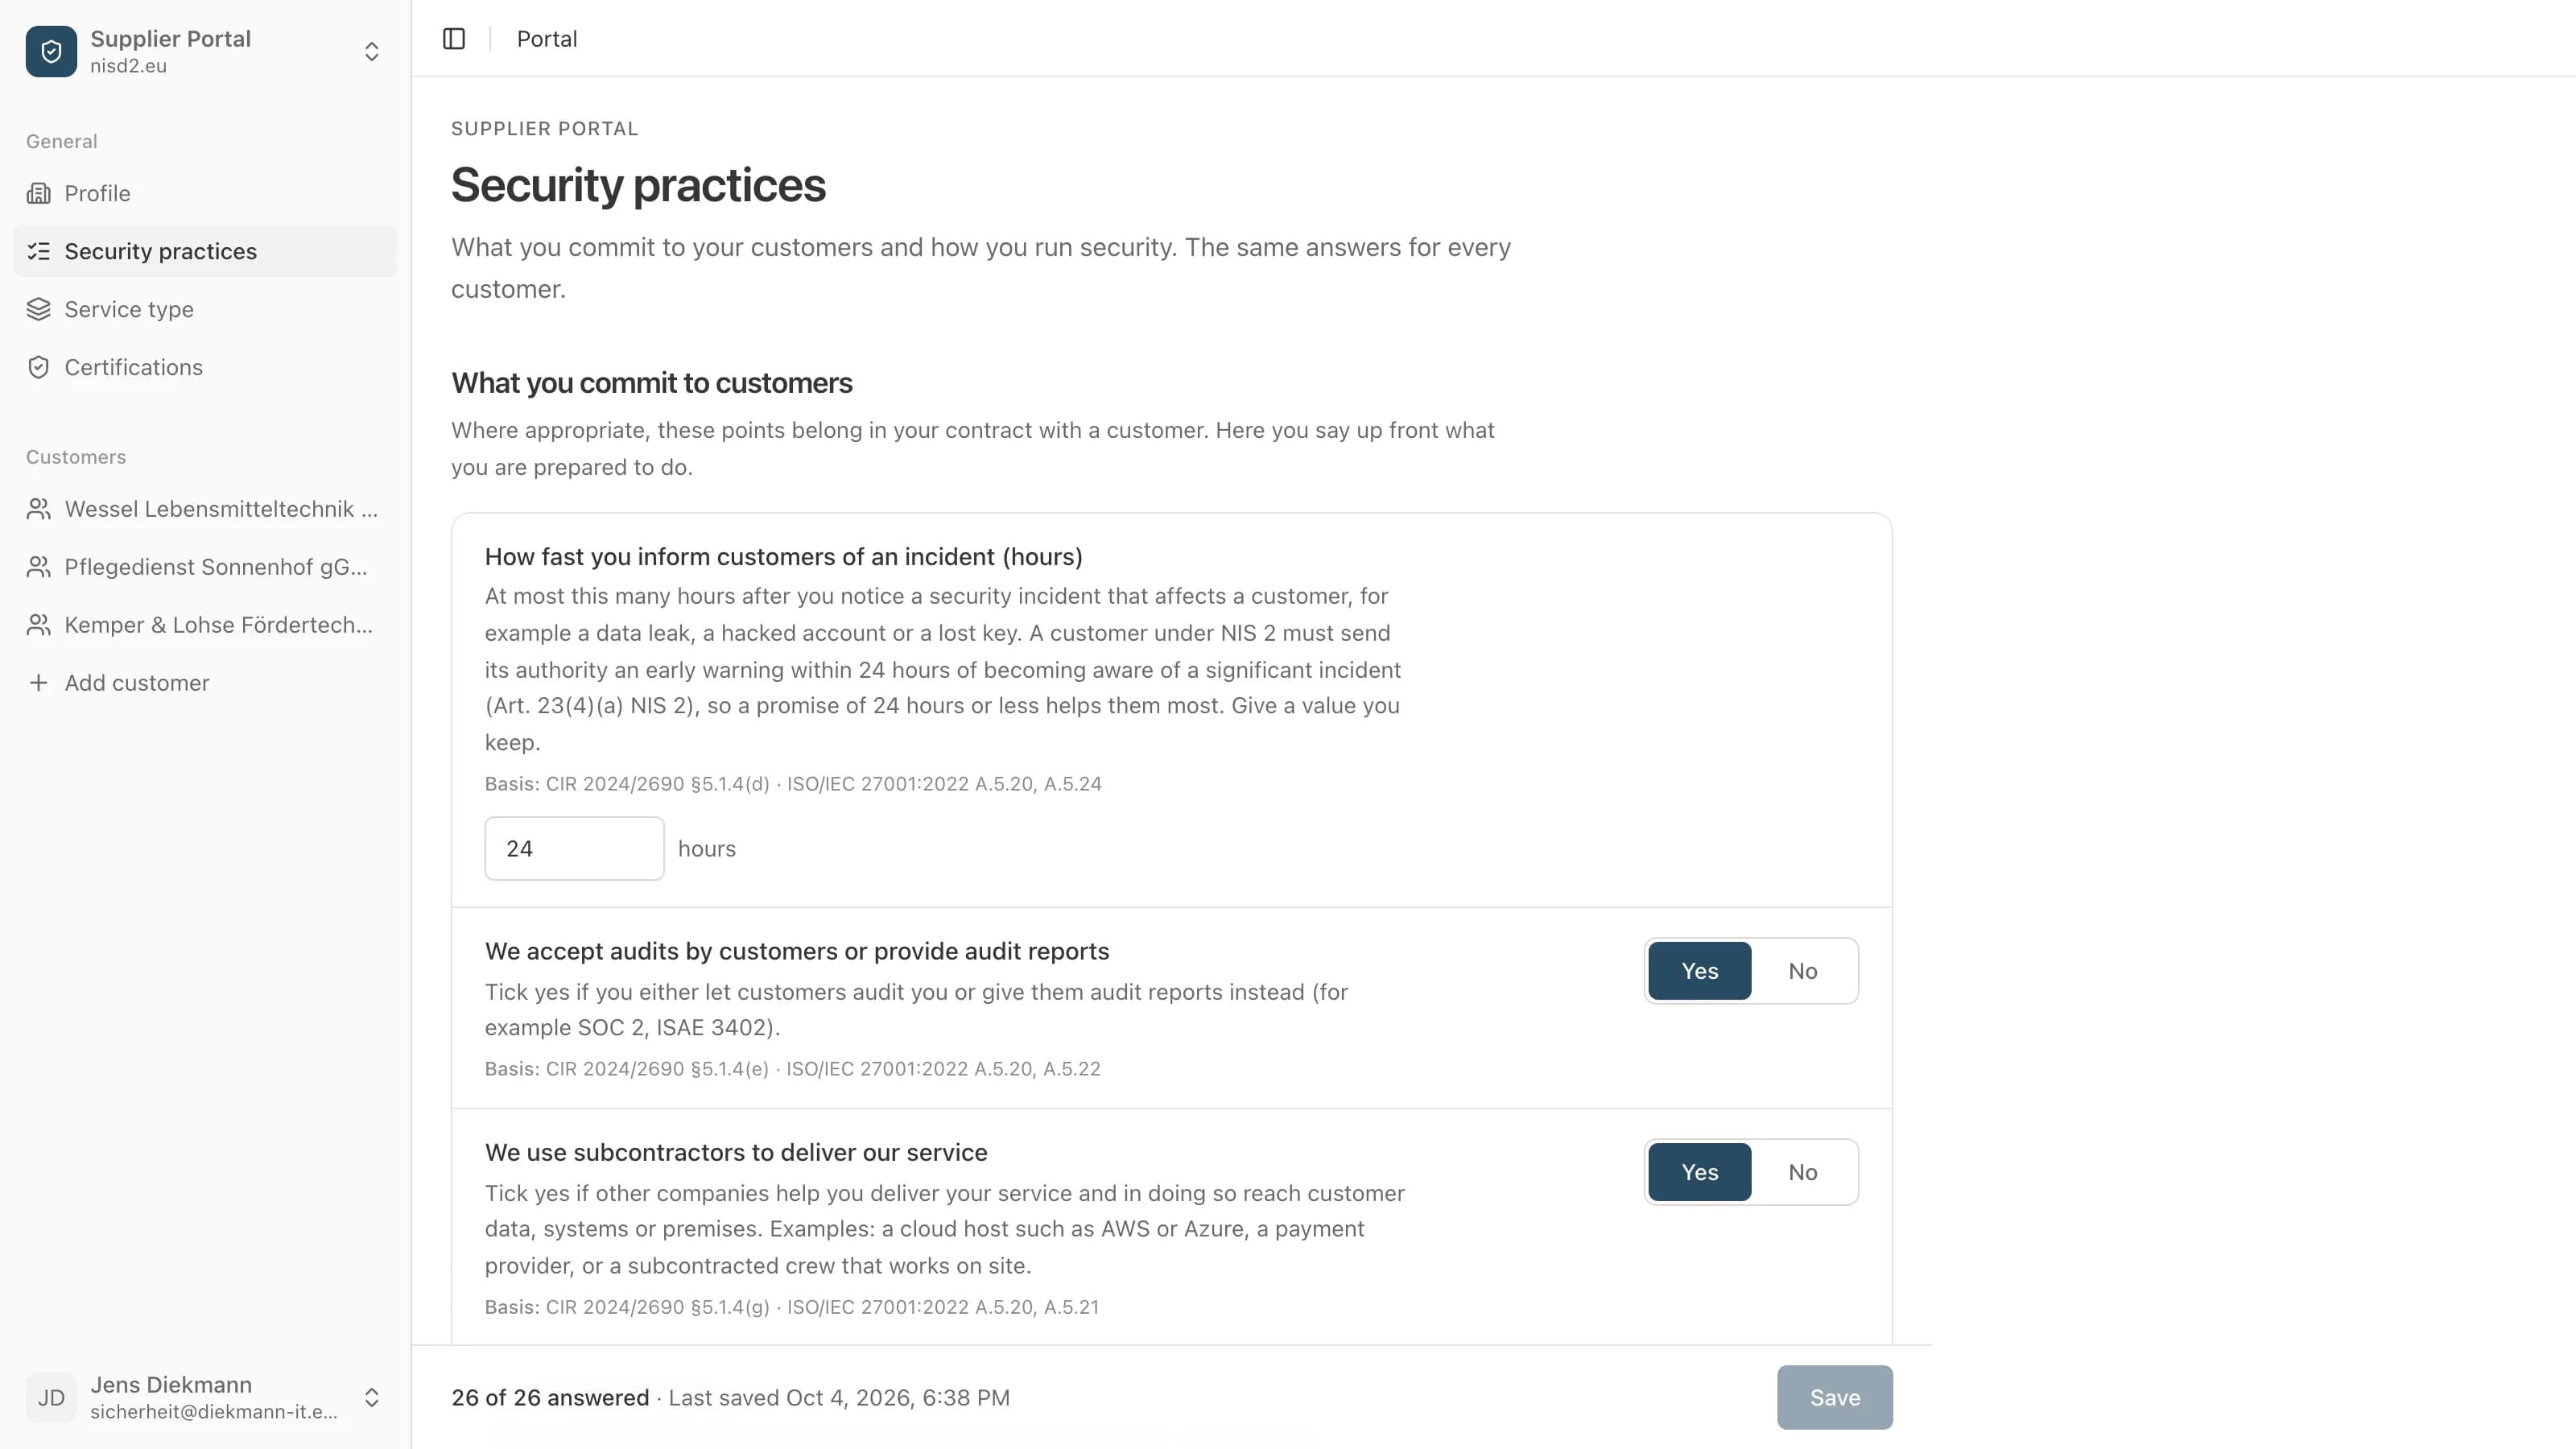
- 1
Only the questions that fit you
First you say whether you hold your customers' data, access their systems or enter their premises, and what service you provide. After that you see only the questions that belong to it, and none that do not apply to your service.
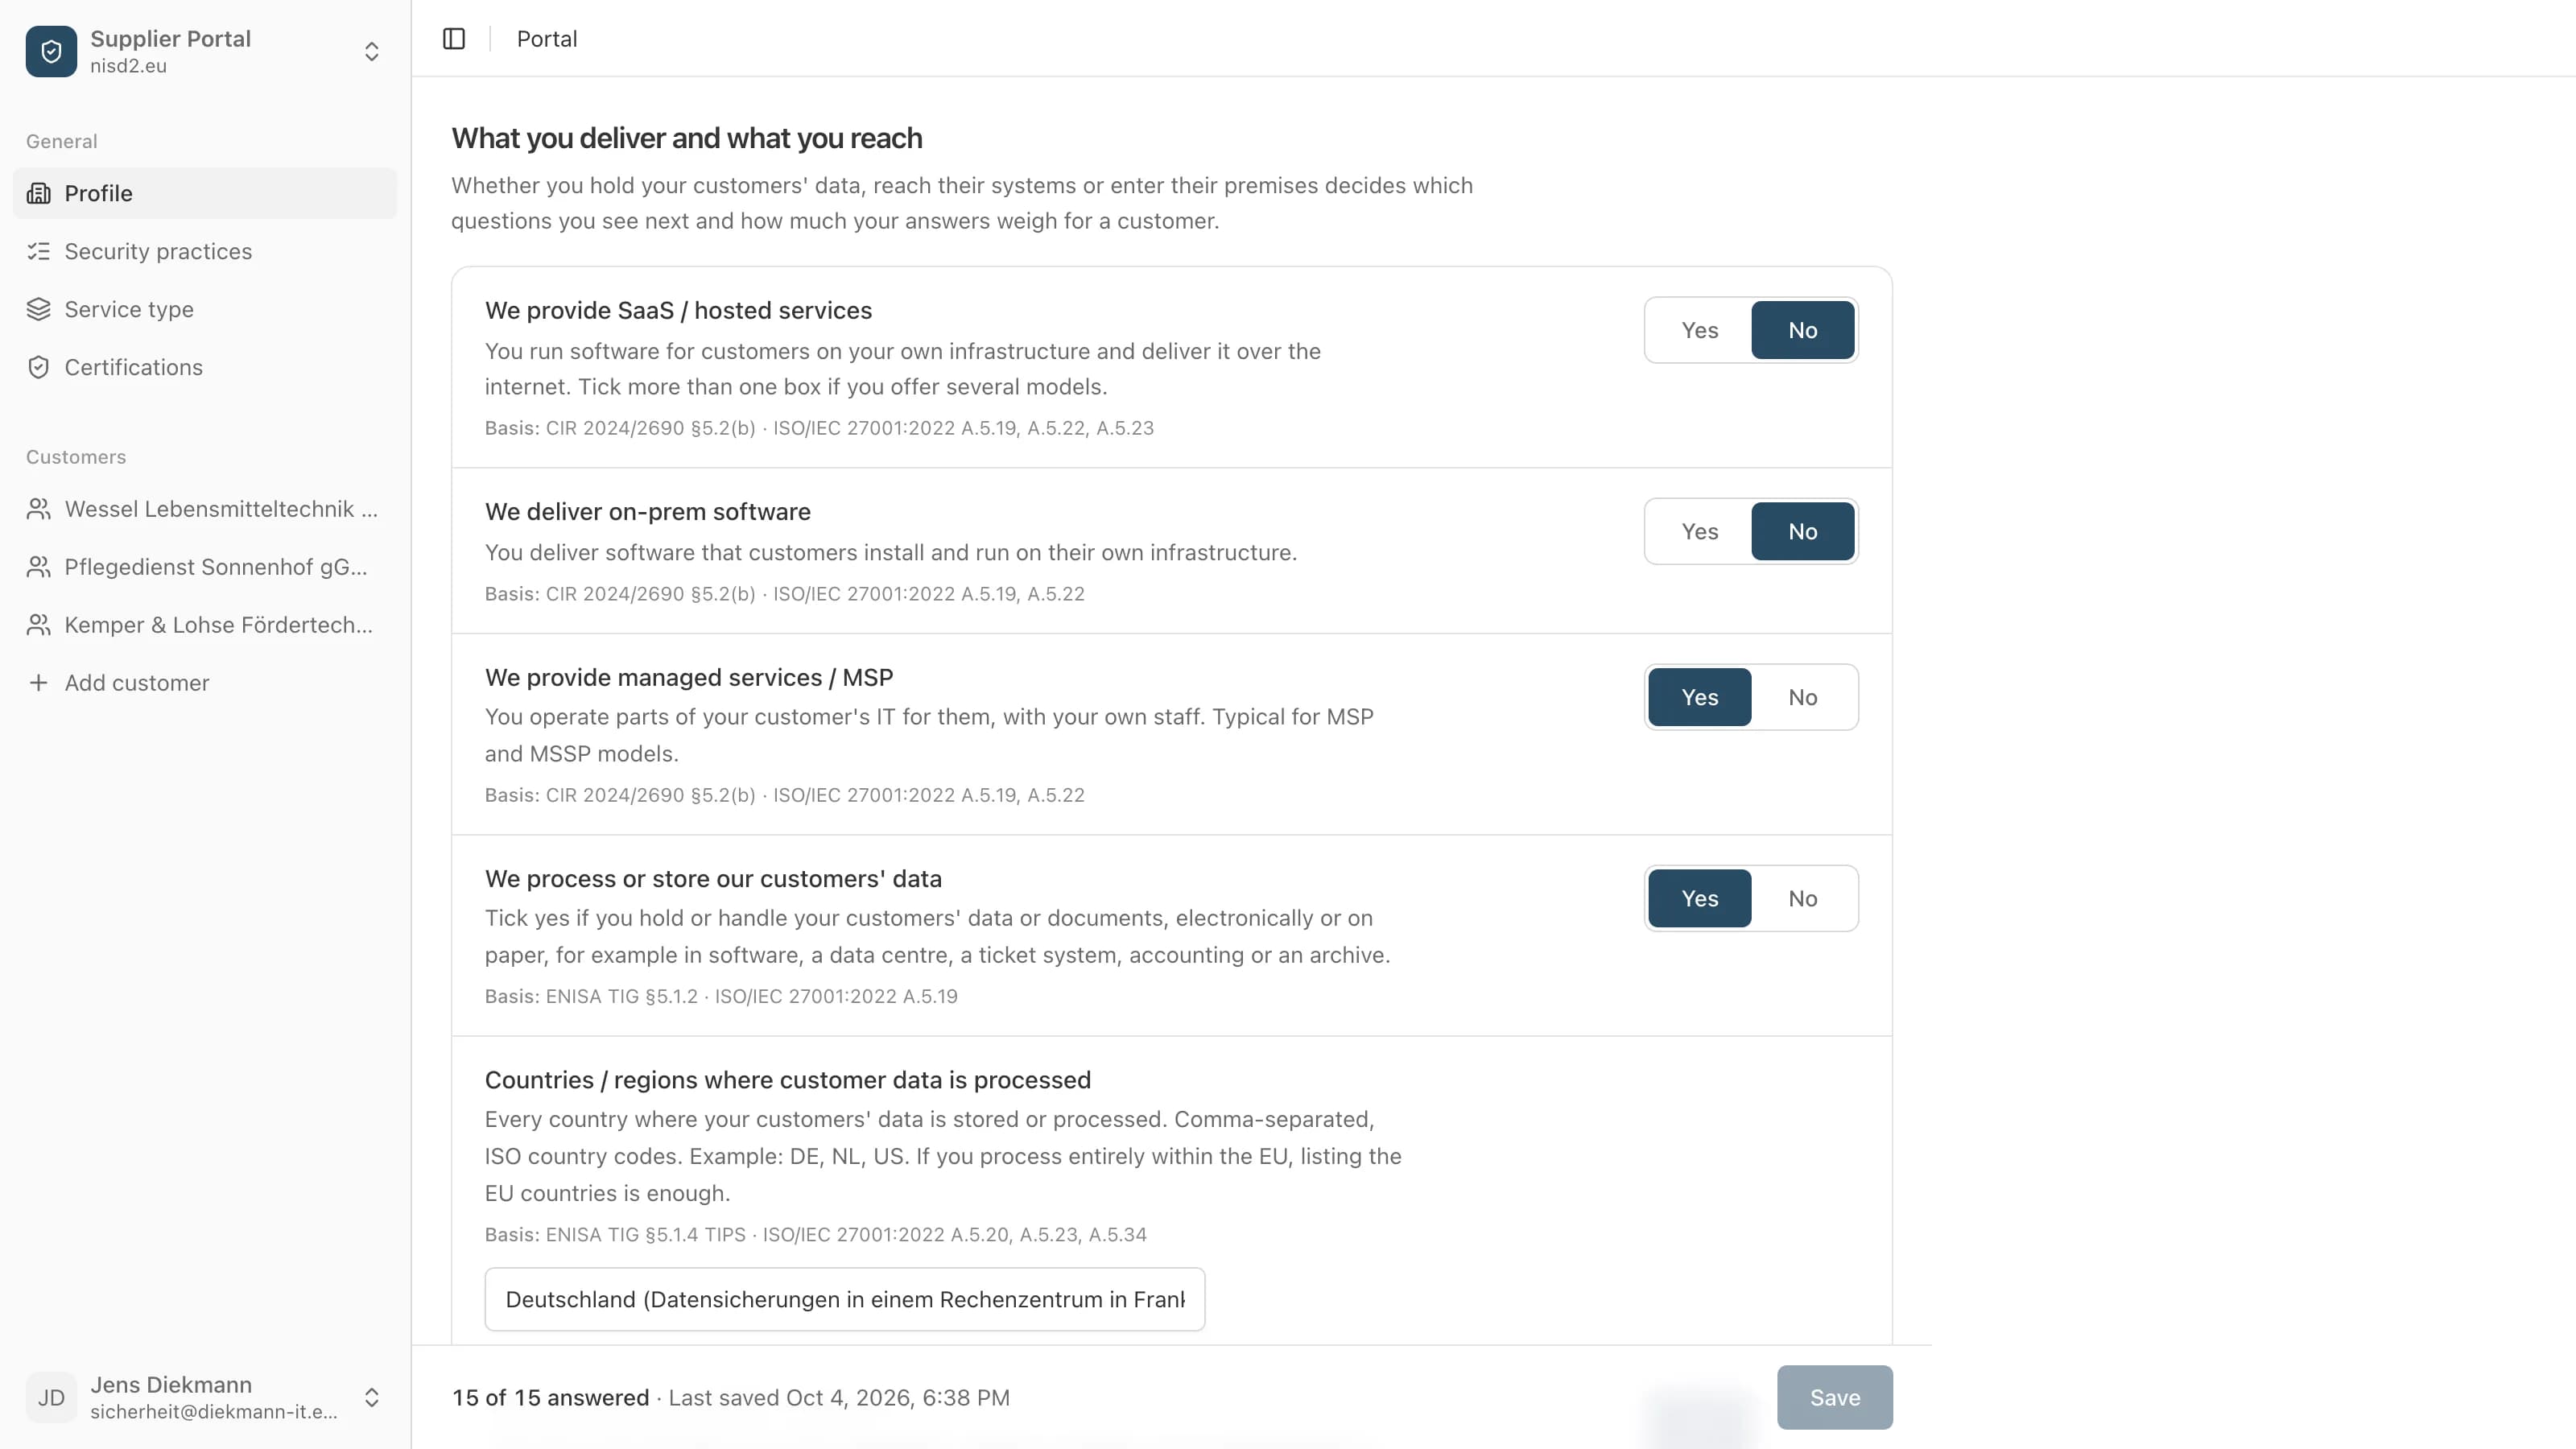
- 2
Every question says when to tick yes
Under each question it says in plain words what is meant, with examples. Below that, what the question rests on, mostly a paragraph of Implementing Regulation (EU) 2024/2690, and the matching ISO/IEC 27001:2022 control where there is one.
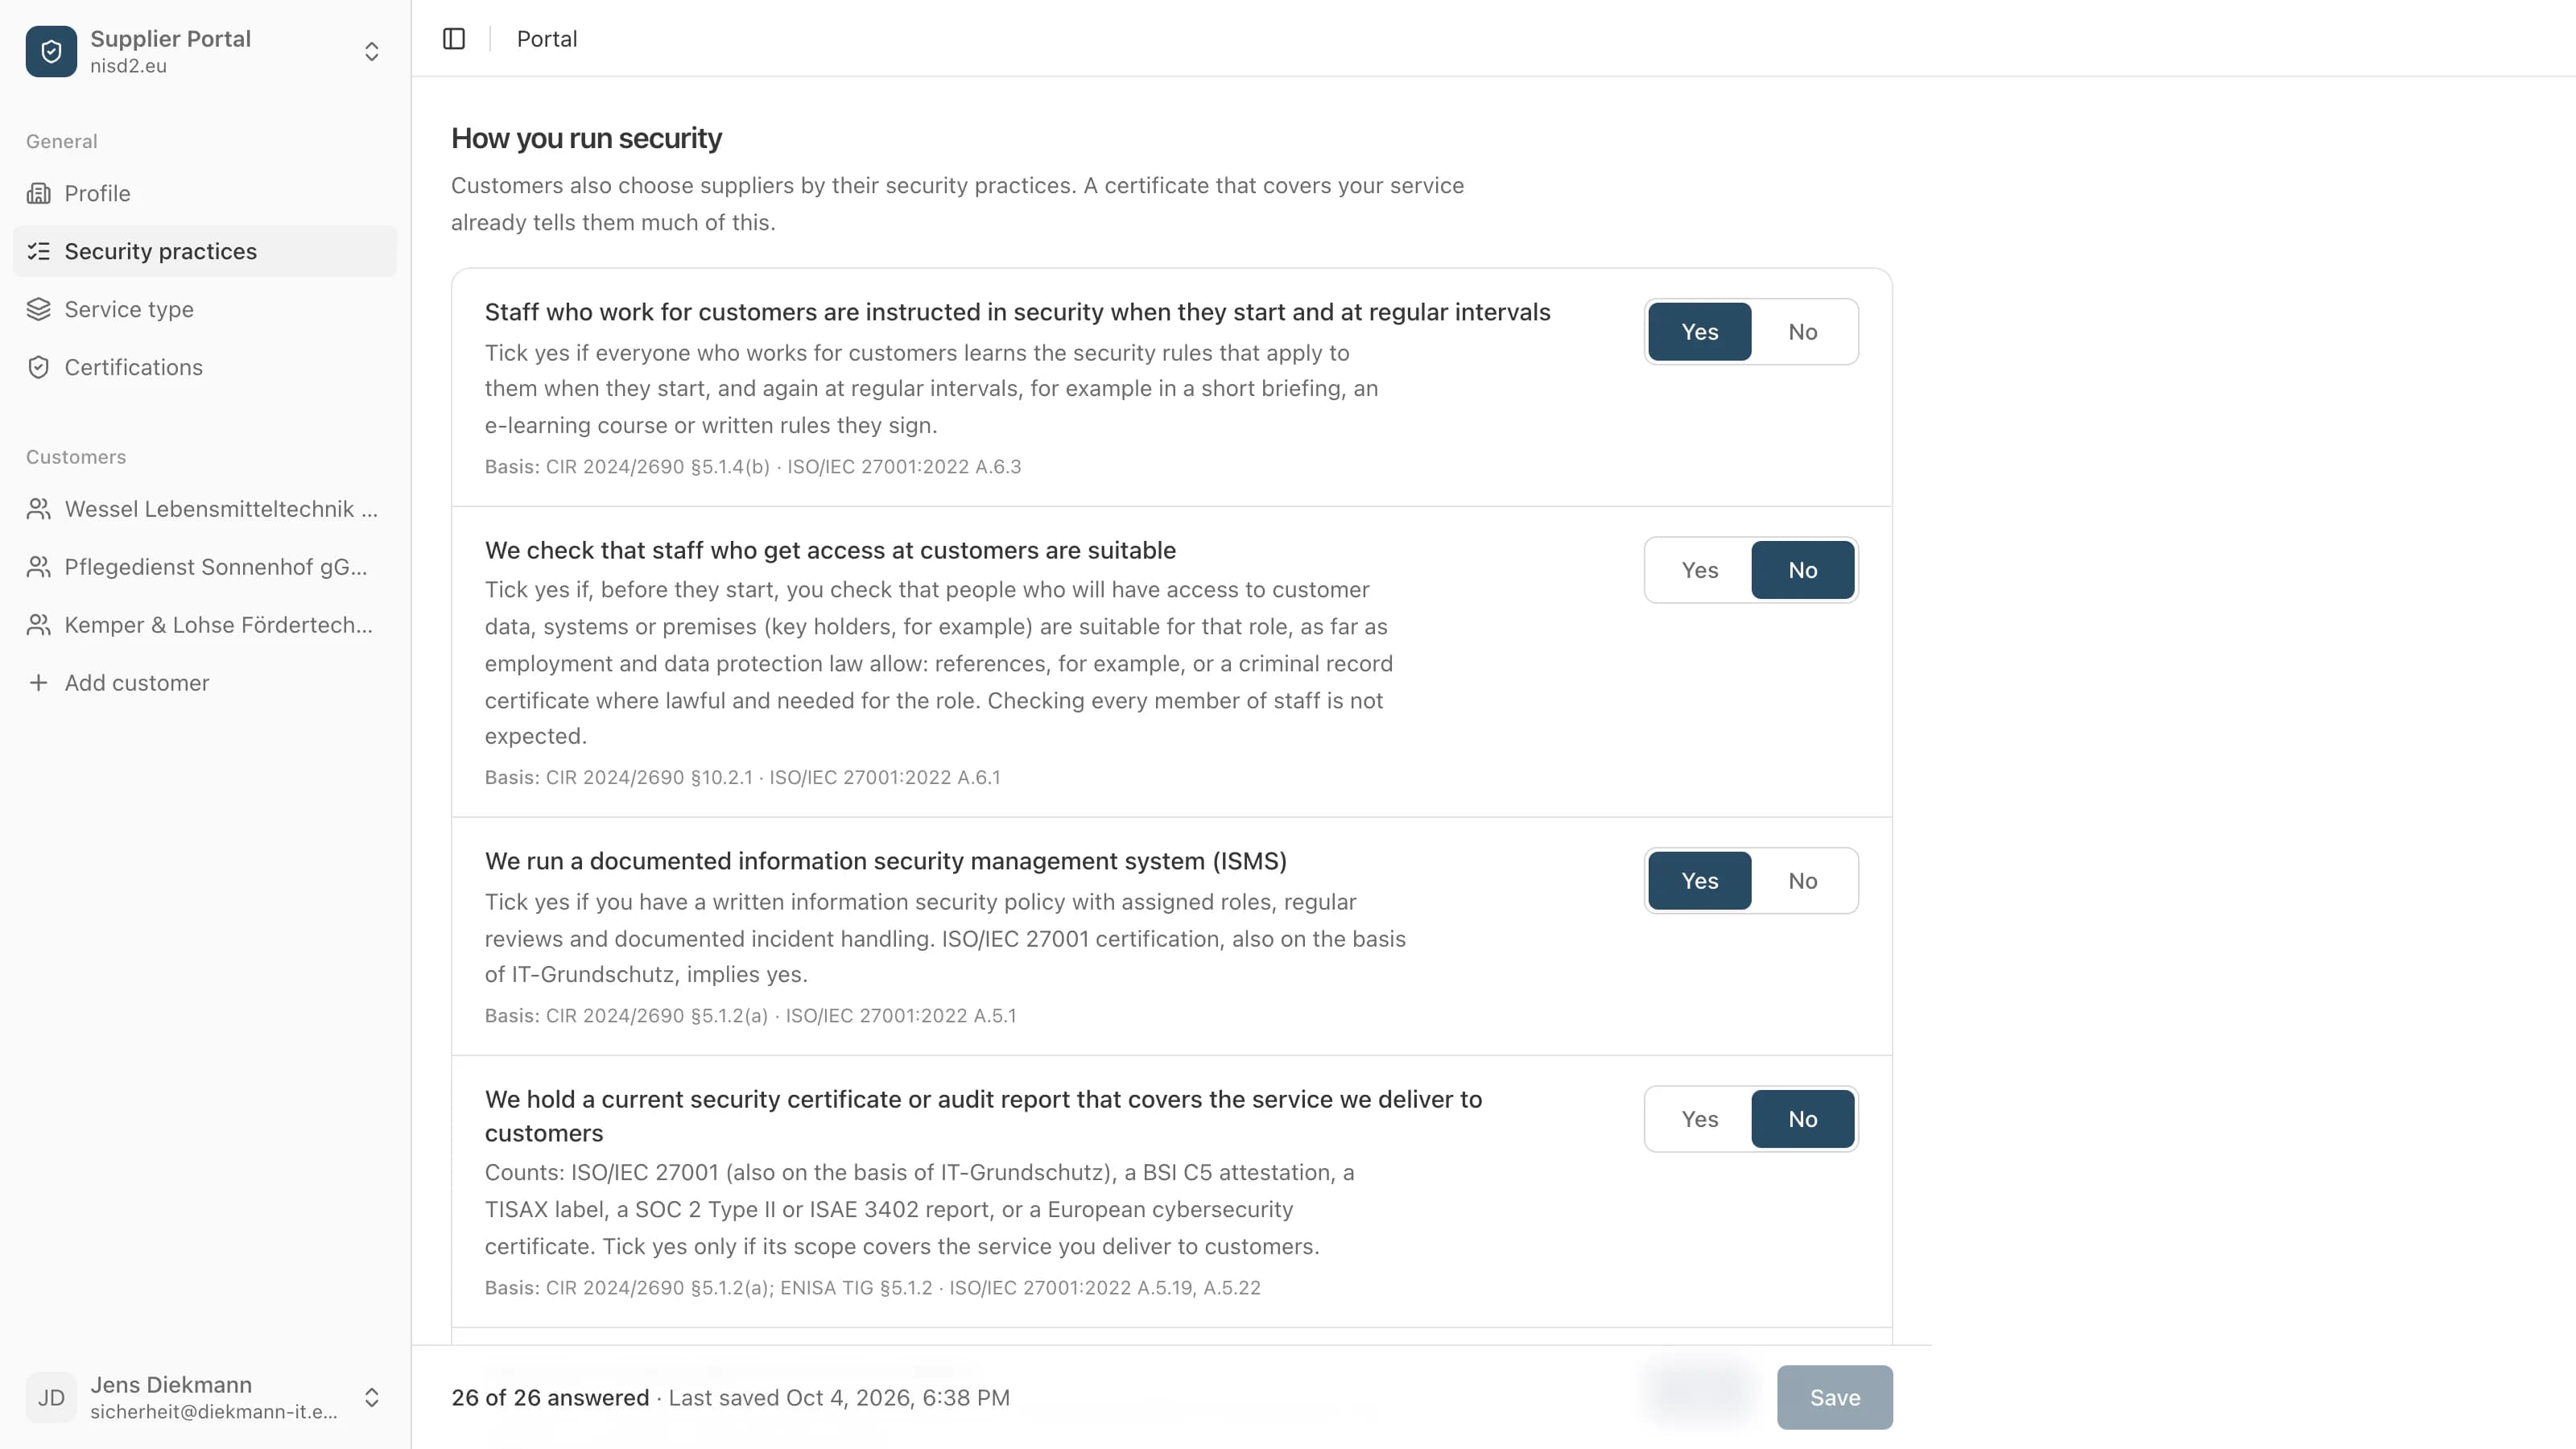
- 3
Answer once, show every customer
You invite your customers by email. Each opens your answers through a link of their own, without creating an account, and reads the same answers as everyone else. Nothing is public: no profile page, nothing for search engines. You can take the access back at any time.
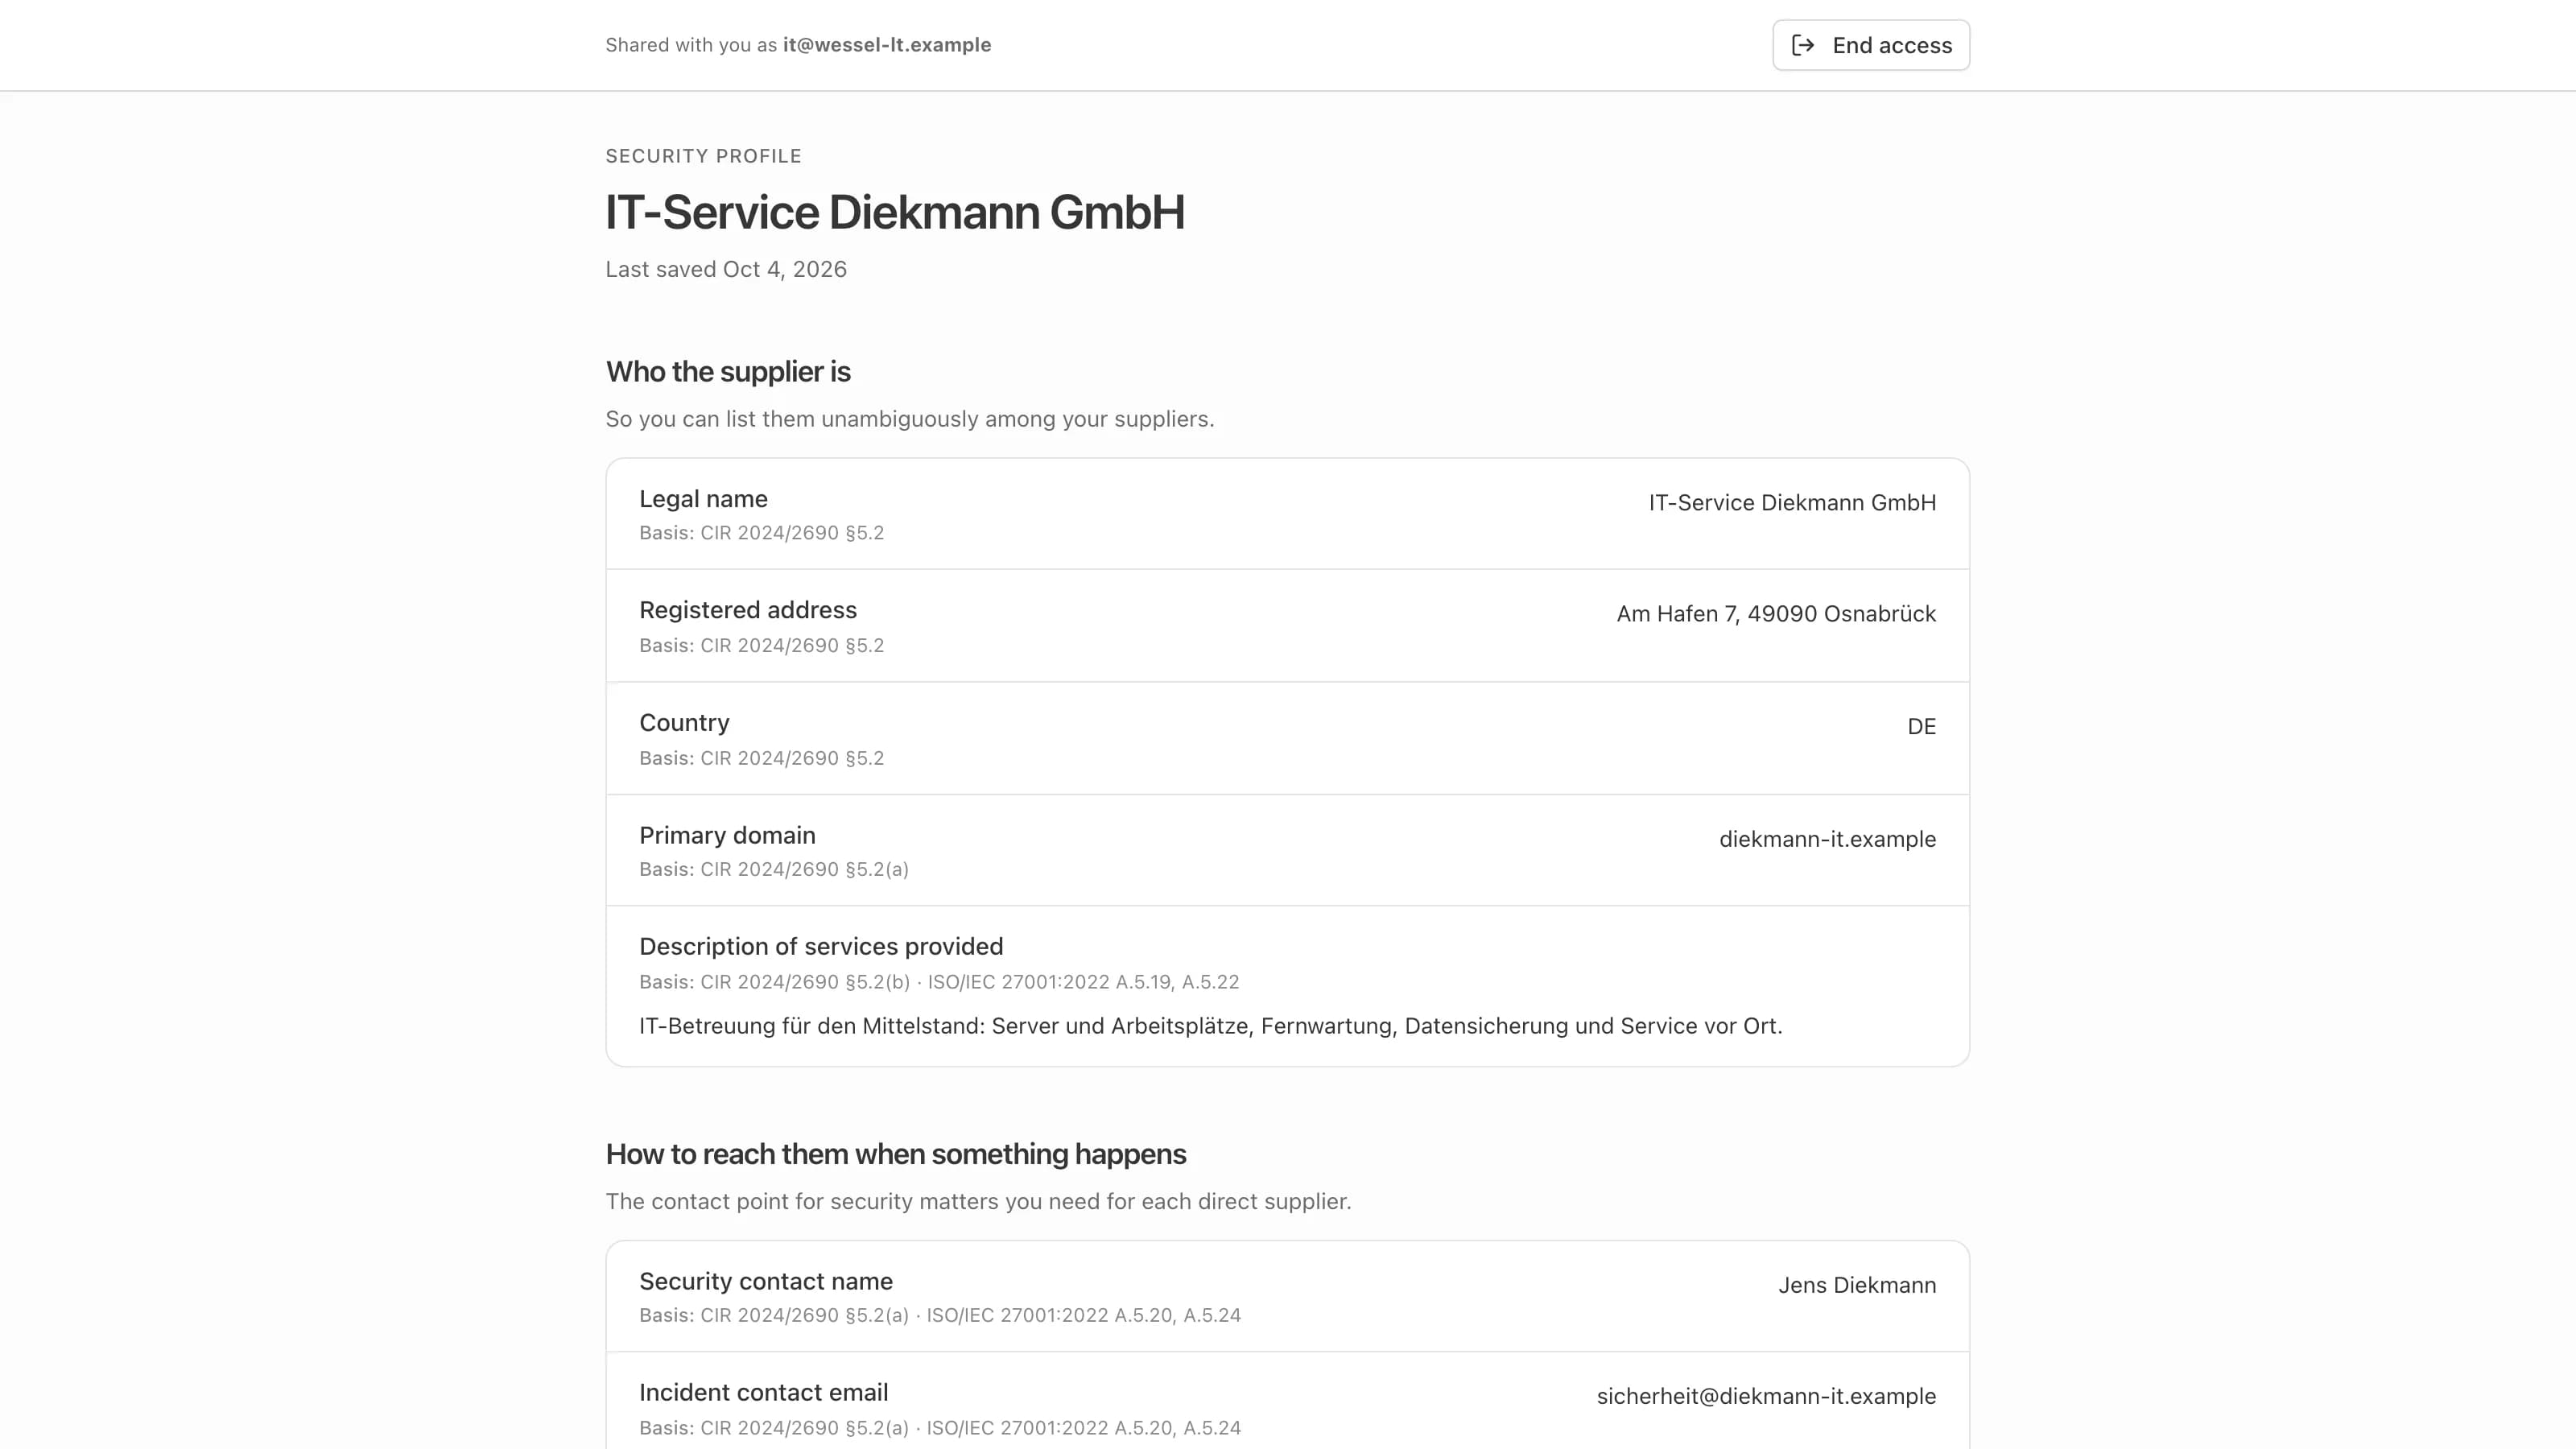
- 4
Customers on nisd2.eu have you in their supplier register
If your customer uses nisd2.eu itself, it requests your answers in the portal. From then on it opens them from its supplier register, where it keeps its suppliers under NIS 2.
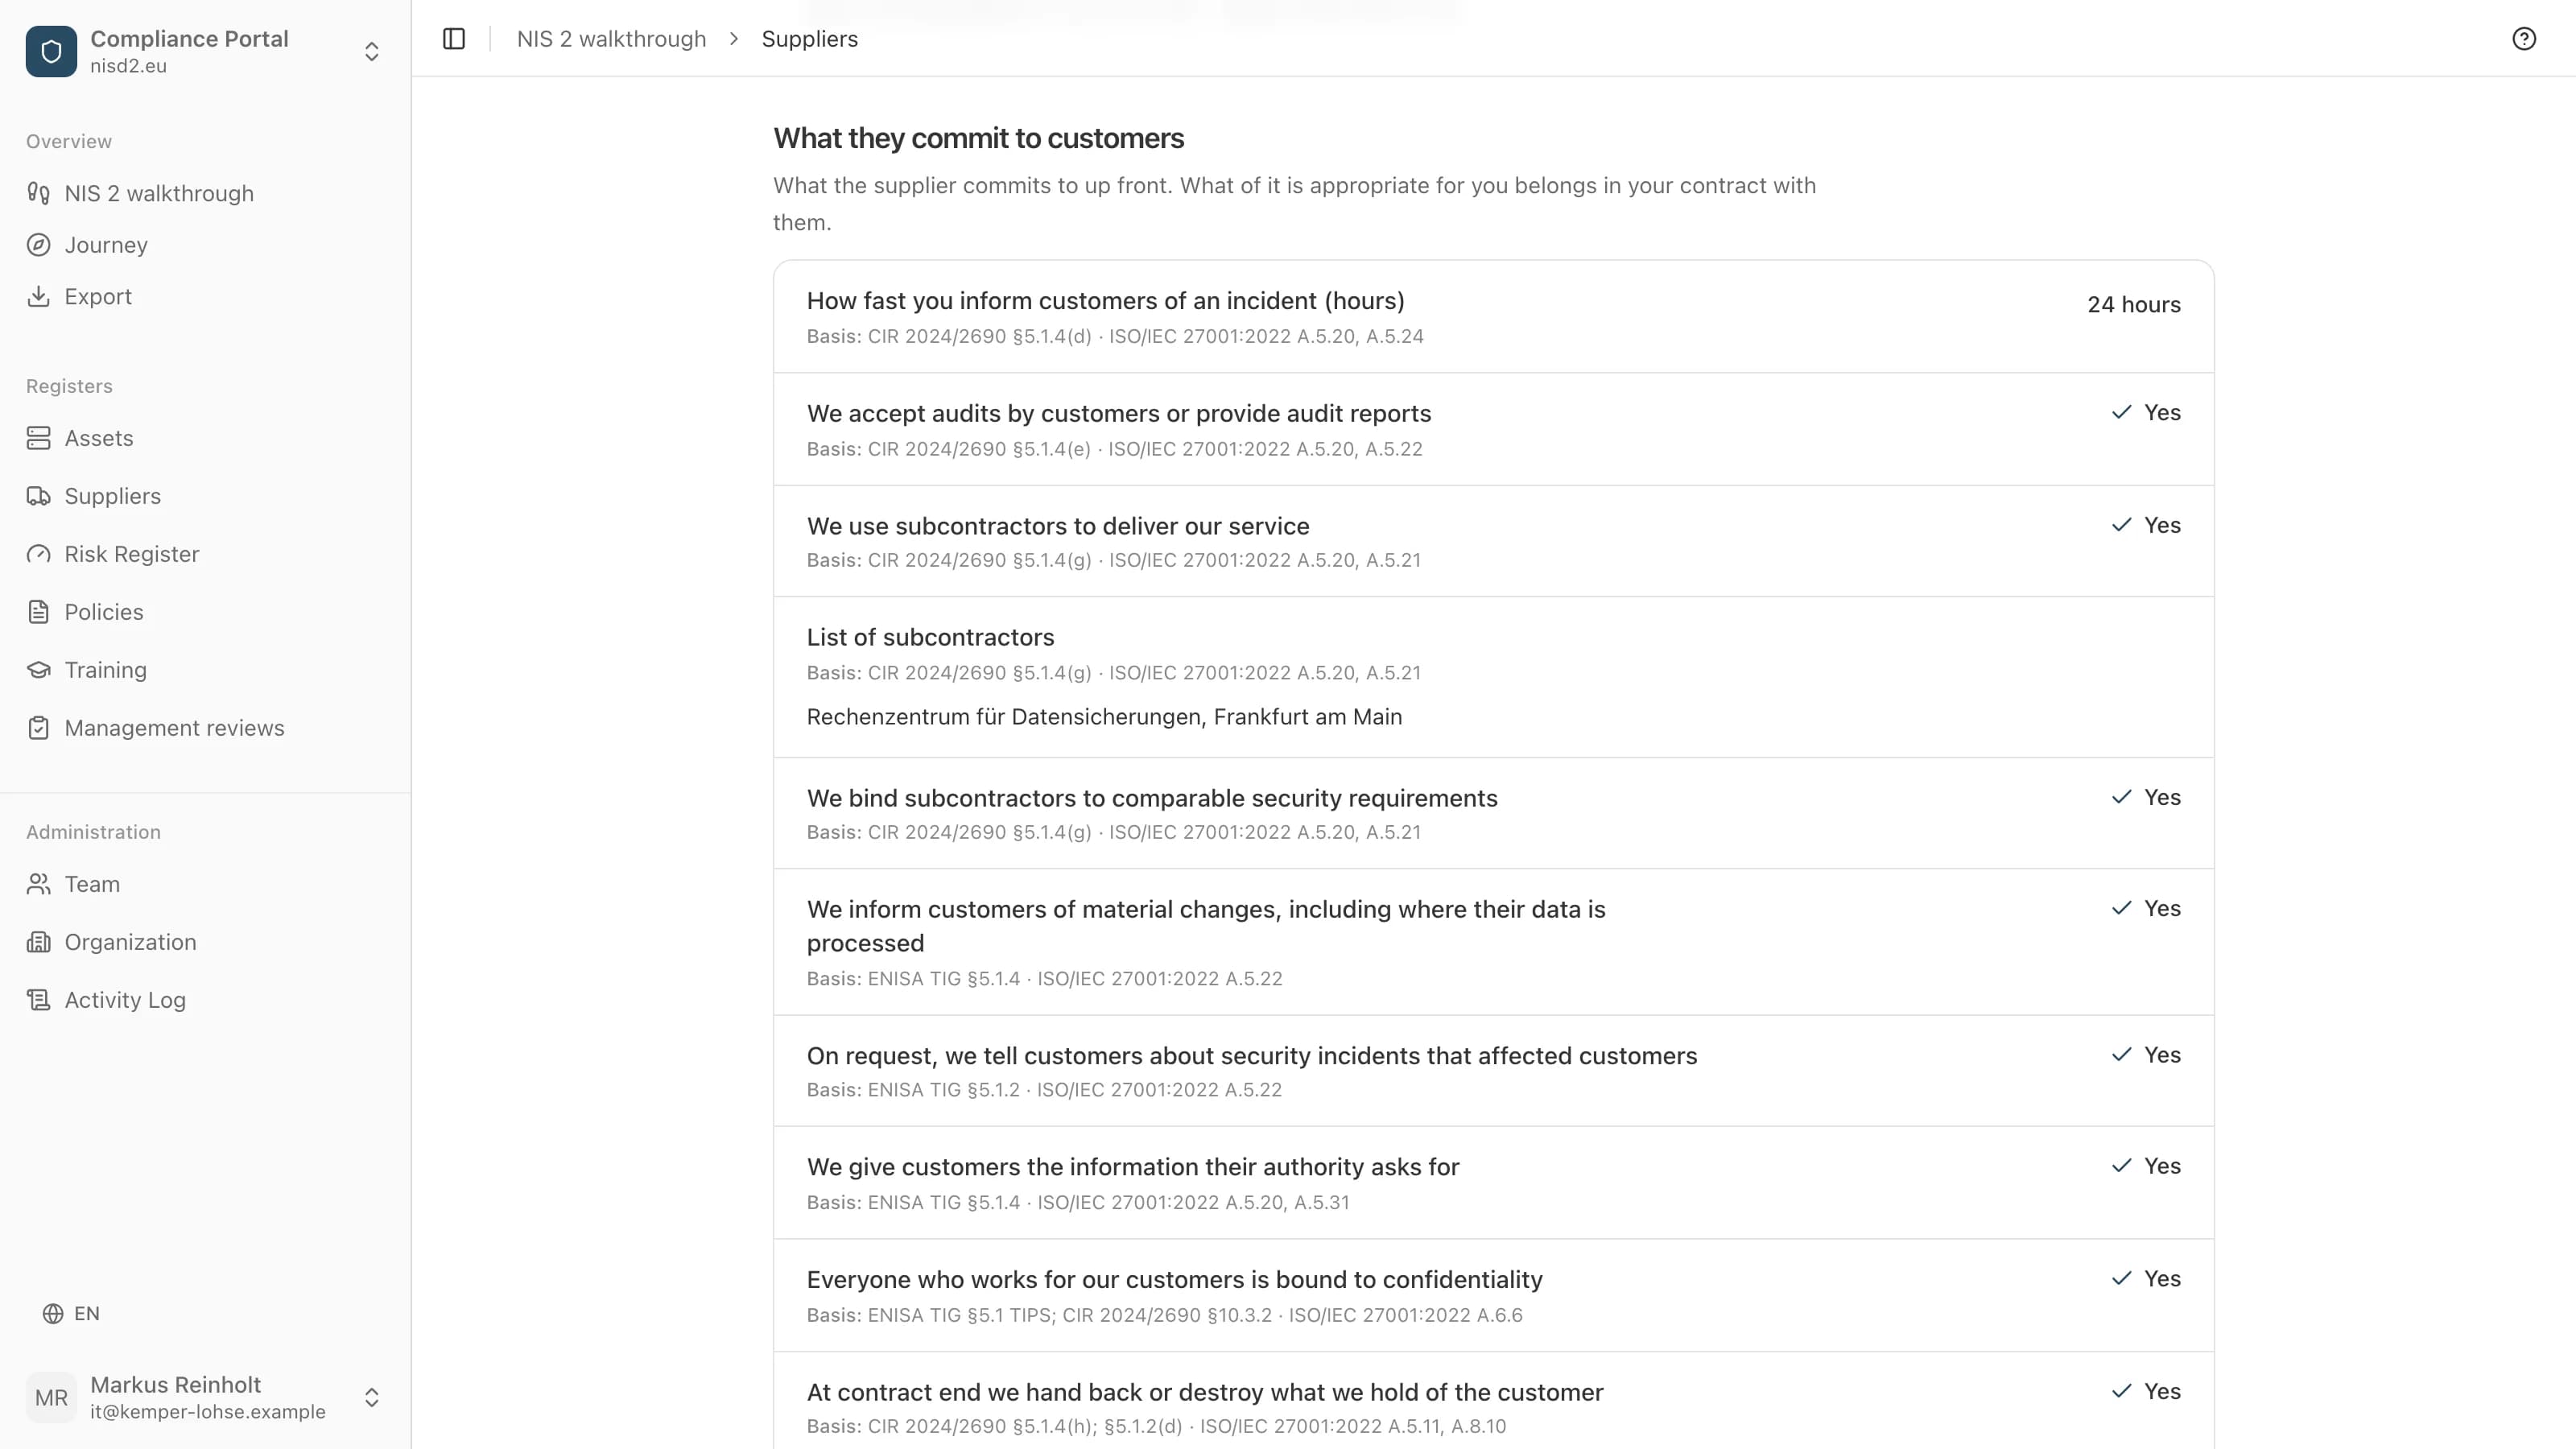
- 5
Change it in one place
When a subcontractor is added or an answer changes, you change it once in the portal. Every customer always reads the current version, with the day of your last change.
To, o co jesteś pytany, zależy od tego, do czego masz dostęp u klientów.
Każdy dostawca odpowiada na 21 pytań. W profilu podajesz, czy przechowujesz dane klientów, masz dostęp do ich systemów lub wchodzisz do ich pomieszczeń, oraz czy oferujesz oprogramowanie jako usługę, dostarczasz oprogramowanie lub prowadzisz IT dla klientów. Z tego wynika reszta. Dostawca, który ma dostęp do danych, systemów lub pomieszczeń, odpowiada też na pytania o poufność, przydatność pracowników z dostępem i zwrot na koniec umowy.
Dane Twoich klientów
Gdzie dane są przetwarzane, umowa powierzenia przetwarzania danych, szyfrowanie w spoczynku i w tranzycie. Do tego sposób zarządzania bezpieczeństwem: SZBI, certyfikat, obsługa podatności, plany na incydenty i awarie, drugi składnik dla Twoich własnych kont administratorów.
Systemy Twoich klientów
Osobiste konta z drugim składnikiem przy każdym dostępie, także przy zdalnym serwisie, oraz rejestrowanie dostępu z uprawnieniami administratora. Do tego to samo zarządzanie bezpieczeństwem co przy danych klientów.
Pomieszczenia Twoich klientów
Jak prowadzisz ewidencję kluczy, identyfikatorów i kodów oraz jakich pisemnych zasad postępowania przestrzegają Twoi pracownicy na miejscu. Dostawca, który tylko wchodzi do pomieszczeń, nie jest pytany o SZBI, testy bezpieczeństwa ani konta administratorów.
Oprogramowanie i usługi zarządzane
Jeśli oferujesz oprogramowanie jako usługę lub dostarczasz oprogramowanie: bezpieczne wytwarzanie, opublikowany sposób zgłaszania luk bezpieczeństwa, niezależne testy bezpieczeństwa. Przy SaaS także drugi składnik dla Twoich klientów i czas przywrócenia usługi; przy dostarczanym oprogramowaniu to, jak długo dostarczasz aktualizacje bezpieczeństwa, SBOM i podpisane wydania. Jeśli prowadzisz IT dla klientów, odpowiadasz na pytania o testy bezpieczeństwa i zarządzanie bezpieczeństwem.
Firma sprzątająca z kluczami widzi w ten sposób 26 pytań, dostawca SaaS przechowujący dane klientów 39.
„Wir begrüßen aktuelle Vorstöße der Wirtschaft, einen einheitlichen Fragenkatalog für Lieferanten zu erarbeiten, der die Erfüllung der Anforderungen belegt.“
We welcome current initiatives from industry to develop a uniform catalogue of questions for suppliers that demonstrates the requirements are met.
This questionnaire is one such initiative: uniform, open and free to reuse. Suppliers answer it once, and every customer reads the same answers when it manages the security of its supply chain under Art. 21(2)(d) NIS 2.
Only for customers you invite
Your answers are seen only by the customers you invite or whose request you accept. No public profile page, nothing for search engines. Hosted in the EU, with the code open on GitHub.
Start with your profile
Sign in, enter your company name, then answer the questionnaire at your own pace. You invite your customers only when you are ready.
Create supplier profileMore on nisd2.eu
- Supplier portal
What else the portal does: invite customers, store certificates, report incidents.
- Every question with its basis
The whole questionnaire to read, and as a PDF, for Word and as an open schema.
- Open source
The full source code under AGPL-3.0 on GitHub.
Open source
Platforma jest open source i bezpłatna, gdy hostujesz ją samodzielnie. Zarabiamy na wdrożeniu z przewodnikiem, a nie na Twoich danych. Kod i schematy są otwarte na GitHub, więc możesz sprawdzić sam. Wszystko można wyeksportować, bez lock-inu.