For suppliers to companies under NIS 2
Answer one security questionnaire, share it with every customer
Companies under NIS 2 have to manage the security of their supply chain, so they ask their suppliers. You answer one questionnaire, once, and every customer reads the same answers. Free for suppliers.
Programmes and memberships
How the questionnaire works
Every picture shows the real app, filled in for made-up sample companies.
- 1
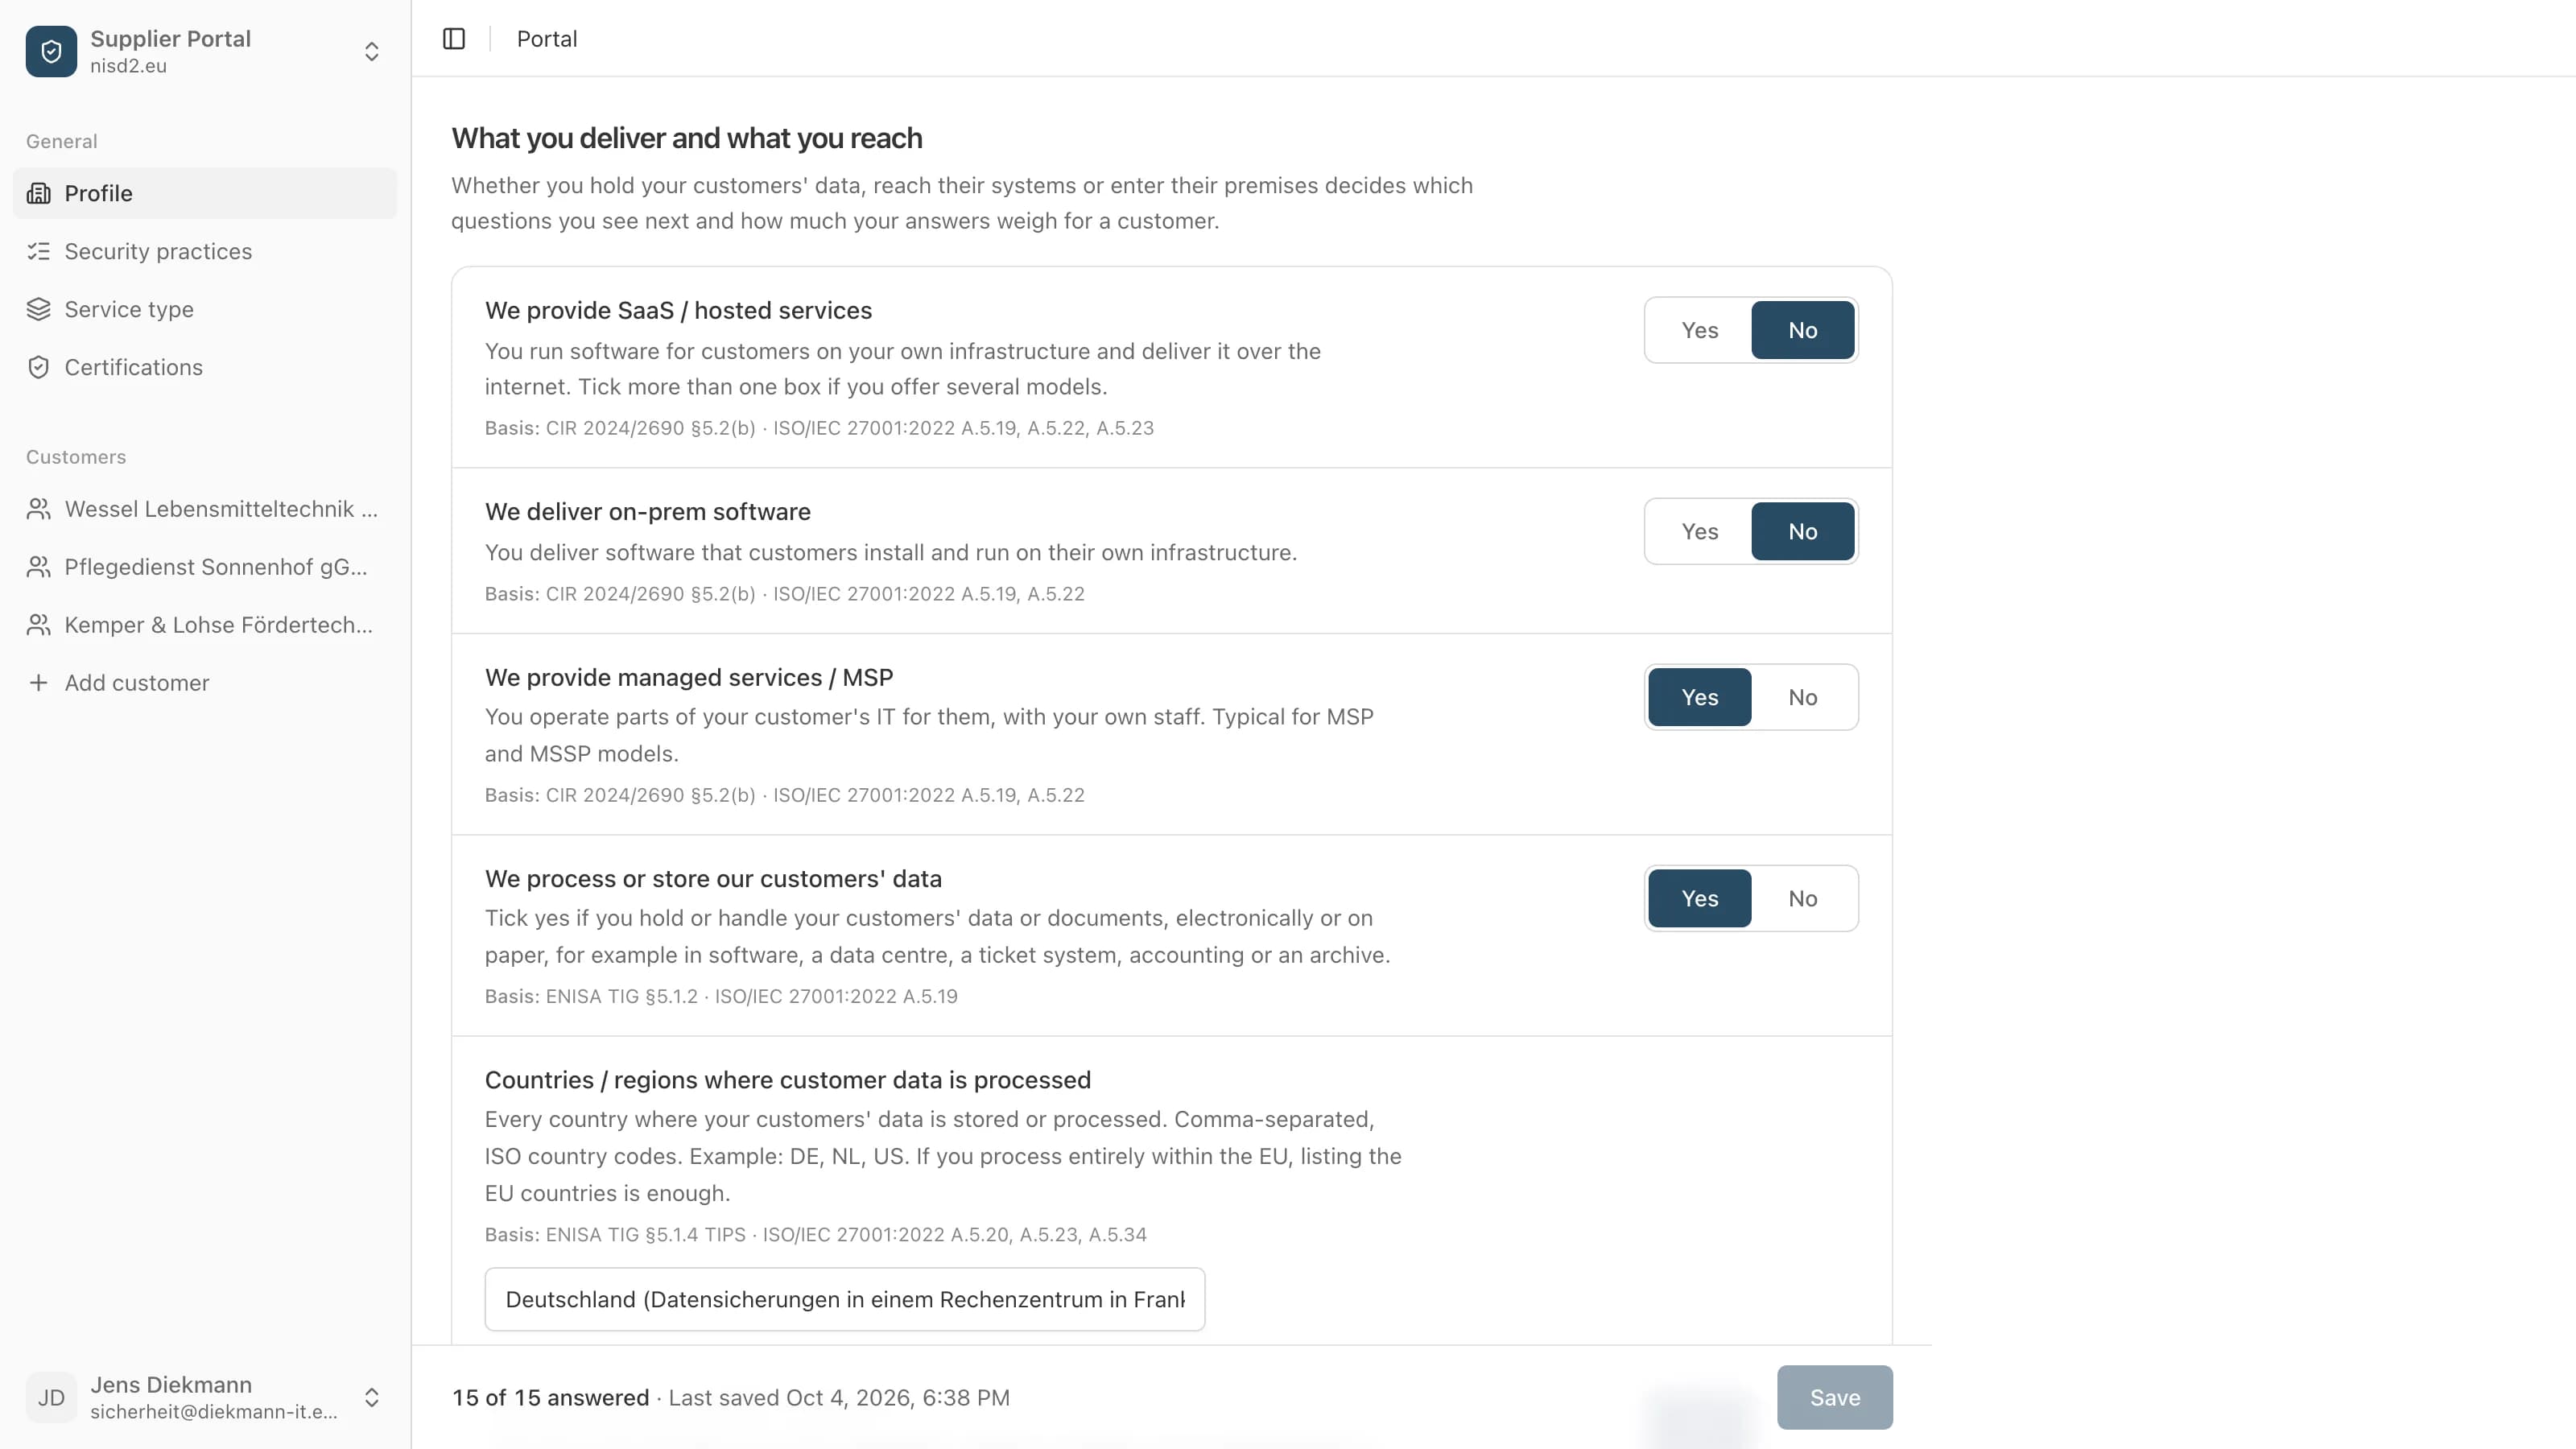
Only the questions that fit you
First you say whether you hold your customers' data, access their systems or enter their premises, and what service you provide. After that you see only the questions that belong to it, and none that do not apply to your service.
- 2
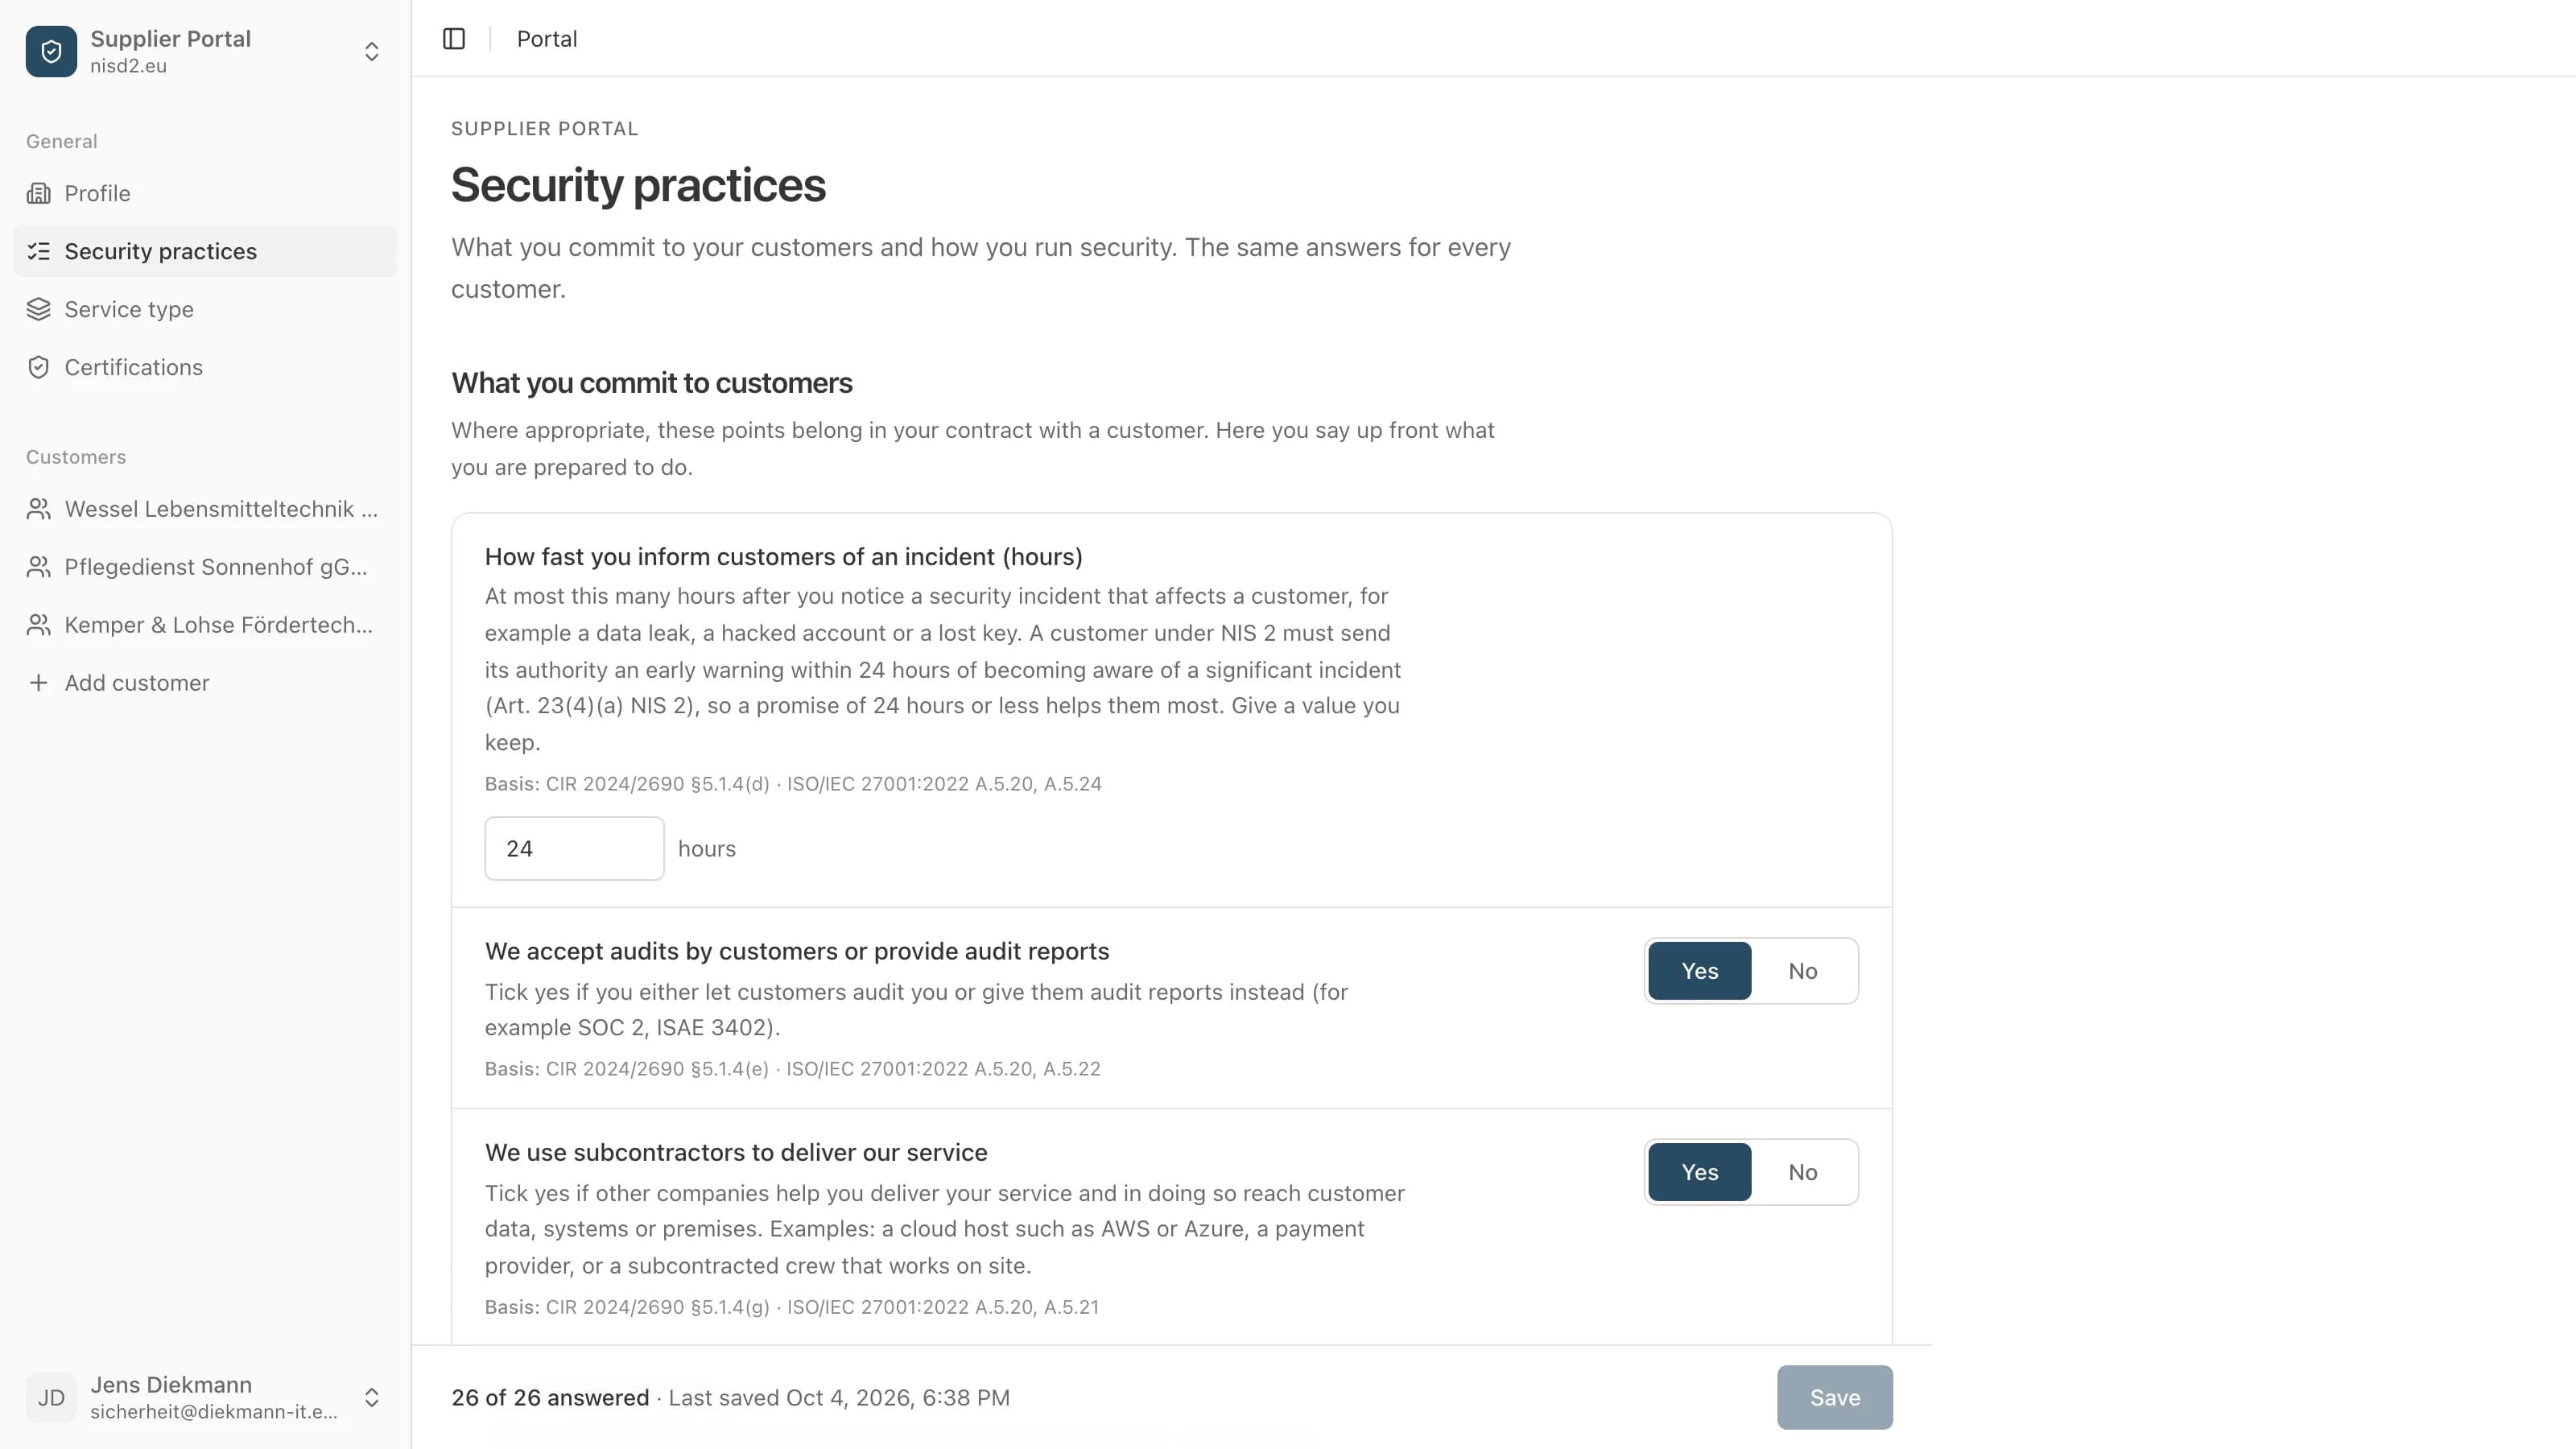
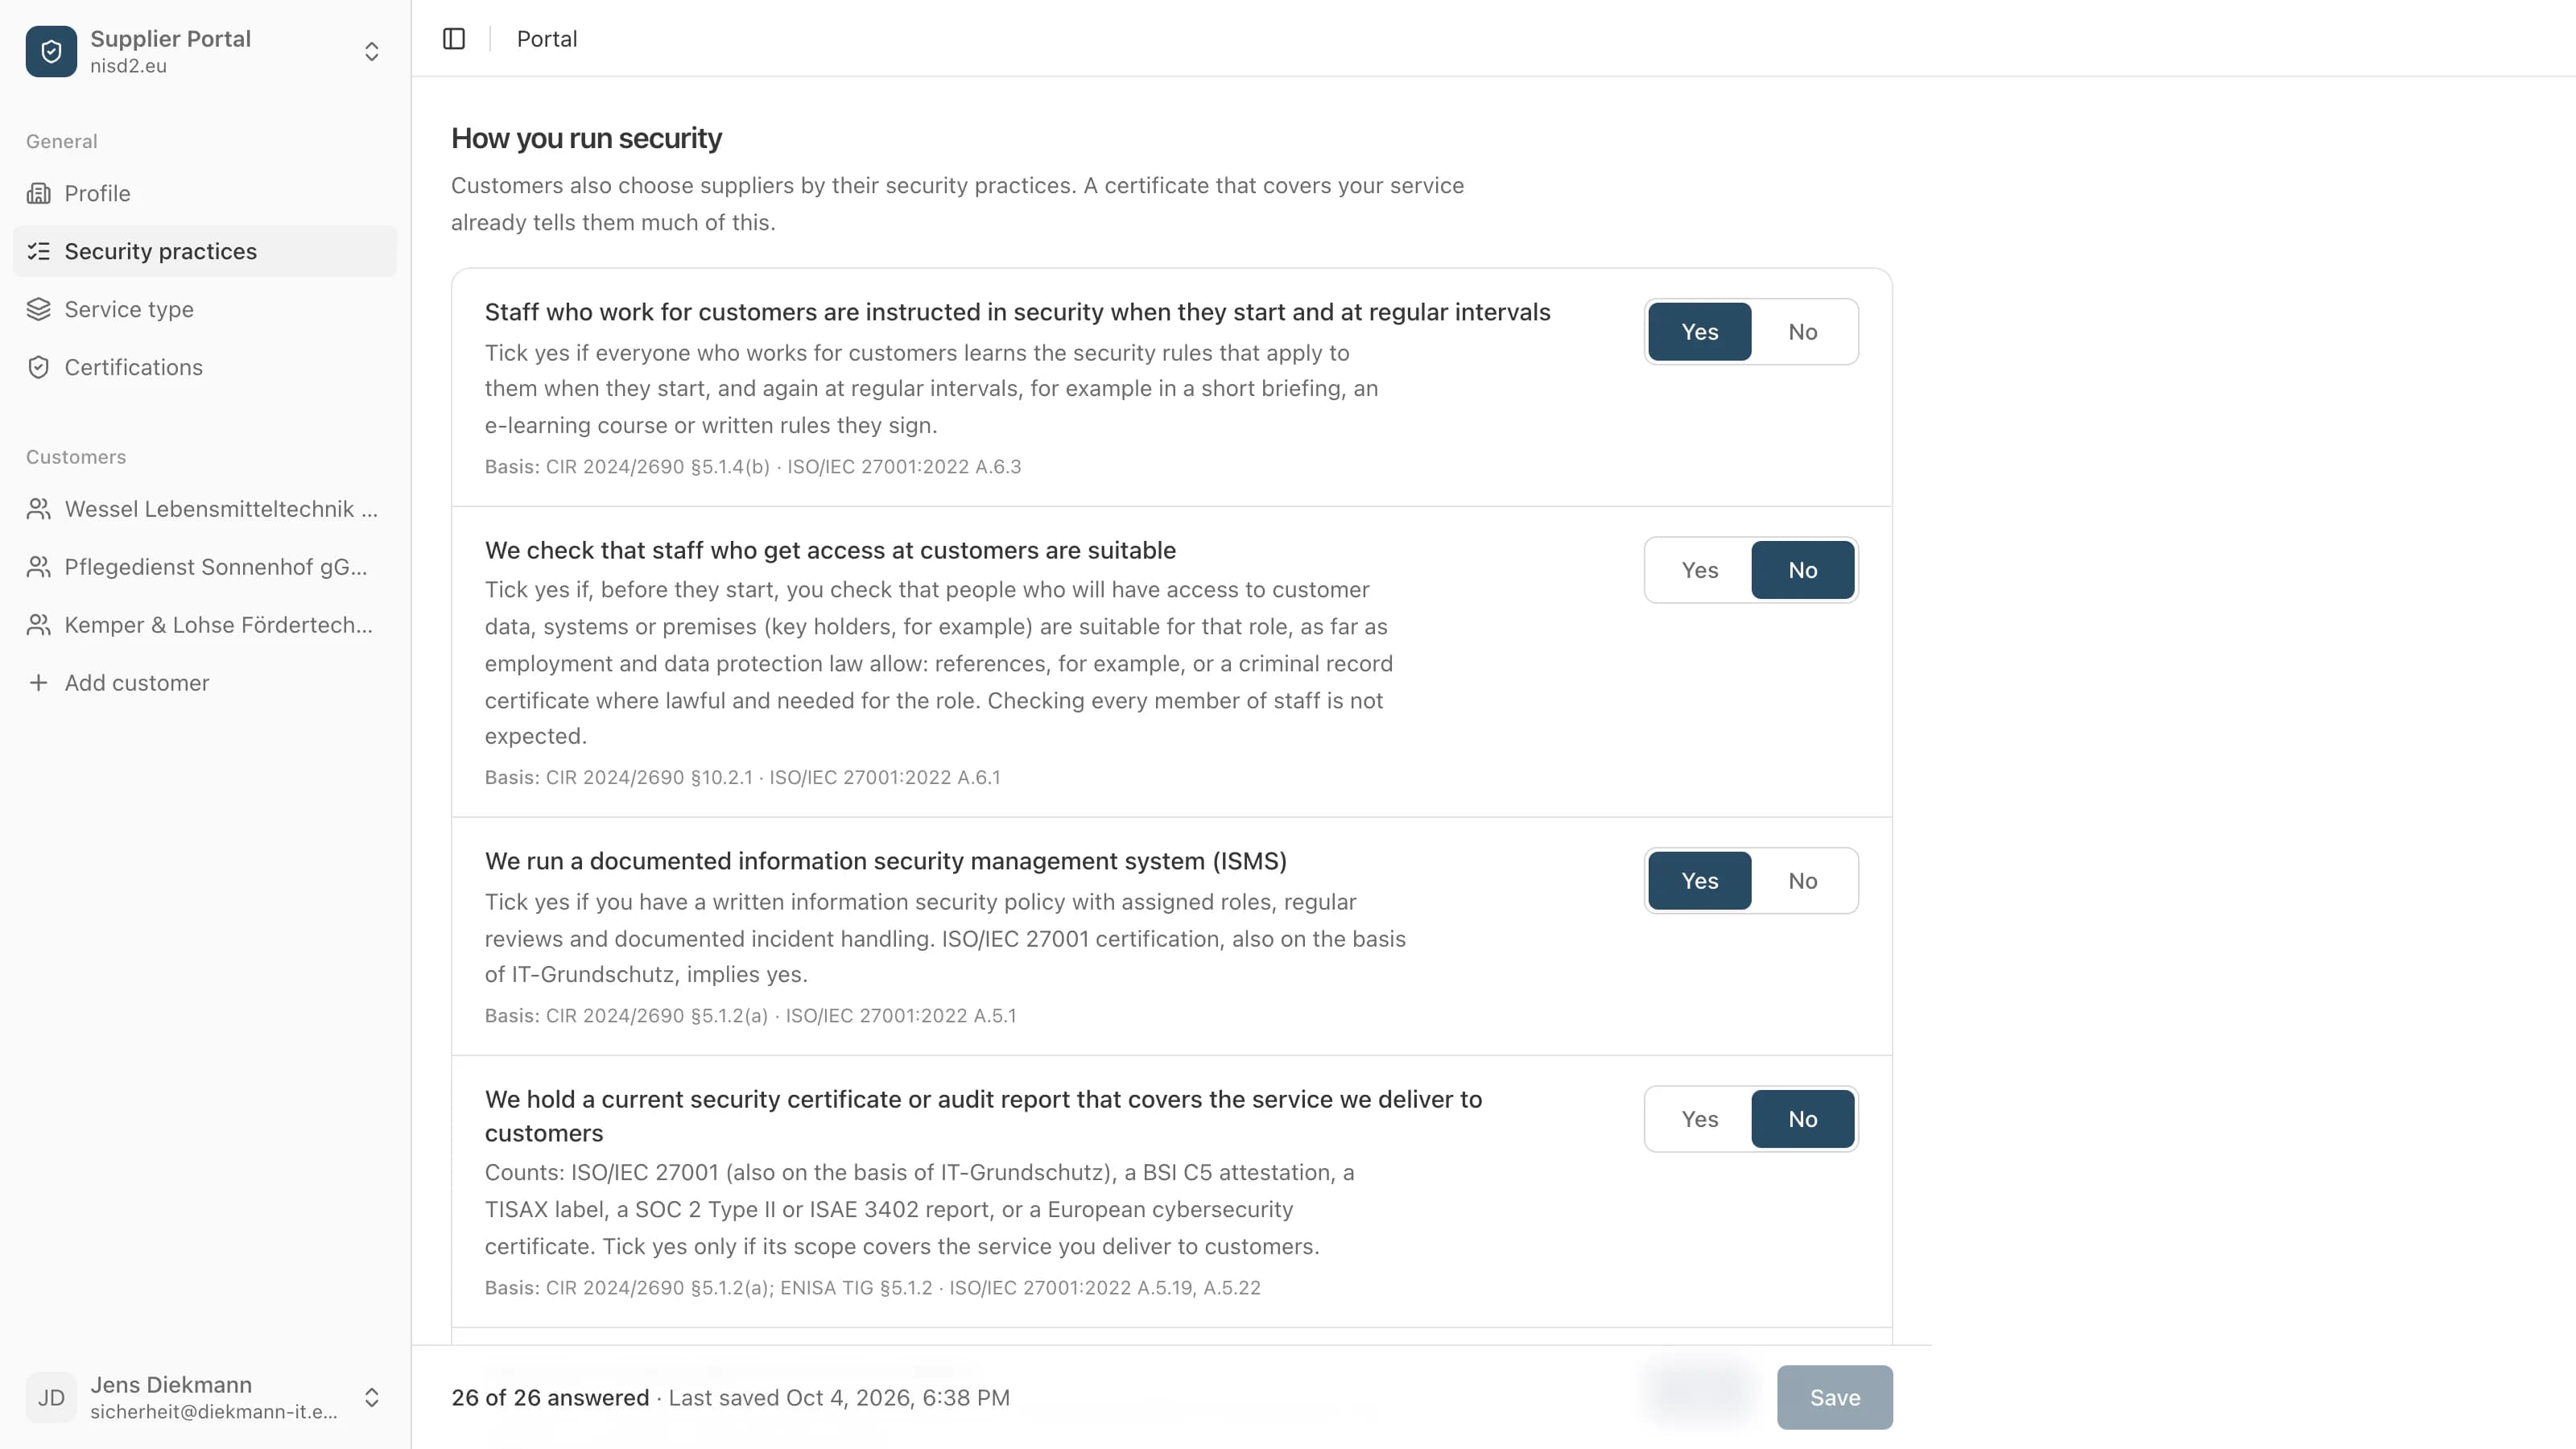
Every question says when to tick yes
Under each question it says in plain words what is meant, with examples. Below that, what the question rests on, mostly a paragraph of Implementing Regulation (EU) 2024/2690, and the matching ISO/IEC 27001:2022 control where there is one.
- 3
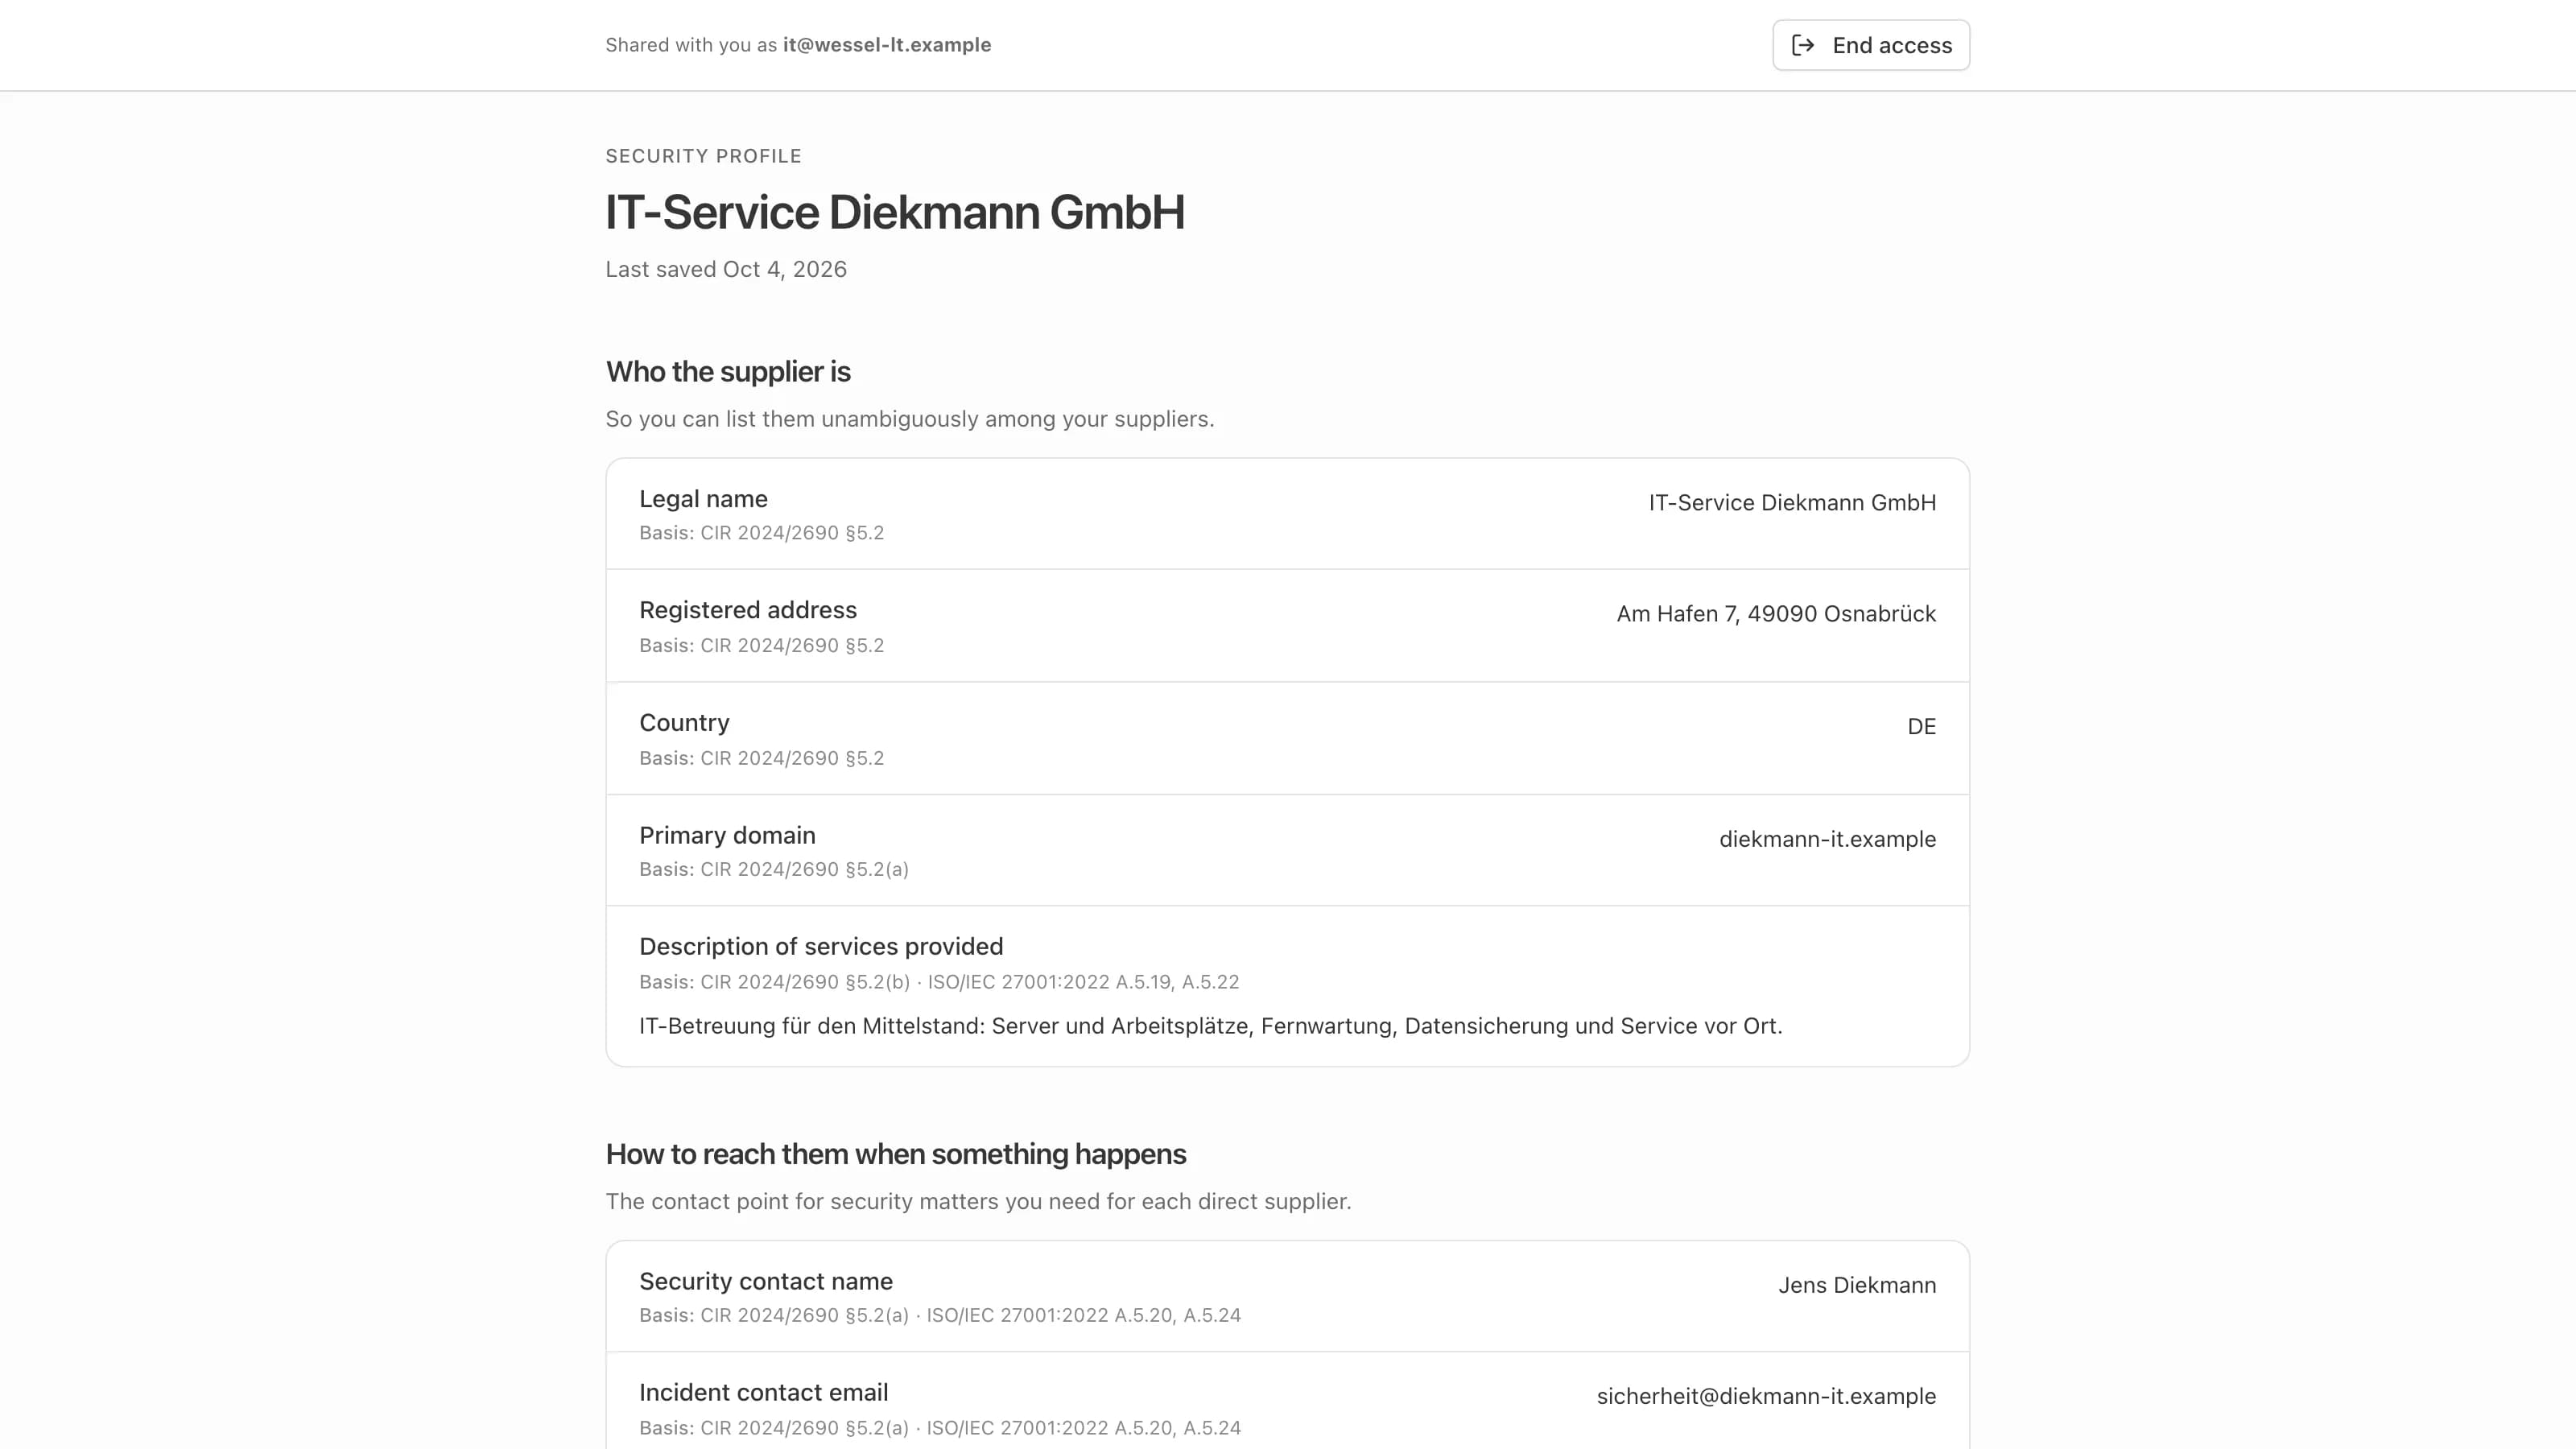
Answer once, show every customer
You invite your customers by email. Each opens your answers through a link of their own, without creating an account, and reads the same answers as everyone else. Nothing is public: no profile page, nothing for search engines. You can take the access back at any time.
- 4
Customers on nisd2.eu have you in their supplier register
If your customer uses nisd2.eu itself, it requests your answers in the portal. From then on it opens them from its supplier register, where it keeps its suppliers under NIS 2.
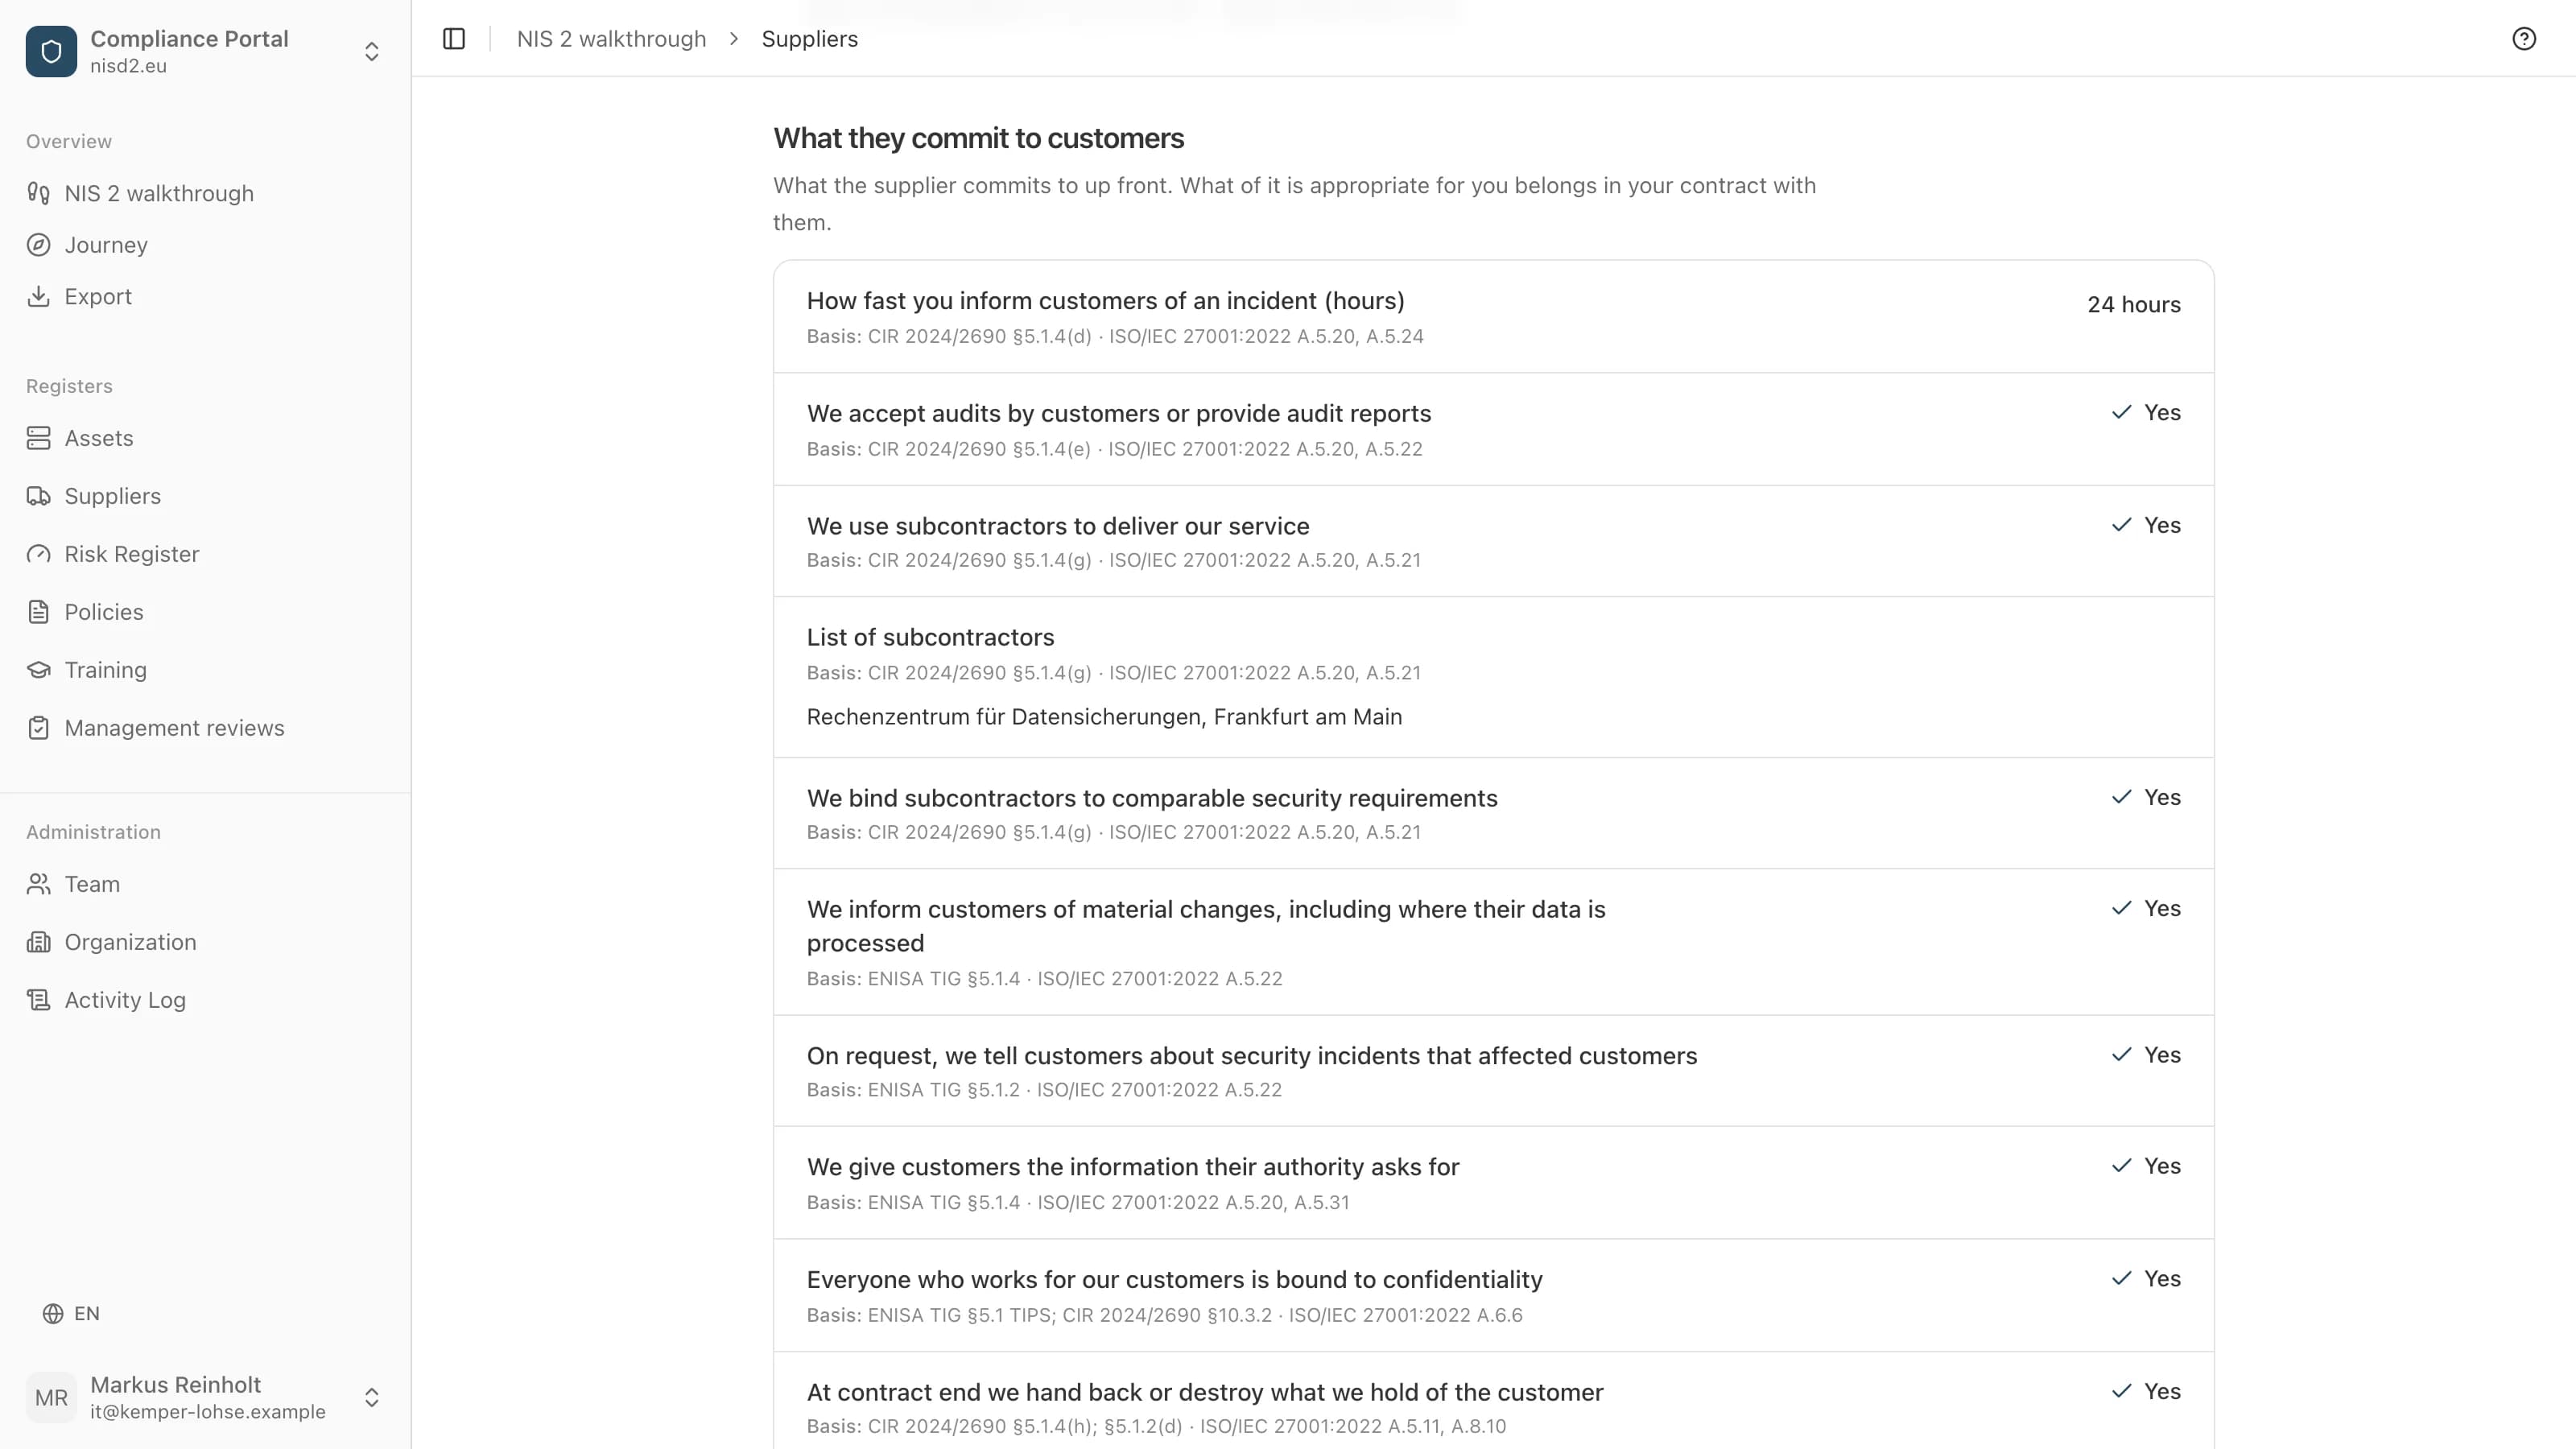
- 5
Change it in one place
When a subcontractor is added or an answer changes, you change it once in the portal. Every customer always reads the current version, with the day of your last change.
What you are asked depends on what you reach at your customers.
Every supplier answers 21 questions. On your profile you say whether you hold your customers' data, access their systems or enter their premises, and whether you offer software as a service, ship software or run IT for customers. The rest follows from that. A supplier that reaches data, systems or premises also answers on confidentiality, on the suitability of staff with access, and on hand-back at the end of the contract.
Your customers' data
Where the data is processed, the data processing agreement, encryption at rest and in transit. Plus how you manage security: ISMS, certificate, vulnerability handling, plans for incidents and outages, a second factor for your own administrator accounts.
Your customers' systems
Personal accounts with a second factor for every access, remote maintenance included, and a log of access with administrator rights. Plus the same security management as for customer data.
Your customers' premises
How you keep track of keys, badges and codes, and which written rules of conduct your staff follow on site. A supplier that only enters premises is not asked about an ISMS, security testing or administrator accounts.
Software and managed services
If you offer software as a service or ship software: secure development, a published way to report security holes, independent security testing. For SaaS also a second factor for your customers and the time to restore service; for shipped software how long you supply security updates, an SBOM and signed releases. If you run IT for customers, you answer the questions on security testing and security management.
A cleaning company with keys sees 26 questions this way, a SaaS provider that holds customer data 39.
„Wir begrüßen aktuelle Vorstöße der Wirtschaft, einen einheitlichen Fragenkatalog für Lieferanten zu erarbeiten, der die Erfüllung der Anforderungen belegt.“
We welcome current initiatives from industry to develop a uniform catalogue of questions for suppliers that demonstrates the requirements are met.
This questionnaire is one such initiative: uniform, open and free to reuse. Suppliers answer it once, and every customer reads the same answers when it manages the security of its supply chain under Art. 21(2)(d) NIS 2.
Only for customers you invite
Your answers are seen only by the customers you invite or whose request you accept. No public profile page, nothing for search engines. Hosted in the EU, with the code open on GitHub.
Start with your profile
Sign in, enter your company name, then answer the questionnaire at your own pace. You invite your customers only when you are ready.
Create supplier profileMore on nisd2.eu
- Supplier portal
What else the portal does: invite customers, store certificates, report incidents.
- Every question with its basis
The whole questionnaire to read, and as a PDF, for Word and as an open schema.
- Open source
The full source code under AGPL-3.0 on GitHub.
Open source
The platform is open source and free to host yourself. We earn from the guided walkthrough, not from your data. The code and schemas are open on GitHub, so you can check for yourself. Everything exportable, no lock-in.