For suppliers to companies under NIS 2
Answer one security questionnaire, share it with every customer
Companies under NIS 2 have to manage the security of their supply chain, so they ask their suppliers. You answer one questionnaire, once, and every customer reads the same answers. Free for suppliers.
Programas y membresías
How the questionnaire works
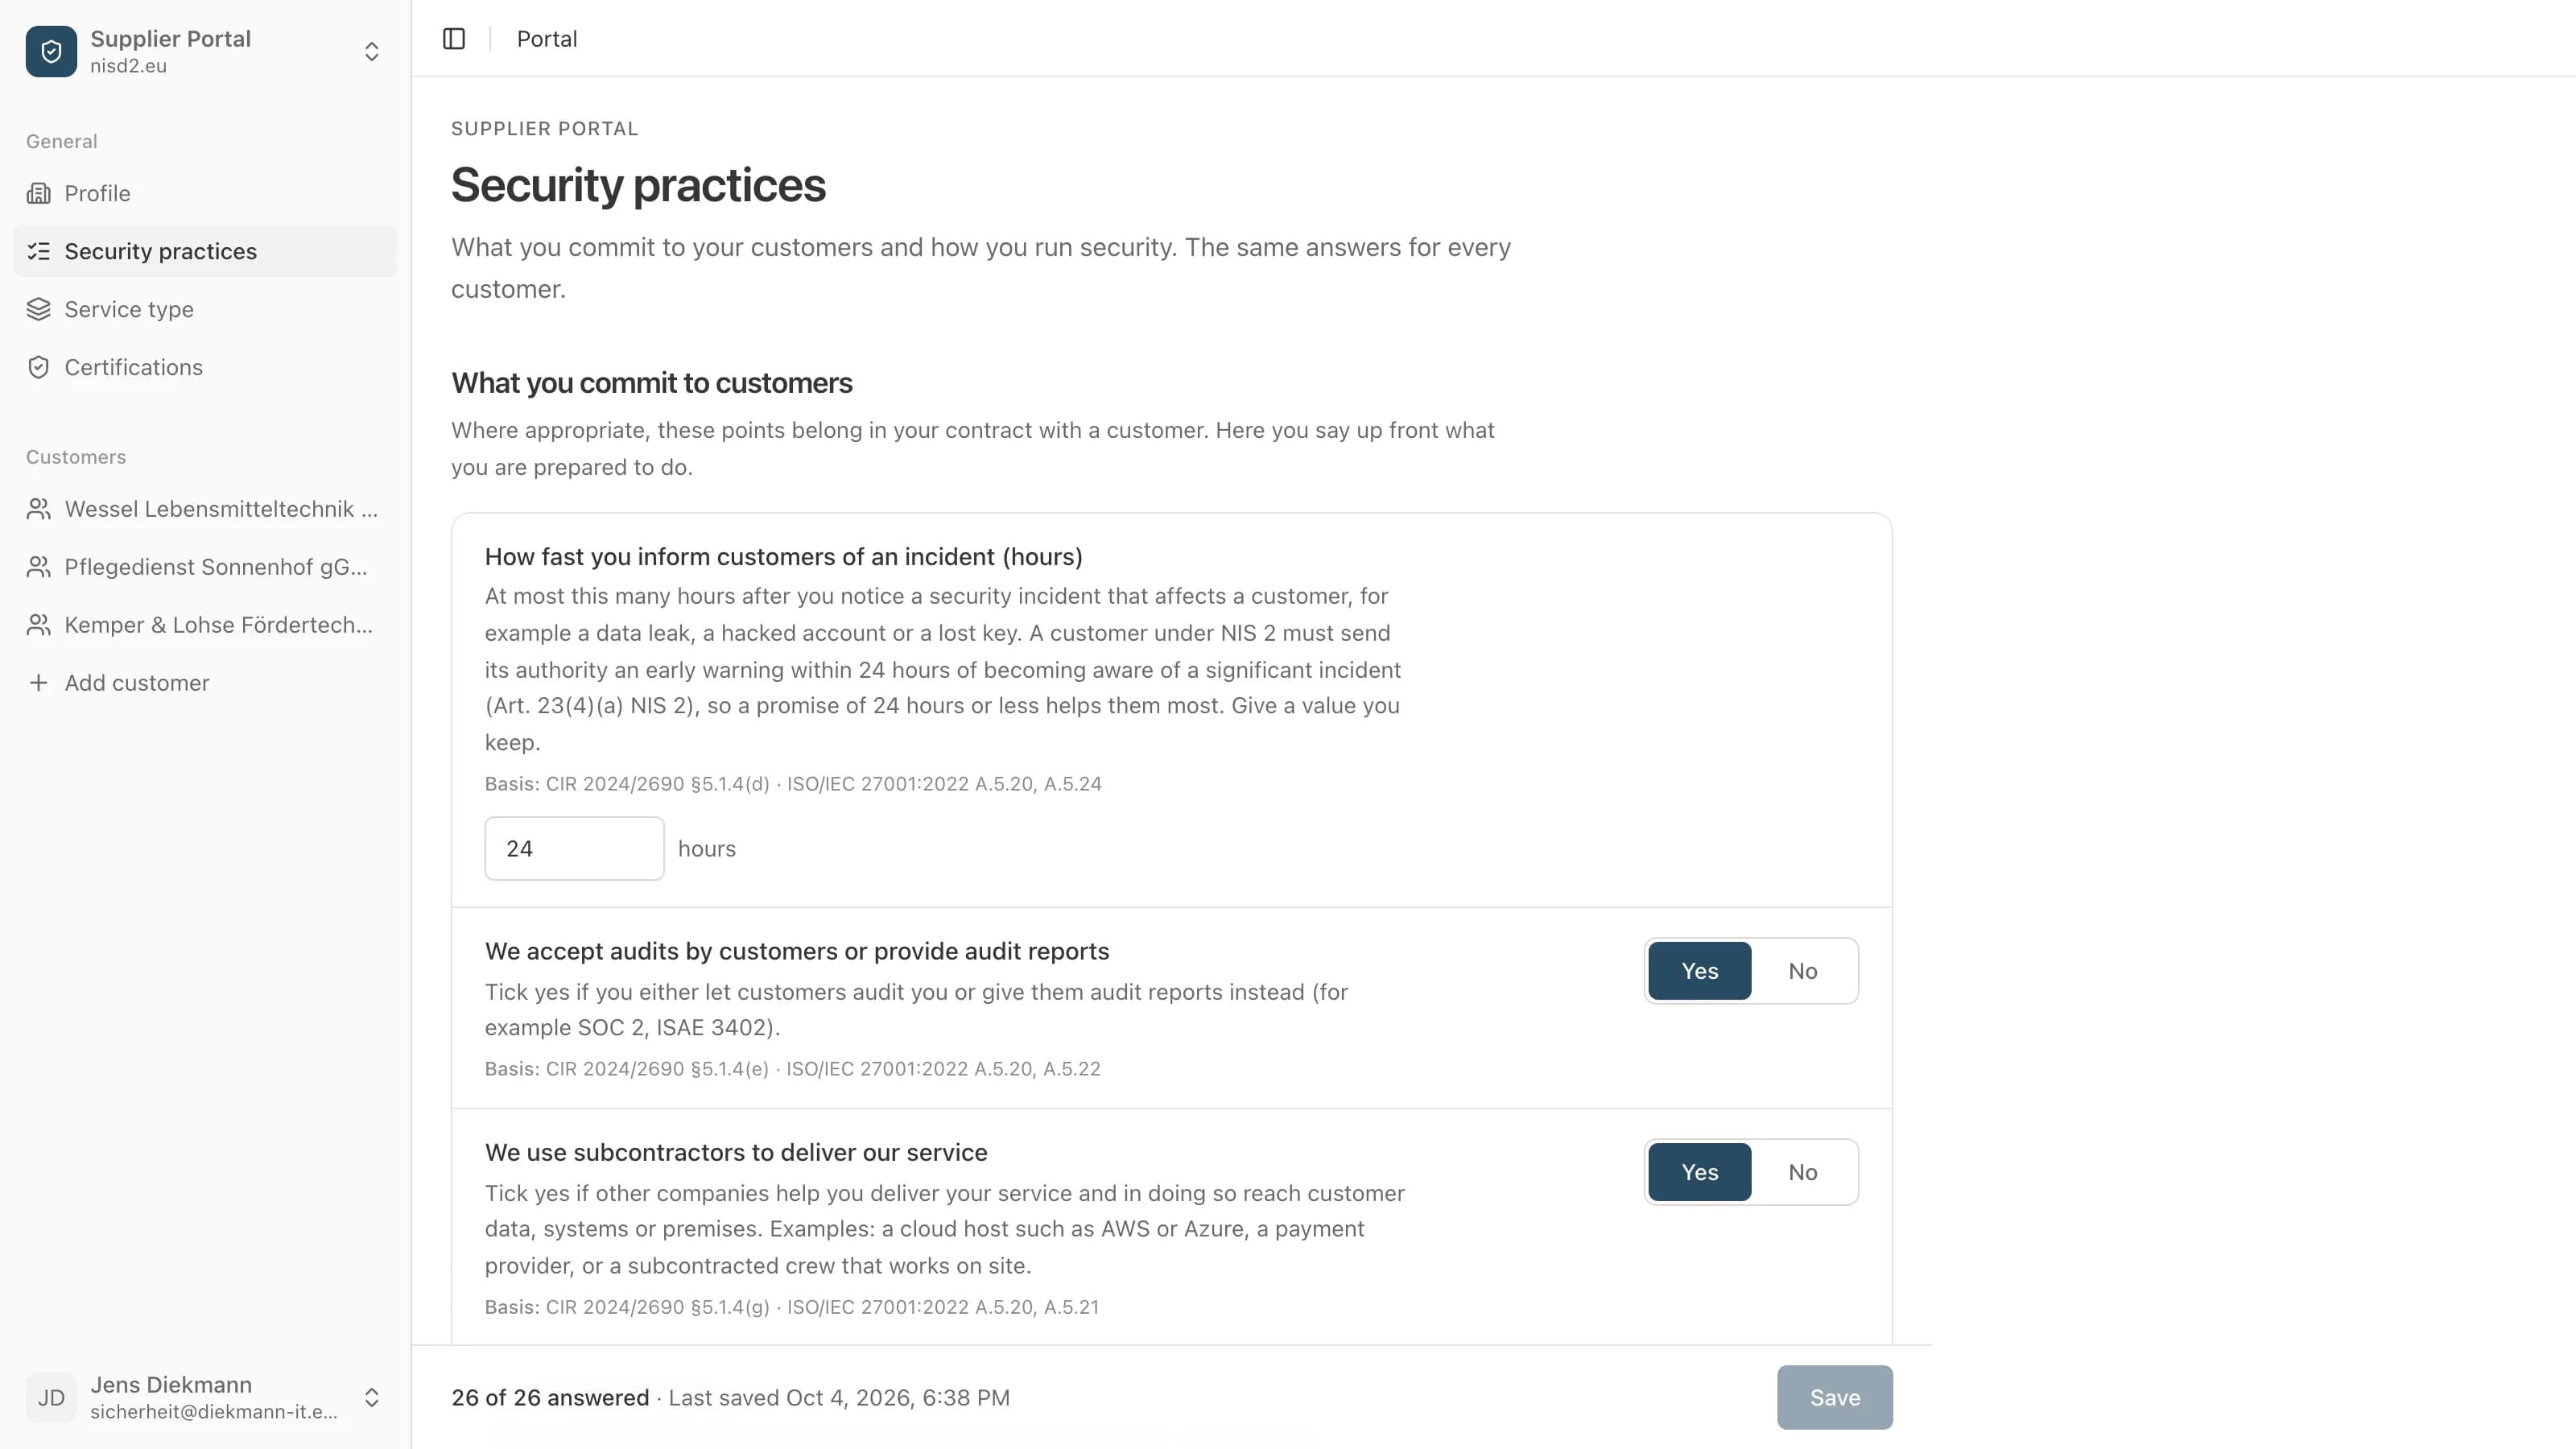
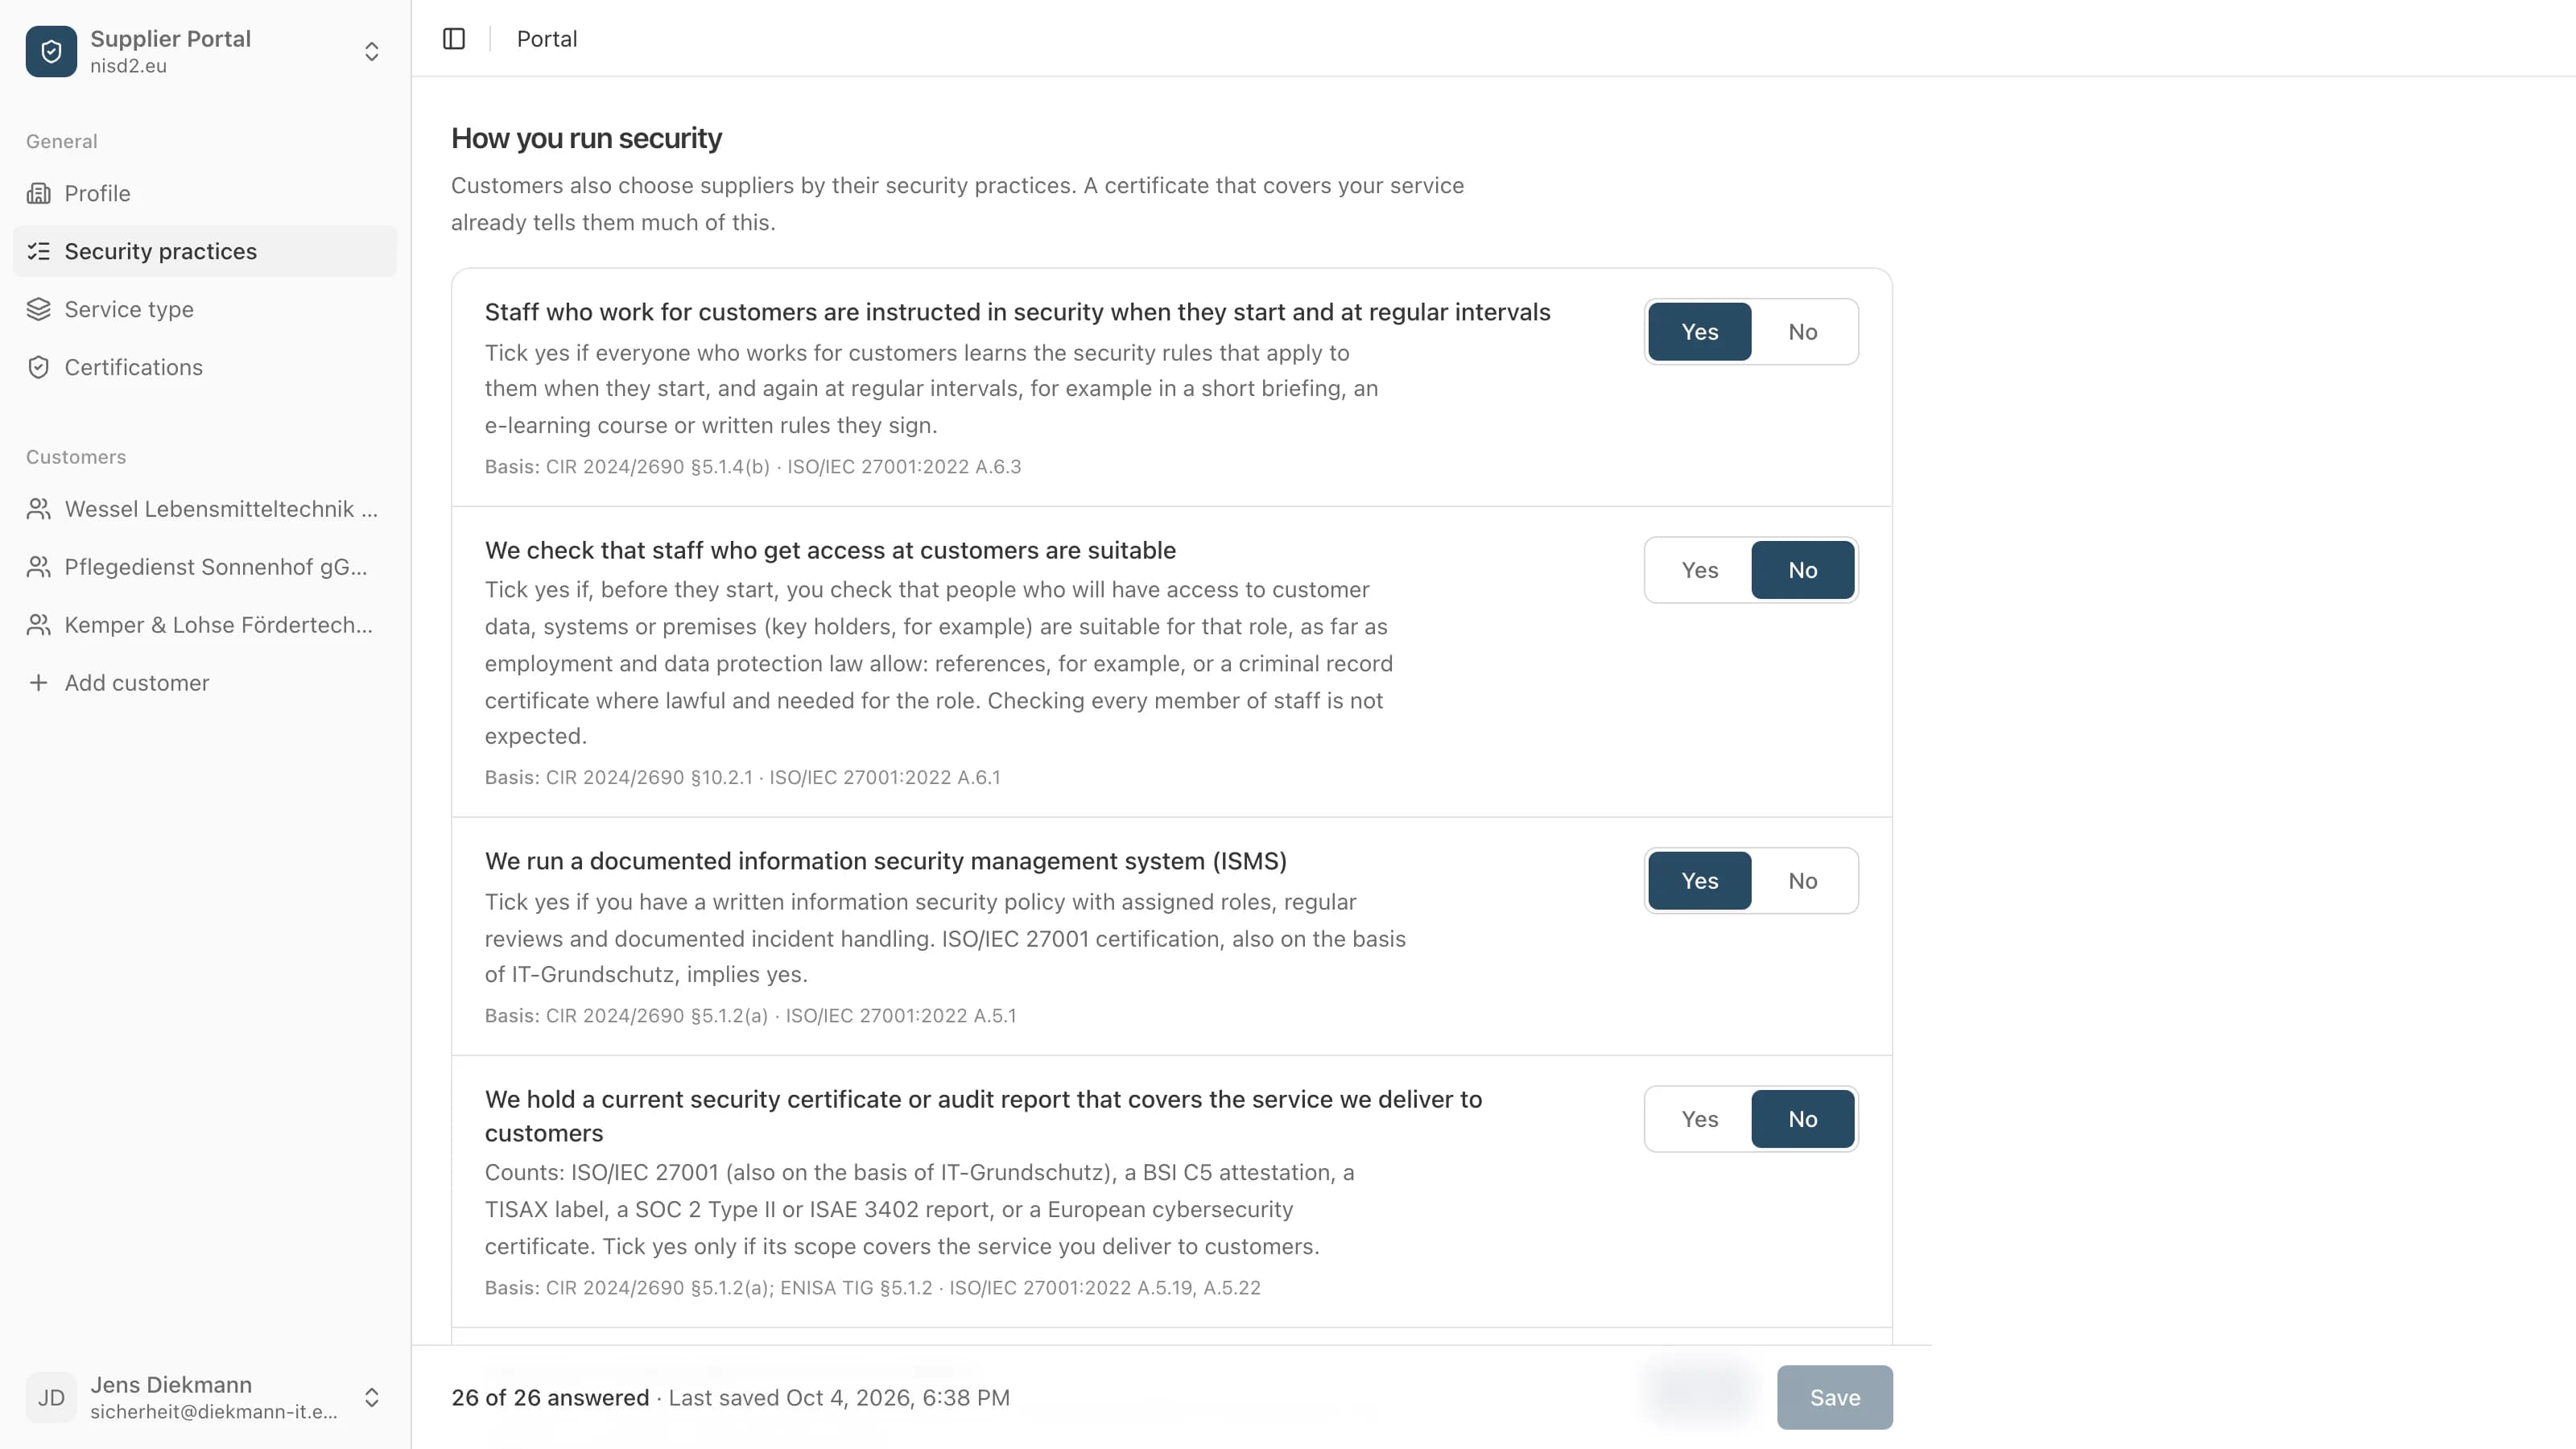
Every picture shows the real app, filled in for made-up sample companies.
- 1
Only the questions that fit you
First you say whether you hold your customers' data, access their systems or enter their premises, and what service you provide. After that you see only the questions that belong to it, and none that do not apply to your service.
- 2
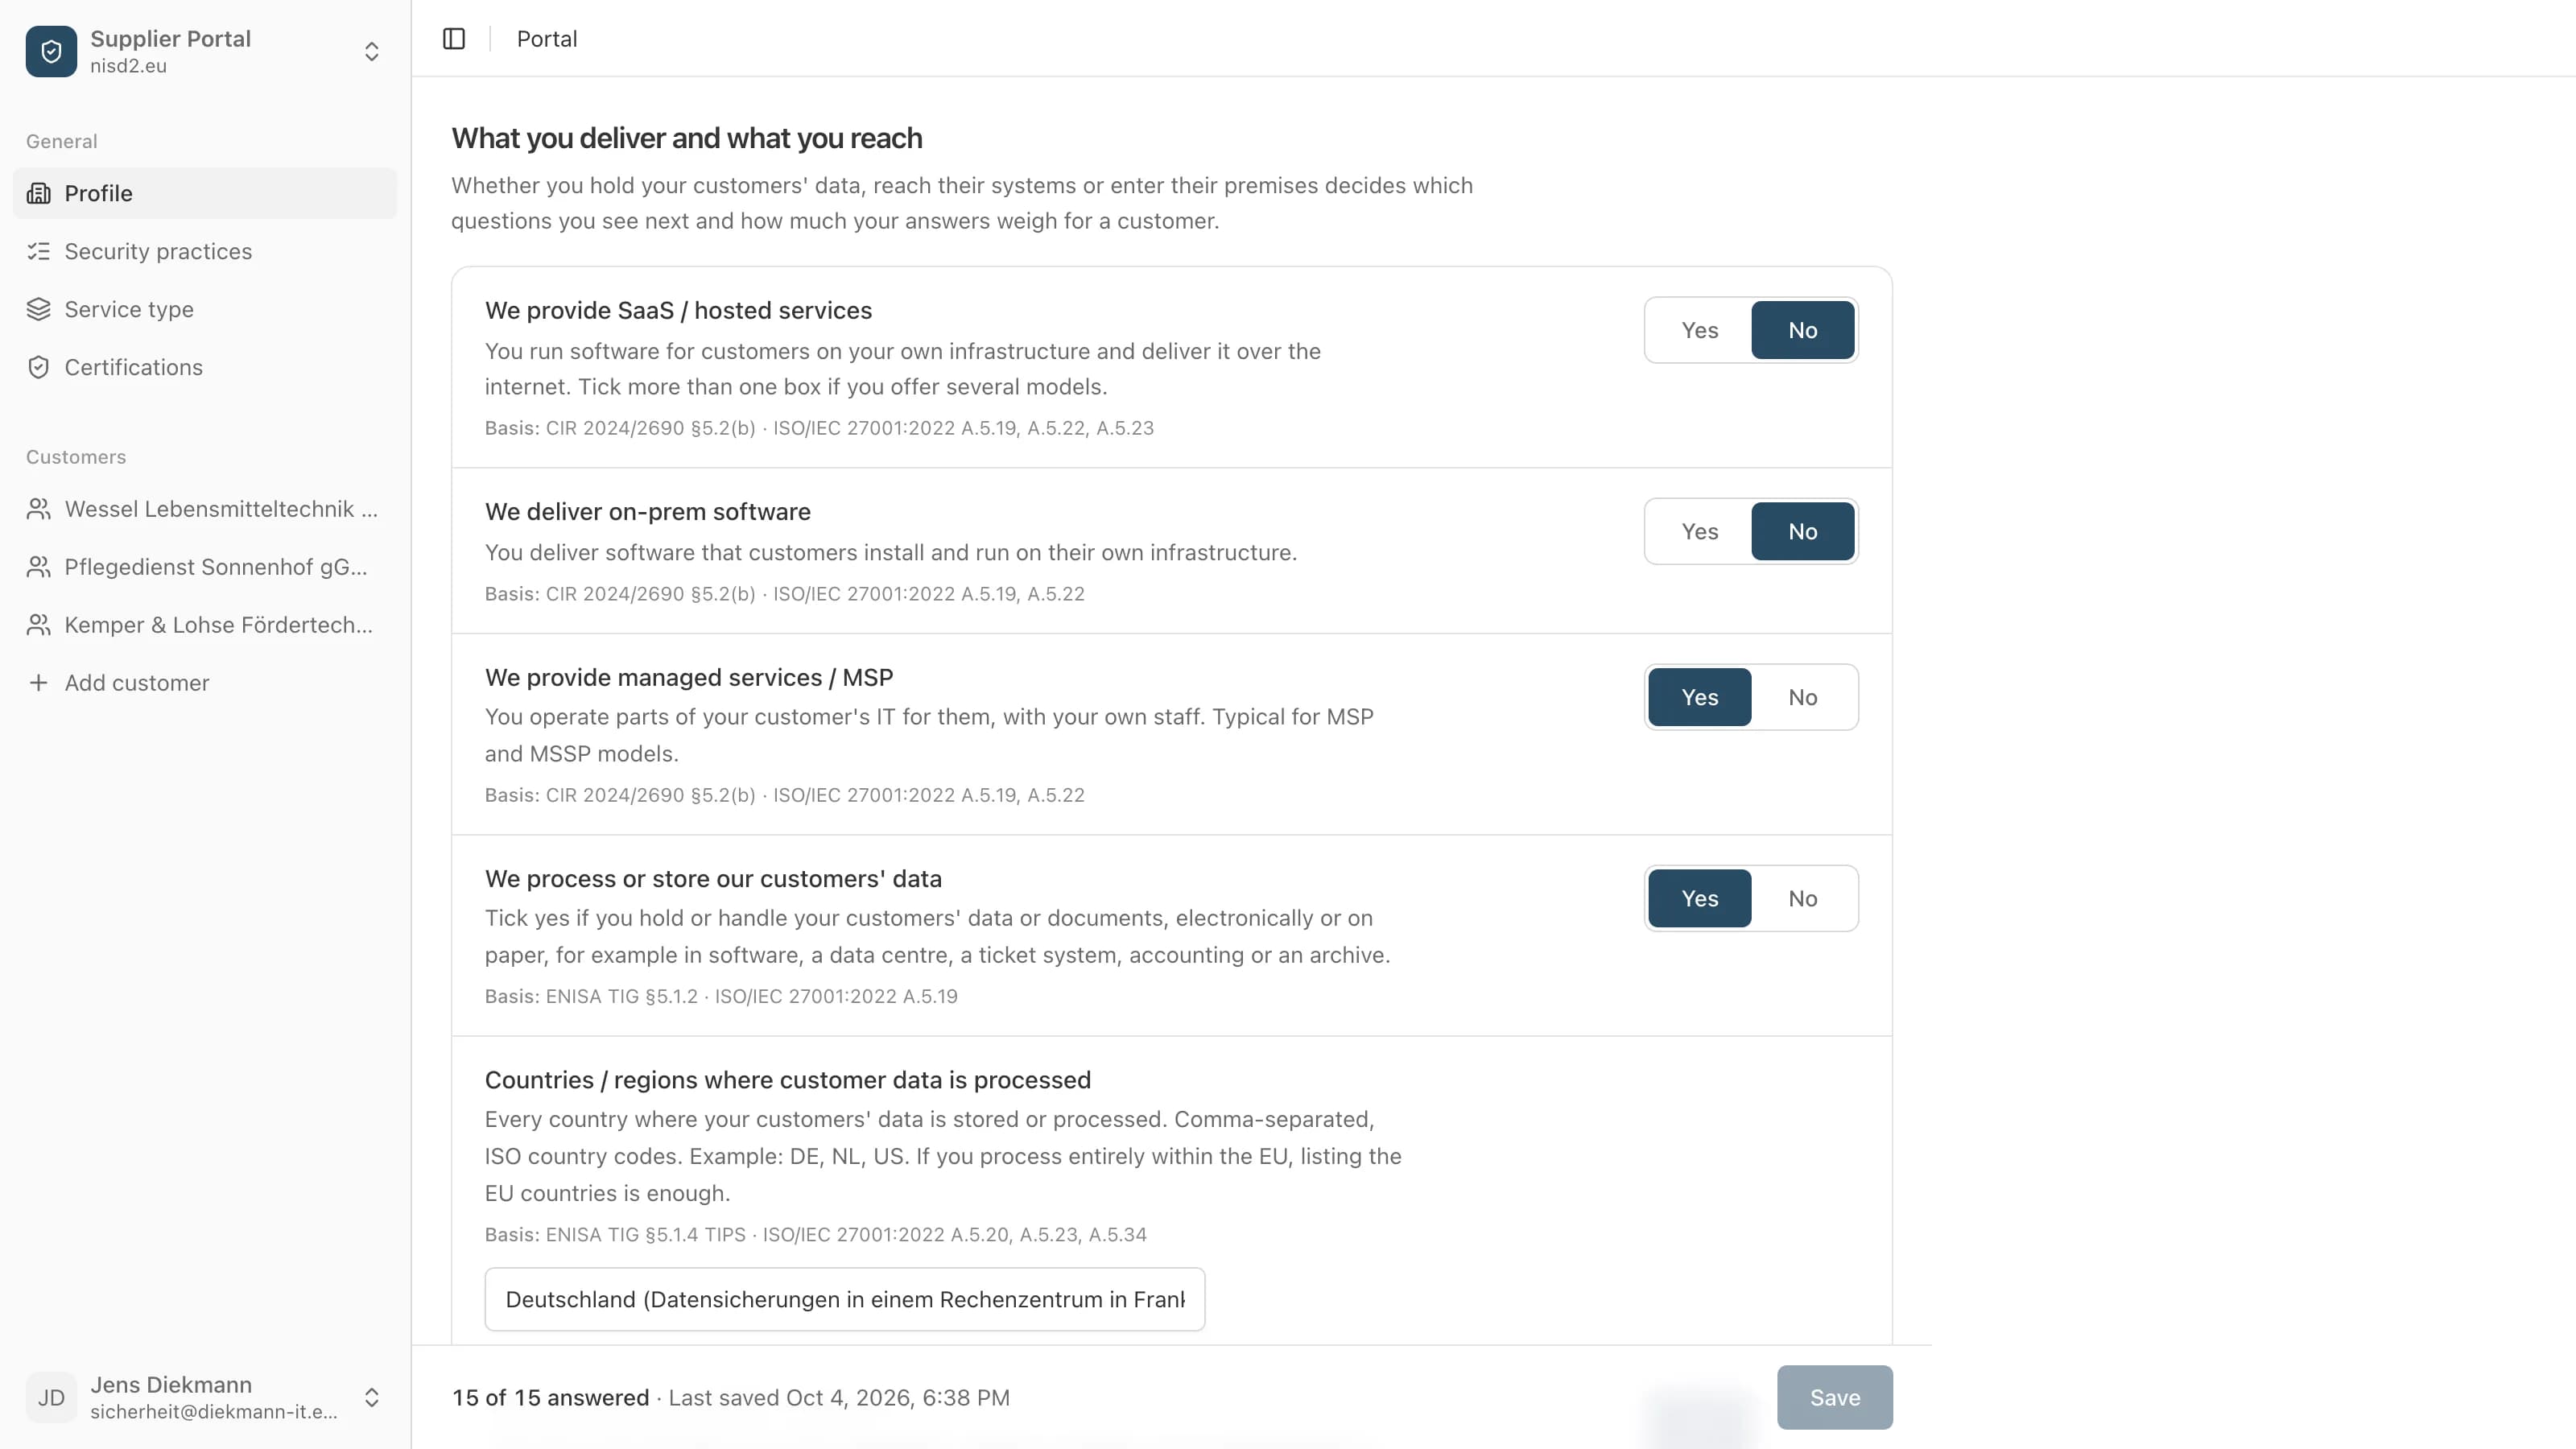
Every question says when to tick yes
Under each question it says in plain words what is meant, with examples. Below that, what the question rests on, mostly a paragraph of Implementing Regulation (EU) 2024/2690, and the matching ISO/IEC 27001:2022 control where there is one.
- 3
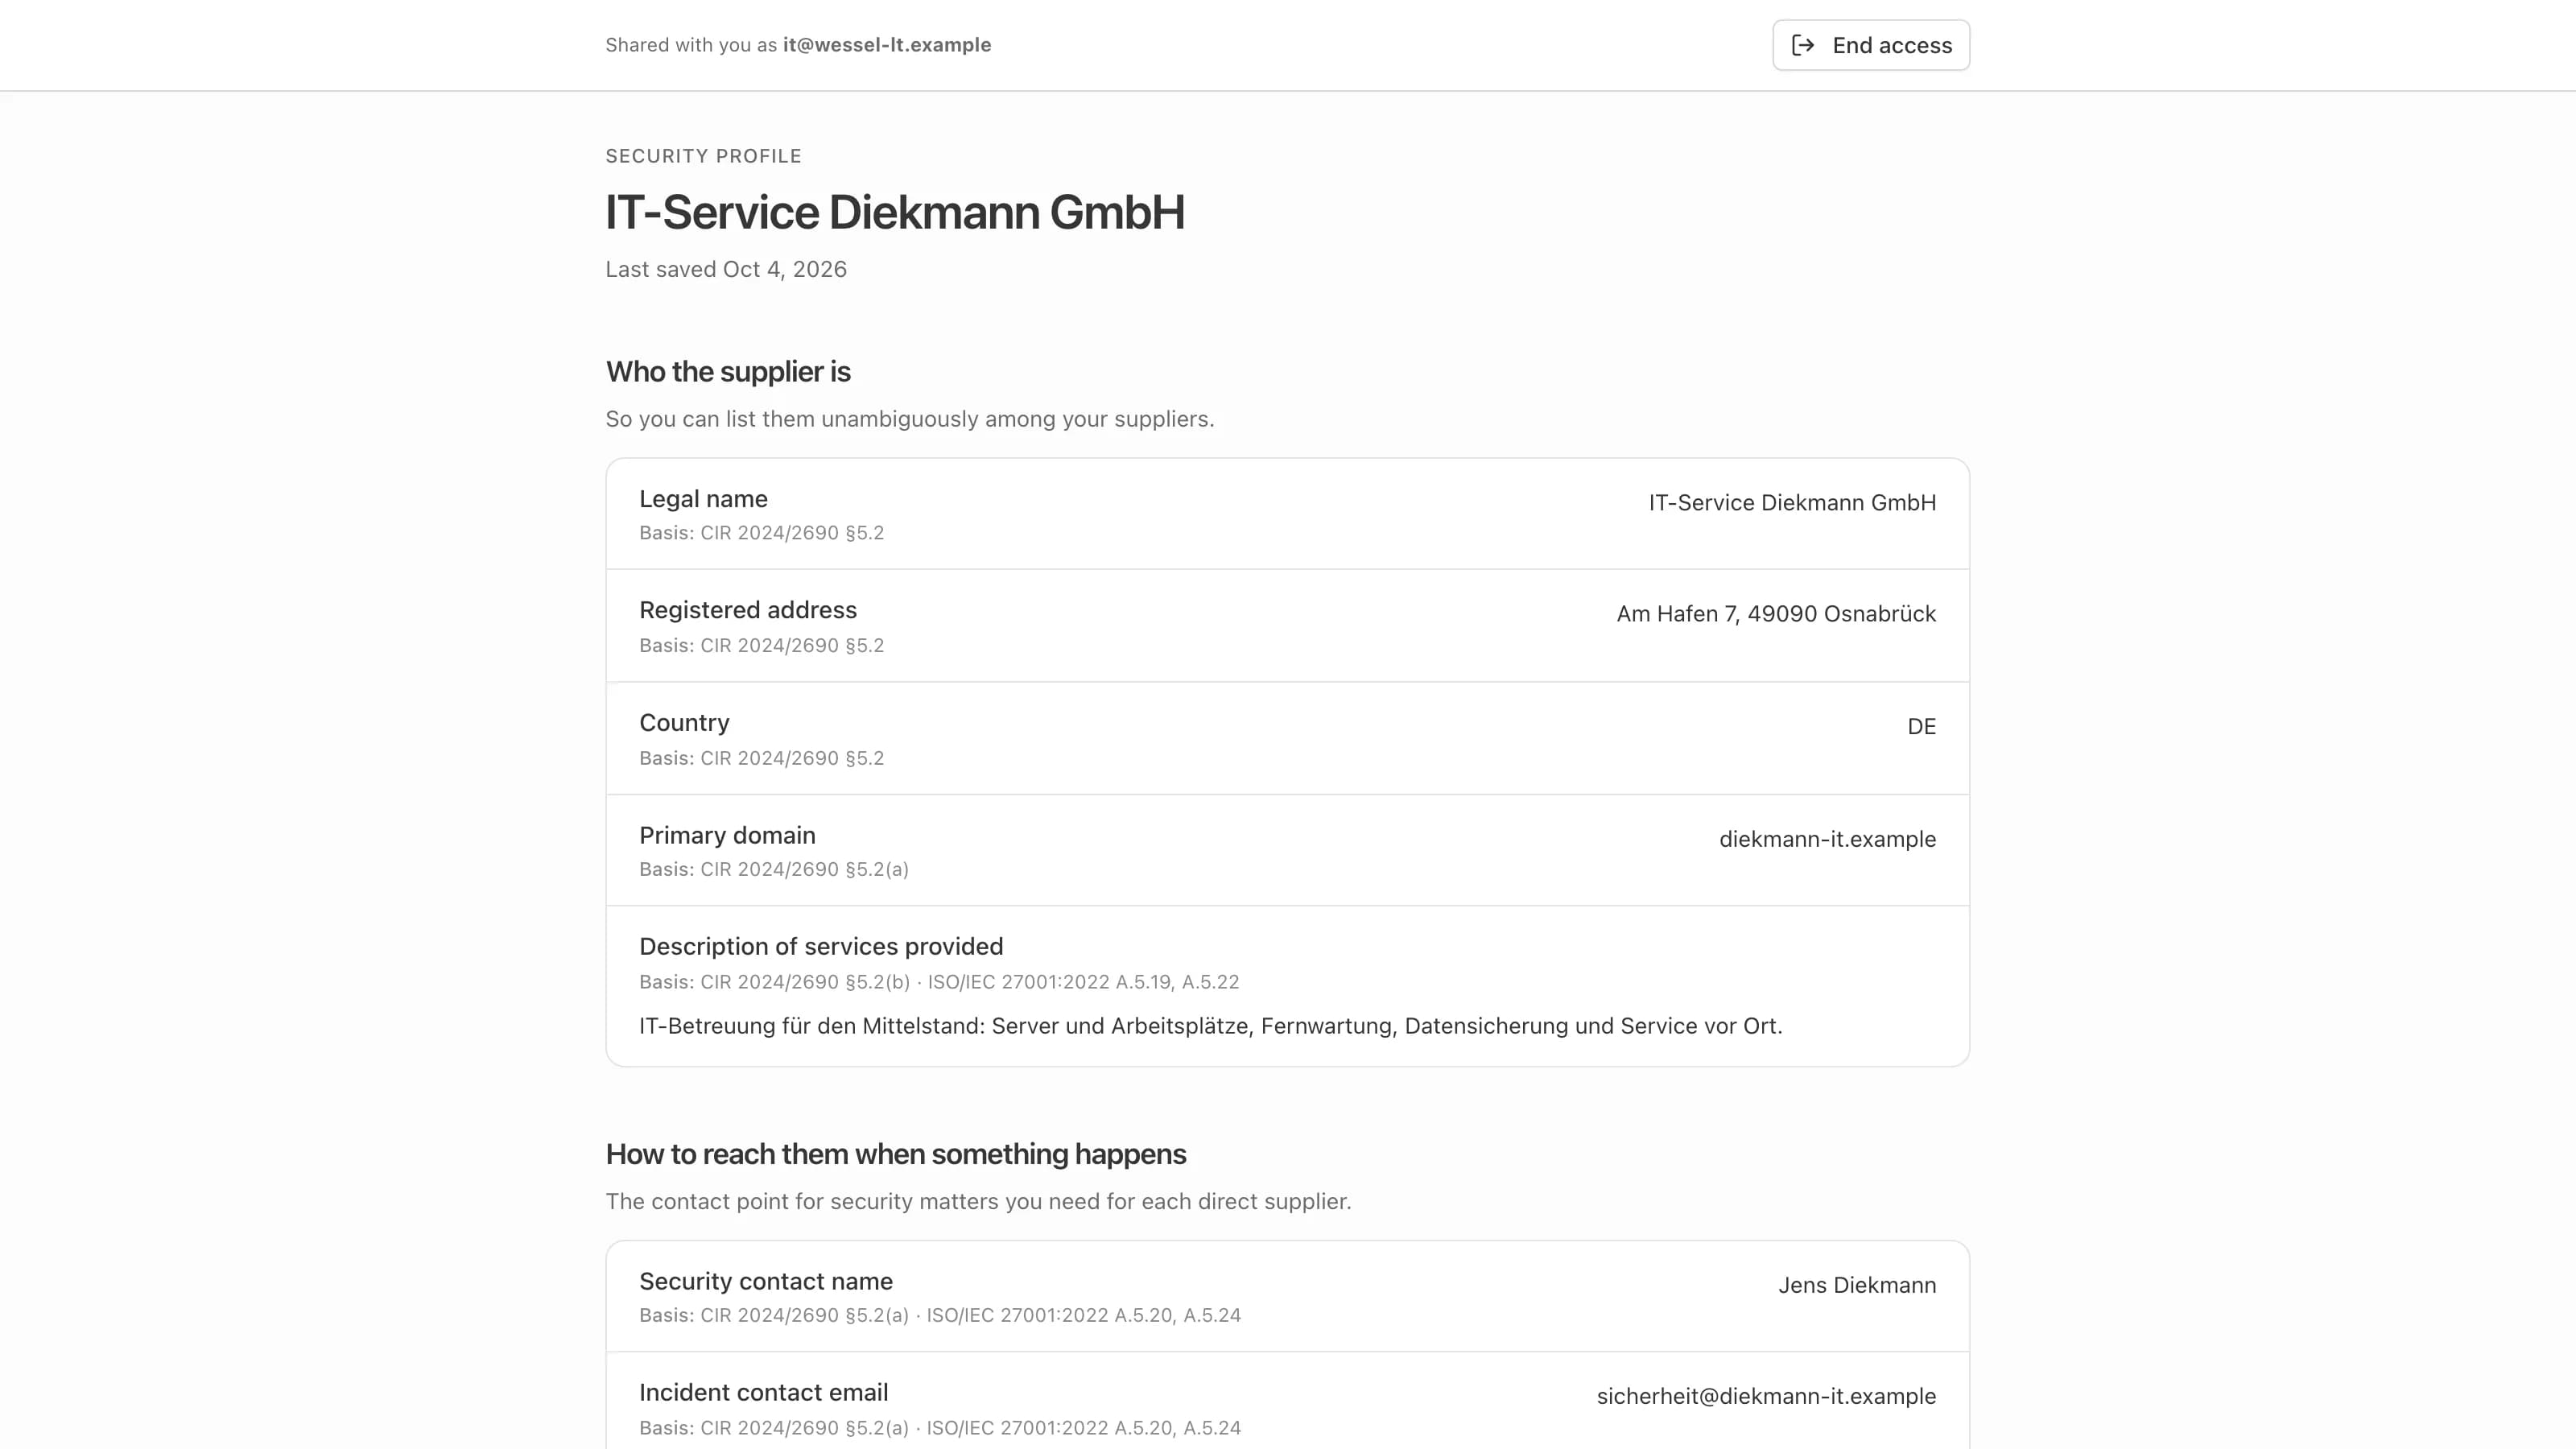
Answer once, show every customer
You invite your customers by email. Each opens your answers through a link of their own, without creating an account, and reads the same answers as everyone else. Nothing is public: no profile page, nothing for search engines. You can take the access back at any time.
- 4
Customers on nisd2.eu have you in their supplier register
If your customer uses nisd2.eu itself, it requests your answers in the portal. From then on it opens them from its supplier register, where it keeps its suppliers under NIS 2.
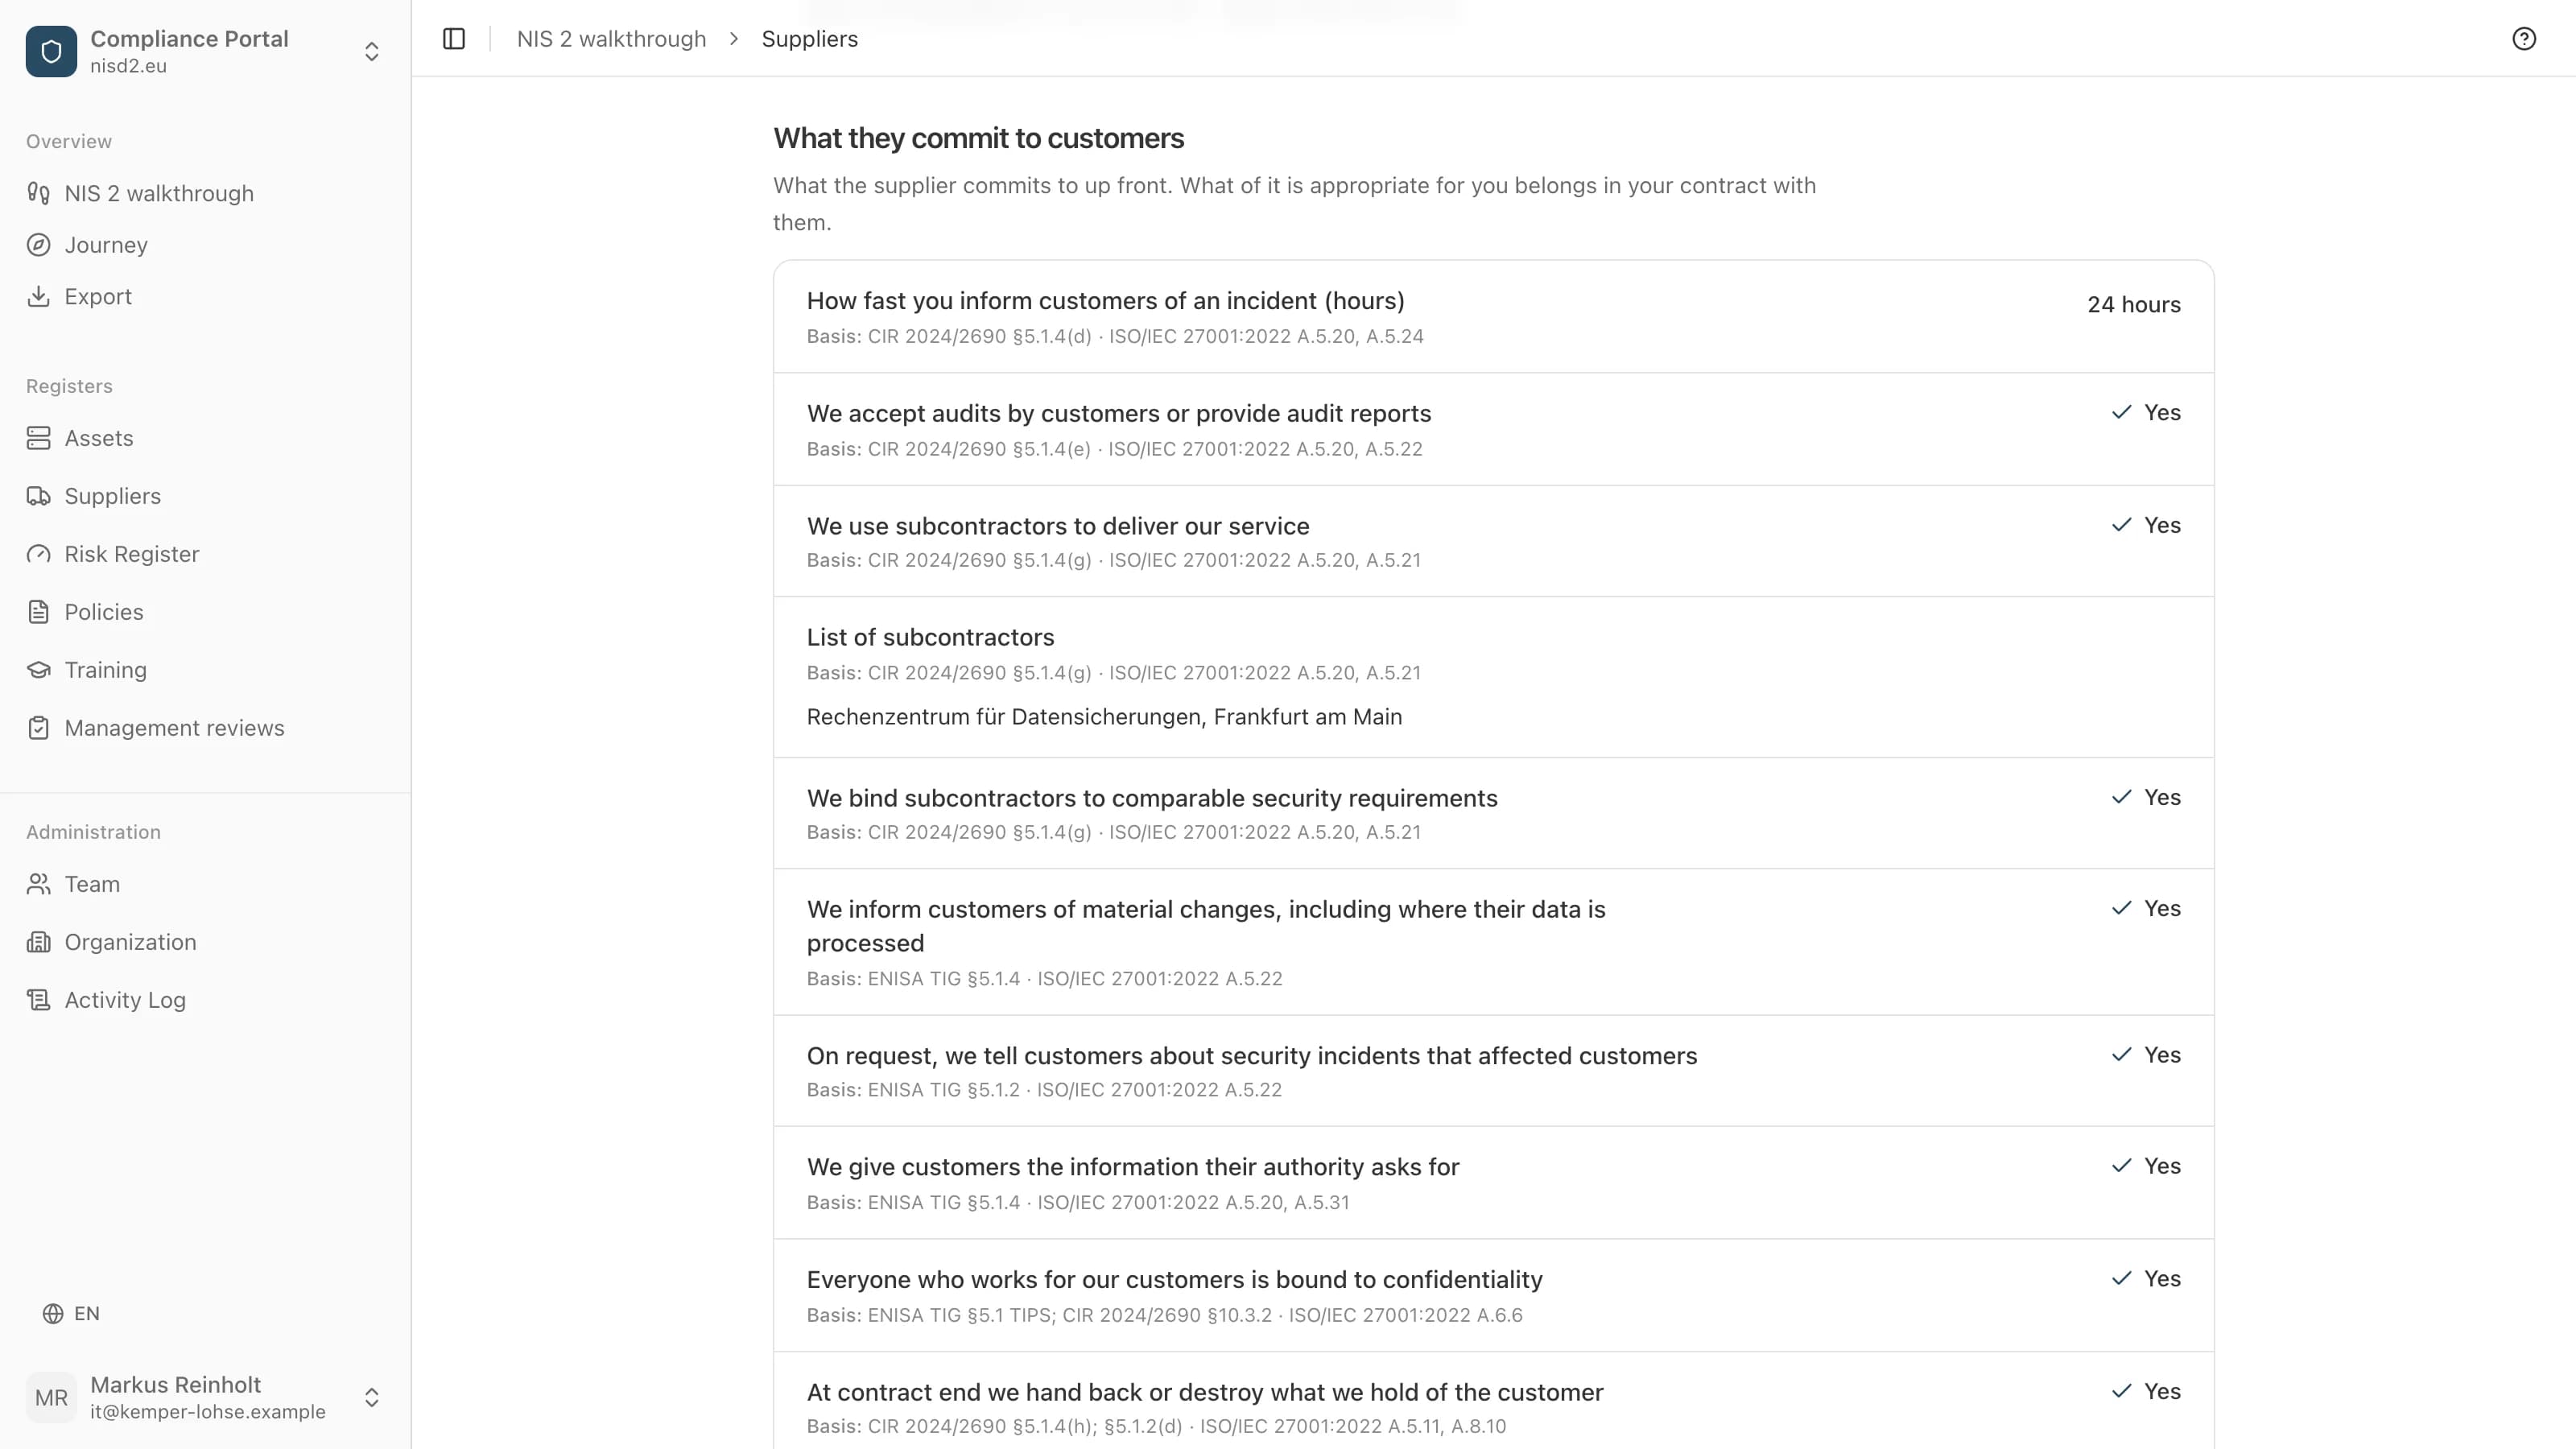
- 5
Change it in one place
When a subcontractor is added or an answer changes, you change it once in the portal. Every customer always reads the current version, with the day of your last change.
Lo que se le pregunta depende de a qué accede en sus clientes.
Todo proveedor responde 21 preguntas. En su perfil indica si conserva datos de sus clientes, accede a sus sistemas o entra en sus instalaciones, y si ofrece software como servicio, entrega software o gestiona la TI de sus clientes. El resto se deriva de ello. Un proveedor que accede a datos, sistemas o instalaciones responde además sobre confidencialidad, la idoneidad del personal con acceso y la devolución al final del contrato.
Los datos de sus clientes
Dónde se tratan los datos, el acuerdo de tratamiento de datos, cifrado en reposo y en tránsito. Además, cómo gestiona la seguridad: SGSI, certificado, gestión de vulnerabilidades, planes para incidentes e interrupciones, un segundo factor para sus propias cuentas de administrador.
Los sistemas de sus clientes
Cuentas personales con un segundo factor para cada acceso, incluido el mantenimiento remoto, y un registro de los accesos con derechos de administrador. Además, la misma gestión de la seguridad que para los datos de clientes.
Las instalaciones de sus clientes
Cómo controla las llaves, tarjetas y códigos y qué normas de conducta escritas sigue su personal in situ. A un proveedor que solo entra en instalaciones no se le pregunta por un SGSI, pruebas de seguridad ni cuentas de administrador.
Software y servicios gestionados
Si ofrece software como servicio o entrega software: desarrollo seguro, una vía publicada para comunicar fallos de seguridad, pruebas de seguridad independientes. En SaaS, además, un segundo factor para sus clientes y el tiempo de restablecimiento del servicio; en el software entregado, hasta cuándo suministra actualizaciones de seguridad, una SBOM y versiones firmadas. Si gestiona la TI de sus clientes, responde a las preguntas sobre pruebas de seguridad y gestión de la seguridad.
Una empresa de limpieza con llaves ve así 26 preguntas, un proveedor de SaaS que conserva datos de clientes 39.
„Wir begrüßen aktuelle Vorstöße der Wirtschaft, einen einheitlichen Fragenkatalog für Lieferanten zu erarbeiten, der die Erfüllung der Anforderungen belegt.“
We welcome current initiatives from industry to develop a uniform catalogue of questions for suppliers that demonstrates the requirements are met.
This questionnaire is one such initiative: uniform, open and free to reuse. Suppliers answer it once, and every customer reads the same answers when it manages the security of its supply chain under Art. 21(2)(d) NIS 2.
Only for customers you invite
Your answers are seen only by the customers you invite or whose request you accept. No public profile page, nothing for search engines. Hosted in the EU, with the code open on GitHub.
Start with your profile
Sign in, enter your company name, then answer the questionnaire at your own pace. You invite your customers only when you are ready.
Create supplier profileMore on nisd2.eu
- Supplier portal
What else the portal does: invite customers, store certificates, report incidents.
- Every question with its basis
The whole questionnaire to read, and as a PDF, for Word and as an open schema.
- Open source
The full source code under AGPL-3.0 on GitHub.
Open source
La plataforma es open source y gratuita si la aloja usted mismo. Obtenemos ingresos de la implementación guiada, no de sus datos. El código y los esquemas están abiertos en GitHub, para que pueda comprobarlo usted mismo. Todo exportable, sin lock-in.